 Ukdefencejournal.Uk
British Drone Intercepts Attack Drones in Pentagon Experiment
Article Content

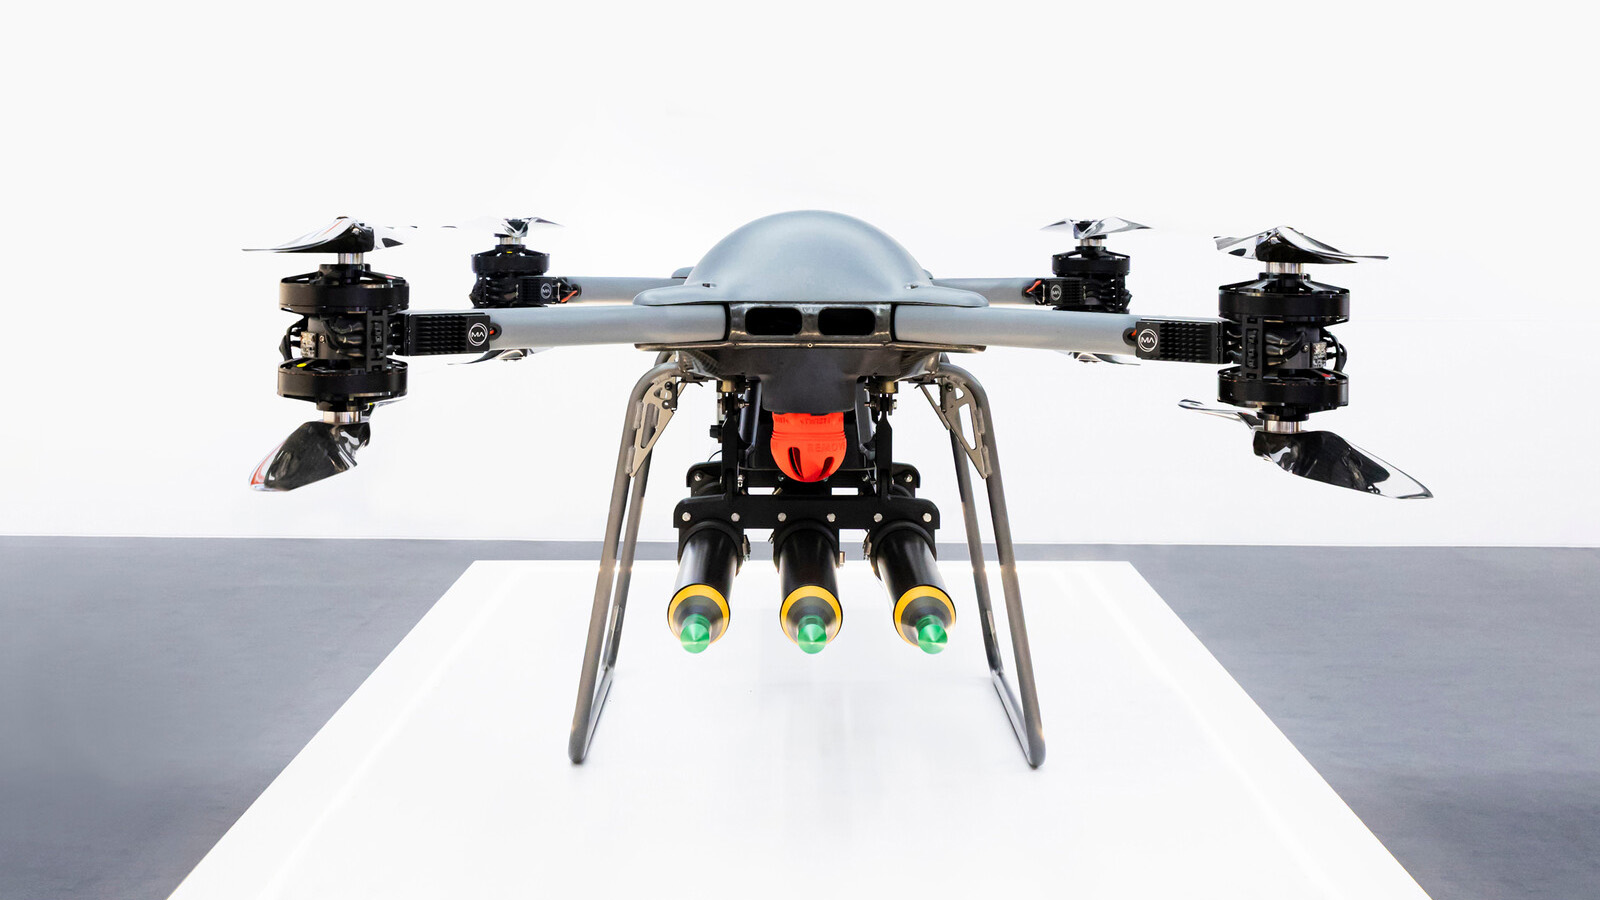
- •The TRV-150 drone intercepted multiple attack drones using APKWS rockets.
- •The Pentagon experiment demonstrated the drone's capability to engage several targets without reloading.
- •BAE Systems plans to adapt this technology for maritime defense.
A modified Malloy Aeronautics T-150 drone, designated TRV-150, successfully intercepted multiple one-way attack drones during a Pentagon experiment at Eglin Air Force Base from September 21 to 25, 2026. The drone, equipped with a three-pod launcher of BAE Systems’ APKWS laser-guided rockets, engaged several targets in succession without needing to land or reload. This test was part of the Joint Readiness Experimentation exercise run by the U.S. Office of the Under Secretary for Research and Engineering. BAE Systems aims to adapt this technology for naval defense against drone threats. The APKWS system enhances the precision of unguided rockets, making them a cost-effective solution for countering drone attacks. The TRV-150's ability to fire multiple rockets in one sortie is crucial given the tendency for attack drones to operate in groups. The trials build on previous tests conducted in July 2025, where the drone successfully fired a single APKWS rocket.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track BAE Systems in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is the TRV-150's role?
How does APKWS improve drone capabilities?
What were the outcomes of the Pentagon experiment?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…