 News.Cgtn
China Advances Draft Law on Cross-Border Anti-Corruption
Article Content

- •China's draft law targets cross-border corruption with a focus on global governance.
- •Chinese companies must establish compliance departments under the new law.
- •The legislation aims to enhance international cooperation and oversight against corruption.
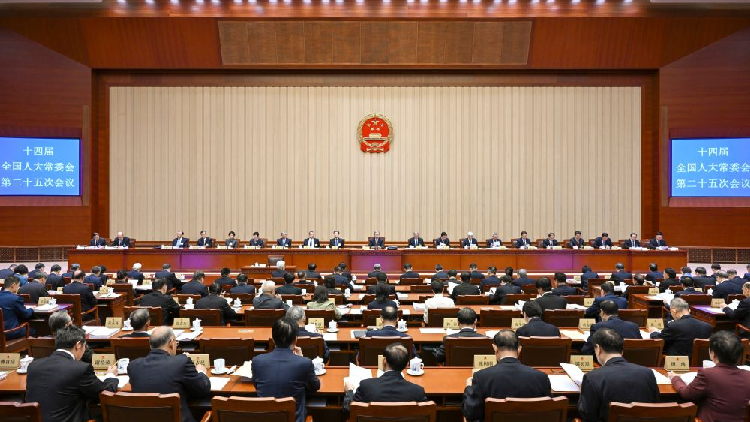
On November 2, 2026, China's National People's Congress began deliberating a draft law aimed at combating cross-border corruption. The law emphasizes the creation of a fair global anti-corruption governance system and includes provisions for using information technology in anti-corruption efforts. It mandates that Chinese companies operating internationally establish integrity and compliance departments. The draft law is part of China's broader strategy to enhance its legal framework for anti-corruption and improve international cooperation, having already repatriated 963 fugitives in 2025. The legislation is structured into six chapters and 47 articles, detailing principles and procedures for oversight and enforcement. The law aims to address both the symptoms and root causes of corruption, promoting a systematic approach to governance. This legislative effort reflects China's ongoing commitment to strengthening its legal system and international standing in anti-corruption initiatives.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What does the draft law entail?
How does this law affect international businesses?
What has been China's recent approach to anti-corruption?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…