 Taipeitimes
China Increases Maritime Harassment Amid Regional Tensions
Article Content

- •Taiwan's CGA reports increased Chinese patrol harassment of shipping vessels.
- •The situation is linked to broader geopolitical tensions involving North Korea and regional military exercises.
- •Shipping companies are advised to remain vigilant and report harassment incidents.
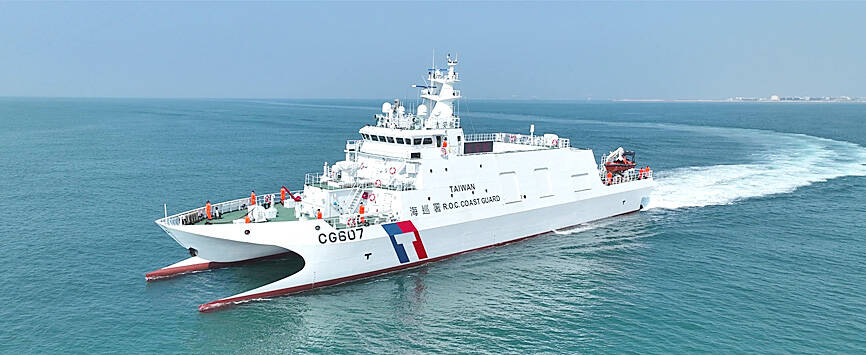
The Coast Guard Administration (CGA) of Taiwan reported increased harassment of shipping vessels by Chinese patrols along Taiwan's east coast. This escalation is part of ongoing tensions in the region, particularly following recent military exercises by China. The CGA has urged shipping companies to remain vigilant and report any incidents of harassment. The situation is exacerbated by the backdrop of heightened military readiness and geopolitical maneuvers involving the US, South Korea, and Japan, who are focused on North Korea's denuclearization. The CGA's warning comes as Taiwan's maritime security is under scrutiny, with potential impacts on trade and shipping routes. No specific incidents of cyber exploitation or attacks were mentioned in the articles, focusing instead on physical maritime threats.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What specific incidents of harassment have been reported?
How are shipping companies advised to respond?
What is the broader geopolitical context of this situation?
Continue Reading
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…
 Chinese Actor Compromises US Government Networks via PHP2Shell Exploit A suspected Chinese nation-state actor exploited vulnerabilities in Palo Alto Networks firewalls using a chained PHP2Shell exploit and a Linux kernel privilege escalation flaw. The attack, which began on October 23, targeted 25 servers across the US, Japan, Taiwan, and South Korea, with a focus on US…