 Menafn
China Suspected in Cyberattack on Swiss Space Firm Beyond Gravity
Article Content

- •Beyond Gravity suspects a cyberattack by China, affecting its satellite and rocket technology operations.
- •The attack is believed to involve data theft, though specific details on the compromised information are not confirmed.
- •This incident follows a historical pattern of cyberattacks on Ruag International AG, highlighting ongoing geopolitical tensions.
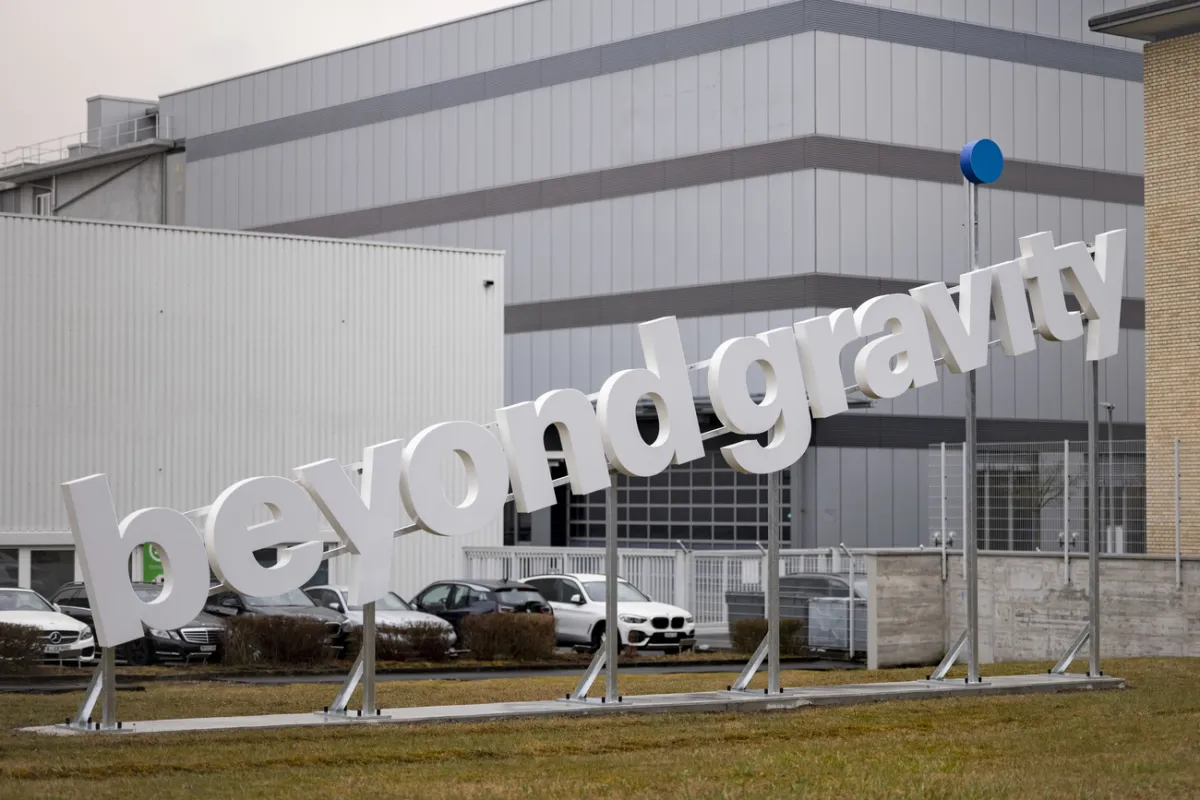
Swiss public television SRF reports that Beyond Gravity, a state-owned Swiss space company, suspects a cyberattack attributed to China. The attack, described as targeted and executed by a 'highly professional actor', was reported earlier this month. Beyond Gravity has filed a criminal complaint regarding the incident, which is currently being investigated by the Federal Department of Defense and the Federal Office for Cybersecurity. While the company has not officially confirmed the attribution to China, internal sources suggest a strong belief in this assessment. Data breaches are suspected, but the exact information compromised remains unclear. Beyond Gravity is part of Ruag International AG, which faced a similar cyberattack over a decade ago, previously attributed to Russia. The Office of the Attorney General has yet to take action on this latest incident.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Beyond Gravity in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What type of data was compromised?
What actions are being taken in response?
How does this relate to past incidents?
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…