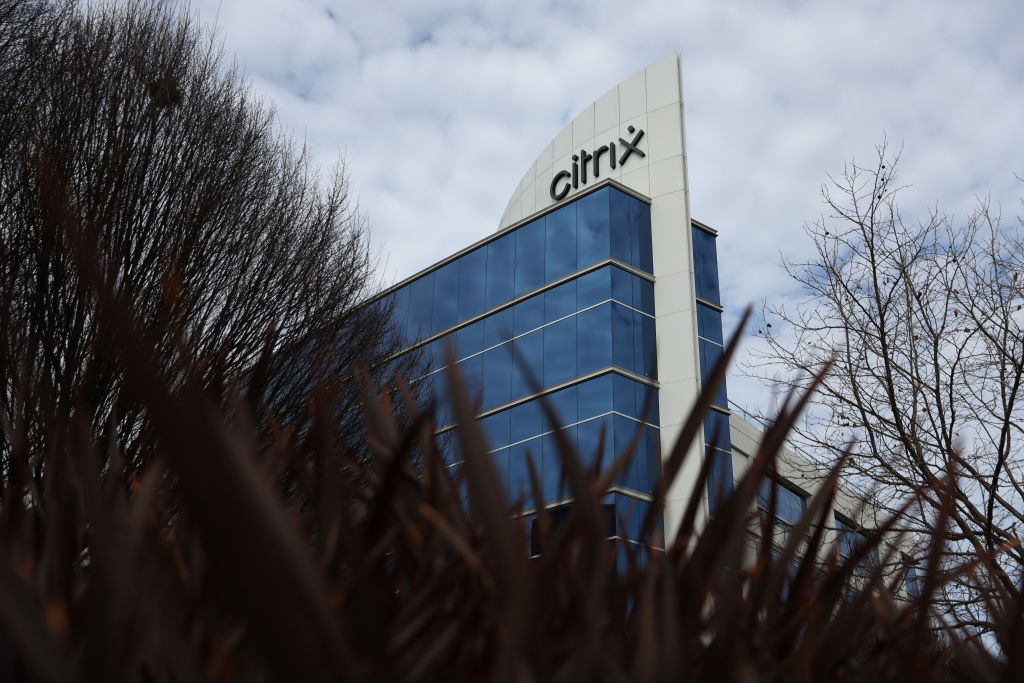
 Cyberscoop
Citrix NetScaler Zero-Days Exploited: Urgent Patches Released
Article Content

- •Citrix confirmed active exploitation of two critical zero-days in NetScaler products.
- •Patches were released on September 27, 2026, after a significant communication delay.
- •Over 50,000 Citrix NetScaler instances are potentially vulnerable to these exploits.
Citrix confirmed active exploitation of two critical zero-day vulnerabilities in its NetScaler products, CVE-2026-88771 and CVE-2026-88772, on September 27, 2026. These vulnerabilities, rated 9.5 on the CVSS scale, allow remote code execution and affect all NetScaler appliances in default configurations. The earliest known exploitation attempt occurred on September 24, 2026, when GreyNoise detected a malicious cyber actor attempting to exploit a Citrix NetScaler Gateway. Citrix's delayed communication left customers relying on unofficial channels for threat information. As of September 29, 2026, over 50,000 instances of Citrix NetScaler devices were identified as potentially vulnerable. Citrix has released patches and provided indicators of compromise to assist customers. Attribution for the attacks remains under investigation, with concerns about financially motivated cybercriminals and state-sponsored groups targeting these vulnerabilities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Ryuk, Citrix and CVE-2026-88771 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 PAYLOAD Ransomware Exploits Active Directory GPO for Disruption In April 2026, Kaspersky's Global Emergency Response Team (GERT) responded to a ransomware incident at a manufacturing organization in the Middle East. Attackers gained domain-admin-equivalent control via a compromised FortiGate SSL VPN account and created a malicious Group Policy Object (GPO) named PAYLOAD. This GPO…
 Education Sector Faces Surge in Cyberattacks Amid Open Network Vulnerabilities SonicWall's 2026 Education Protect Brief reveals that educational institutions are experiencing the highest per-device cyberattack intensity of any tracked sector, with 81,879 intrusion prevention system (IPS) hits per device in the first half of 2026. The report highlights that SIPVicious VoIP exploitation accounted…