 Adsadvance
Cyberattacks Disrupt Supermarket Refrigeration Across Europe
Article Content

- •Cyberattacks on supermarket refrigeration systems affected at least 10 European countries.
- •Temperatures in freezers reportedly reached 50°C, leading to significant food spoilage.
- •The NCSC is advising retailers to update their refrigeration control software.
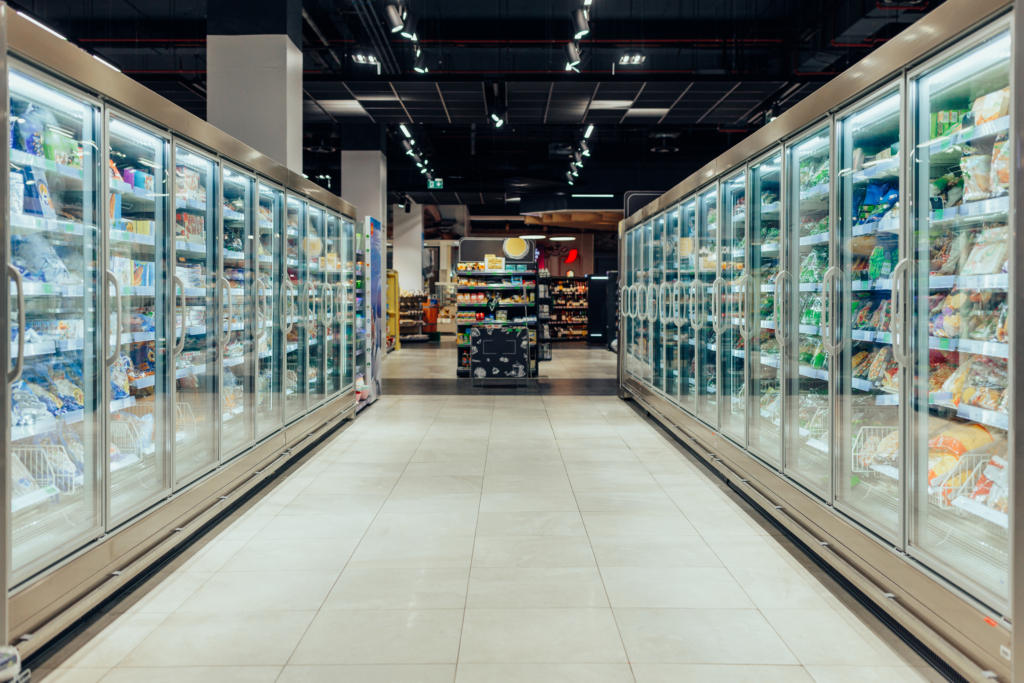
On November 4, 2026, cyberattacks targeted supermarket refrigeration systems in at least 10 European countries, causing significant food spoilage. Affected countries include Belgium, Ireland, Italy, and Sweden, with reports of freezer temperatures rising to 50°C. The attacks have forced retailers to discard thousands of tonnes of food. The UK's National Cyber Security Centre (NCSC) is investigating the incidents, which follow a similar attack on French supermarkets three weeks prior. No group has claimed responsibility, and there is currently no confirmed evidence of AI involvement. The NCSC is advising businesses to update their refrigeration control software to mitigate vulnerabilities. The EU has raised concerns about the potential for further disruptions in the food supply chain due to these incidents.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Intermarche in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Which countries were affected?
What is the current status of the investigation?
What actions should retailers take?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…