 Securityweek
Cybercriminals Exploit ChatGPT Custom GPTs for ClickFix RAT Attacks
Article Content

- •Attackers are using ChatGPT Custom GPTs to distribute malware via ClickFix techniques.
- •At least 40 users have been confirmed infected, with two incidents linked to Custom GPTs.
- •OpenAI has removed the malicious Custom GPTs, but new instances continue to appear.
A new ClickFix campaign has been discovered that exploits ChatGPT Custom GPTs to impersonate legitimate products, luring users into executing malicious code. Cybersecurity firm Huntress reported that at least 40 users have been infected, with two confirmed incidents linked to Custom GPT instances. The attackers created Custom GPTs that directed victims to a Google Sites link, leading to a malicious page that instructed users to run PowerShell commands to download a malicious MSI file. This file then deployed a remote access trojan (RAT) by sideloading malicious DLLs using legitimate Canon and Stardock executables. OpenAI took down the first Custom GPT on September 25, but a second one was discovered shortly after. The campaign highlights the ongoing abuse of AI platforms for social engineering attacks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track ClickFix, Cloudflare and CVE-2025-25249 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Russia's AI-Driven Cyber Espionage Targets Ukraine and Europe A Russian-linked hacking group, identified as GTG-20006, has utilized Anthropic's Claude AI to automate cyber espionage against over 20 organizations, primarily in Ukraine and Europe. The group targeted Ukrainian government officials, military personnel, and drone manufacturers through sophisticated phishing and…
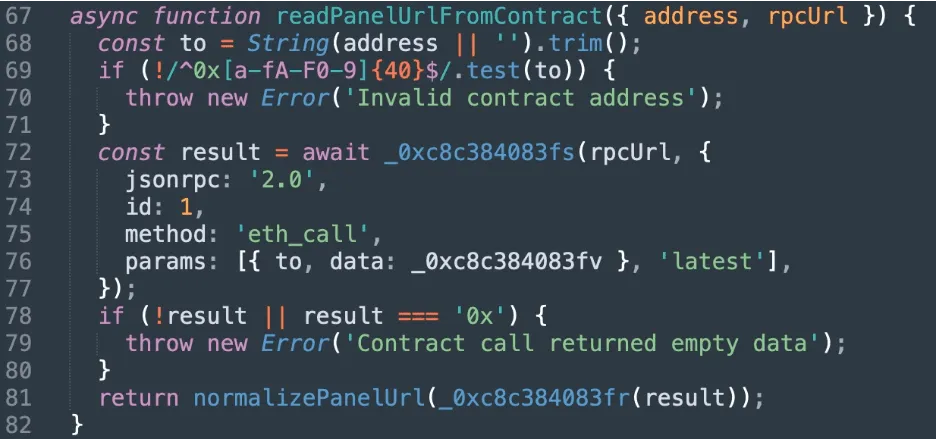 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…