 Datacenterdynamics
EQT Acquires Speedcast's Satellite Ground Infrastructure
Article Content

- •EQT Infrastructure VI acquired Speedcast's teleport business, enhancing SatPort's global reach.
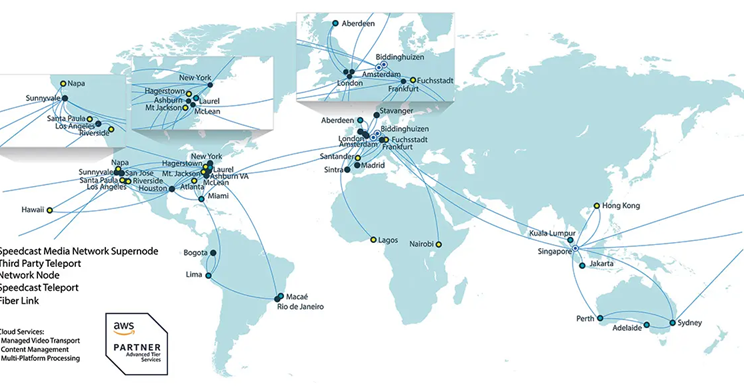
- •The acquisition includes 12 teleports across 11 countries, supporting satellite operators and governments.
- •Speedcast will remain a customer under a new long-term services agreement.
EQT Infrastructure VI has completed the acquisition of Speedcast's teleport infrastructure business, which includes 12 teleports across 11 countries and five continents. This acquisition positions SatPort Infrastructure as a global, carrier-neutral platform for satellite operators and governments. Speedcast will continue to utilize these services under a long-term agreement. The deal follows a prior agreement with Telesat to expand the Telesat Lightspeed ground network. The satellite industry is experiencing significant growth, with revenues projected to reach USD 145 billion by 2035, driven by the deployment of low Earth orbit (LEO) satellites. SatPort aims to provide secure and resilient ground infrastructure for various satellite constellations, enhancing its global capabilities. The acquisition is seen as a strategic move to meet the increasing demand for satellite services.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What does this acquisition mean for Speedcast?
How many teleports are included in the acquisition?
What is SatPort's role in the satellite industry?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…