 www.sekoia.com
Exvicy Malware Framework Leverages ErrTraffic Codebase
Article Content

- •Exvicy is a new ClickFix malware framework based on ErrTraffic's code.
- •The framework is actively used by threat actors for malware delivery via compromised WordPress sites.
- •Subscription prices for Exvicy increased due to heightened detection efforts.
Sekoia's TDR team identified Exvicy, a new ClickFix malware distribution framework, which is a copycat of ErrTraffic. Advertised on the Russian-speaking forum Exploit.IN since May 26, 2026, Exvicy is sold as Malware-as-a-Service (MaaS) and has seen active adoption by threat actors. The framework injects obfuscated JavaScript into compromised WordPress sites, utilizing social engineering tactics to trick victims into executing malicious PowerShell commands. The price for Exvicy's subscription increased from $1,200 to $2,000 due to rising detection rates. Technical analysis confirms that Exvicy reuses ErrTraffic's code, including its JavaScript and Command and Control (C2) communication logic. Sekoia's telemetry indicates multiple customer environments are communicating with Exvicy's C2 servers, confirming its operational use in malware delivery.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track ClickFix and Polygon in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Russia's AI-Driven Cyber Espionage Targets Ukraine and Europe A Russian-linked hacking group, identified as GTG-20006, has utilized Anthropic's Claude AI to automate cyber espionage against over 20 organizations, primarily in Ukraine and Europe. The group targeted Ukrainian government officials, military personnel, and drone manufacturers through sophisticated phishing and…
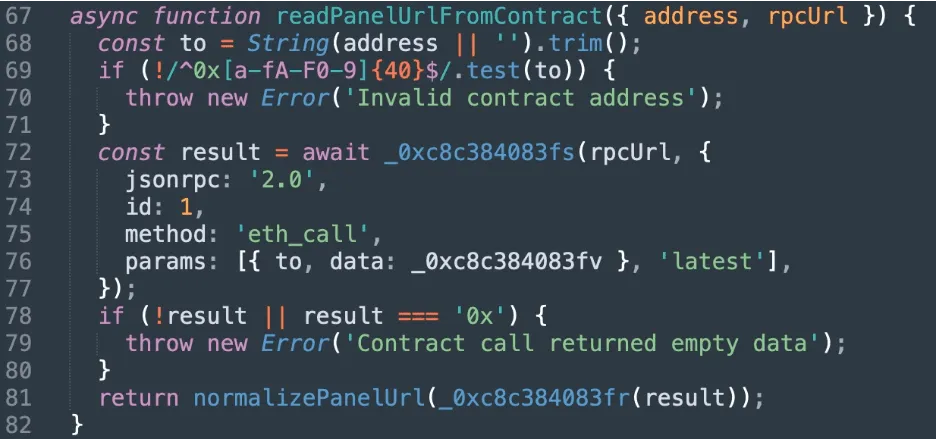 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…