 Justice
FBI Seizes NightmareStresser DDoS-for-Hire Domains in Major Crackdown
Article Content

- •FBI seized NightmareStresser domains linked to hundreds of thousands of DDoS attacks.
- •The service had over 566,000 registered users and allowed attacks of up to 200 Gbps.
- •This operation is part of the ongoing Operation PowerOFF targeting DDoS-for-hire infrastructure.
On September 15, 2026, the FBI seized the domains of NightmareStresser, a notorious DDoS-for-hire service linked to hundreds of thousands of attacks since 2022. This operation, part of the ongoing Operation PowerOFF, targeted infrastructure enabling users to launch distributed denial-of-service attacks against various victims, including educational institutions and government agencies. NightmareStresser had over 566,000 registered users and offered services that allowed for attacks of up to 200 Gbps. The service was known for its ease of use, allowing even non-technical users to rent DDoS capabilities. The seizure is part of a broader effort that has seen over 100 domains seized and 12 individuals charged in the last eight years. The FBI's actions aim to disrupt the growing trend of accessible cybercrime through booter services.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (41)
Following this threat?
Track NightmareStresser and CVE-2026-90894 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
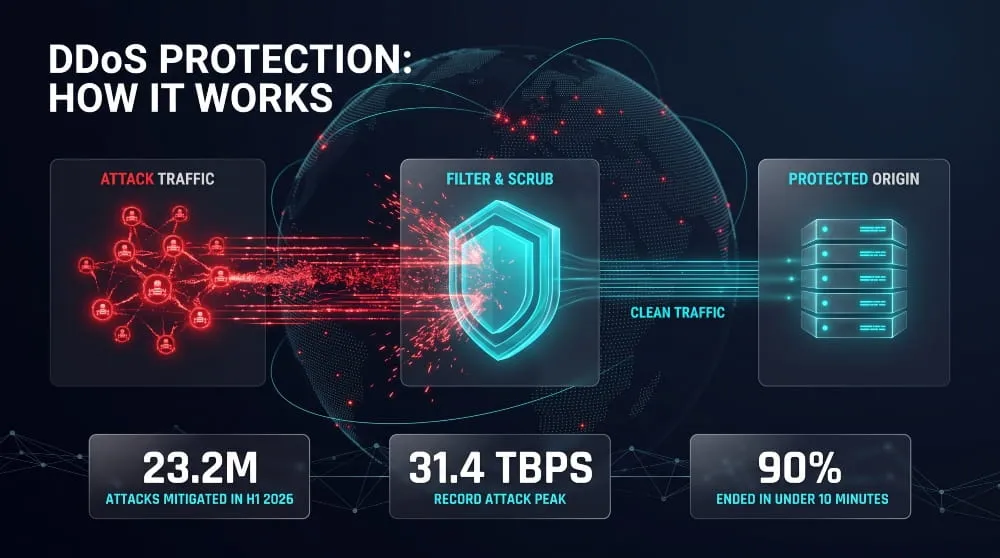 Surge in DDoS Attacks Driven by IoT Botnets in 2026 In 2026, DDoS attacks have surged, with Cloudflare reporting 23.2 million mitigated network-layer attacks in the first half of the year. These attacks are increasingly leveraging compromised IoT devices, particularly through Turbo Mirai-class botnets, which can generate terabits per second. The Adaptive DDoS…
 North Korean Hackers Steal $6.3 Billion from Binance in Record Crypto Heist On October 29, 2026, Binance, the world's largest cryptocurrency exchange, reported a massive security breach resulting in the theft of approximately $6.3 billion across ten blockchains. The attack is attributed to North Korea's TraderTraitor hacking group, which gained access via a compromised DevOps engineer's…