 Helpnetsecurity
Fireperf: New Open-Source Tool for Testing Firewall Connection Handling
Article Content

- •Fireperf measures firewall connection handling, not just data throughput.
- •The tool supports multiple clients on a single server port simultaneously.
- •It is available for various Linux distributions and is open-source.
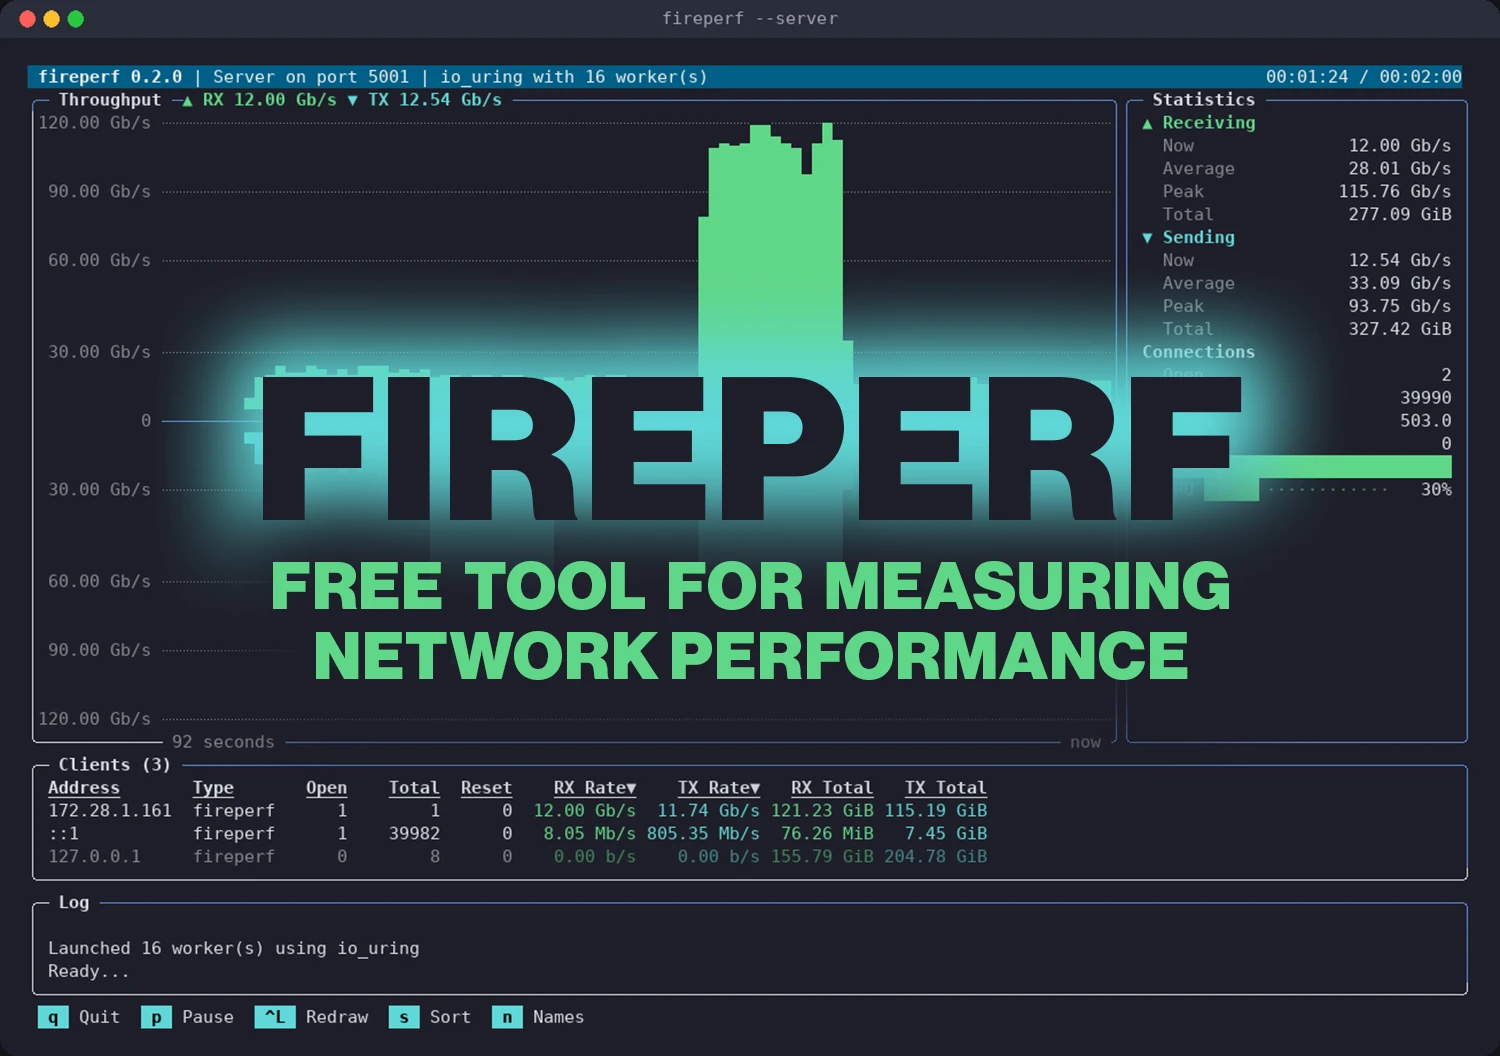
The IPFire project has launched fireperf, an open-source tool designed to measure how firewalls and routers handle connections, rather than just data throughput. It can simulate multiple clients on a single server port and track connection setup failures, providing insights into firewall performance under load. Fireperf is particularly useful for administrators and developers who need to evaluate the connection handling capabilities of stateful systems. The tool is compatible with several Linux distributions, including Debian and Arch Linux, and is available for free. Rico Hoppe, the creator, emphasized its unique event-loop design, which differs from traditional bandwidth testers like iperf3. The tool logs connection handshakes and failures, offering a more comprehensive view of firewall performance. It is intended for use in environments where high connection rates are, such as intrusion prevention systems (IPS). The source code and installation packages are readily accessible for users.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Debian in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is fireperf?
Which Linux distributions support fireperf?
What are the key features of fireperf?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…