 www.infostealers.com
FortiBleed 2.0 Exposes Over 101,000 Credentials and 975 New Domains
Article Content

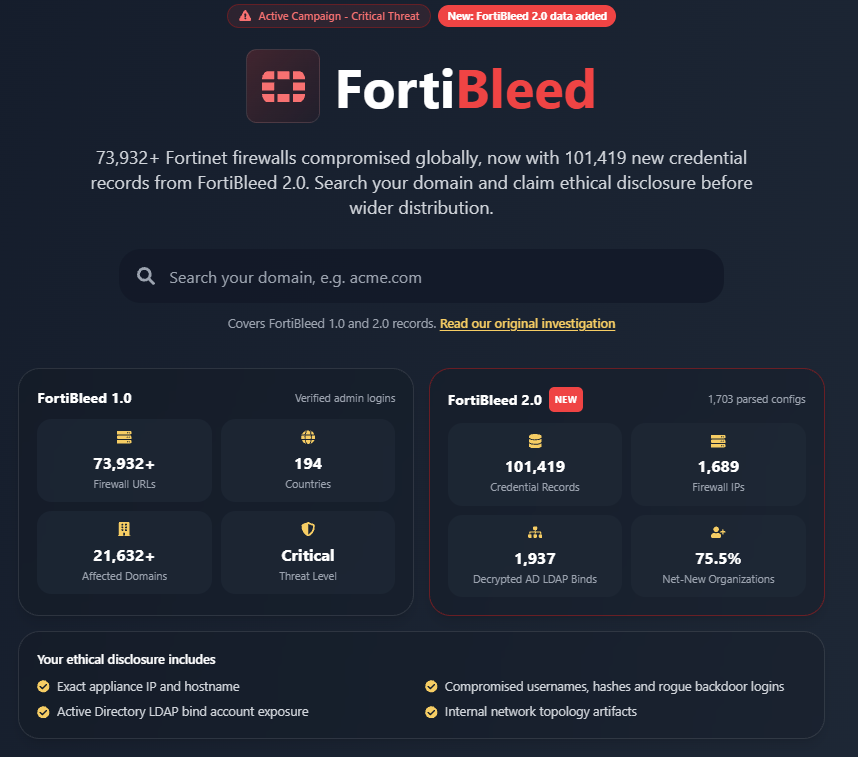
- •FortiBleed 2.0 reveals over 101,000 credential records, including 40,573 cleartext secrets.
- •975 new domain labels were identified, expanding the scope of the initial FortiBleed incident.
- •Organizations are urged to reassess their exposure using the updated dataset from FortiBleed 2.0.
The FortiBleed 2.0 investigation has revealed a significant credential exposure incident involving Fortinet's FortiGate firewalls. Researchers uncovered 101,419 credential and account records, including 40,573 cleartext secrets, from 1,703 configuration reports dated around February 2026. The analysis identified 975 new domain labels not present in the original FortiBleed dataset. This follow-up investigation does not indicate a new wave of attacks, as the report dates predate the earlier findings. Organizations previously checked against the June 2026 alert are advised to reassess using the updated dataset. The exposure includes configuration data, such as local user secrets and Active Directory LDAP bind records. The incident primarily affects organizations using Fortinet's products, with no specific CVEs reported. The findings were published by HKCERT and corroborated by InfoStealers.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Fortinet in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What types of records were exposed?
How many new domains were identified?
What should organizations do now?
Continue Reading
 CyberXero Campaign Targets Ukrainian Records Using AI Tools CyberXero, a Russian-speaking initial access broker, has launched a dual-pronged campaign targeting WordPress sites and Ukrainian critical infrastructure, leveraging AI tools like Claude Code. The operation has led to the exfiltration of over 628,000 records from Ukrainian entities, with confirmed compromises in…
 Krybit and Qilin Target Organizations with FortiBleed Exploits Cybercriminal groups Krybit and Qilin have recently published details of their attacks on organizations using FortiOS SSL-VPN, exploiting the FortiBleed vulnerability (CVE-2022-40684). Krybit's latest victim is www.zhservices.com, while Qilin has targeted Revi Group. Both incidents involve the exposure of FortiOS…