 www.interpol.int
Global Fraud Summit 2026 Highlights Urgent Need for Cooperation Against Fraud
Article Content

- •Global losses from fraud are estimated at USD 442 billion.
- •The summit focused on the role of technology in facilitating fraud, including deepfakes.
- •Over 1,300 participants from various sectors attended the summit to discuss cooperation.
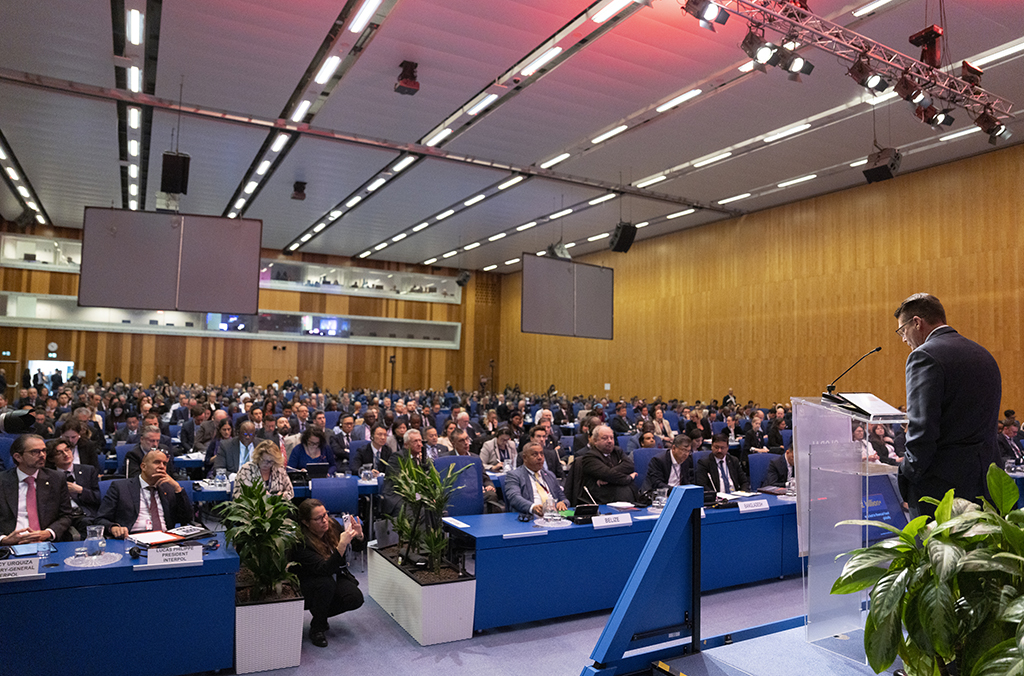
The Global Fraud Summit, held on March 16-17, 2026, in Vienna, concluded with calls for enhanced international cooperation to combat the rising tide of fraud, which has become increasingly sophisticated due to technological advancements. INTERPOL reported that global losses from organized fraud and scams are estimated at USD 442 billion, impacting millions of individuals and businesses. The summit emphasized the role of technology, including generative AI and deepfake tools, in facilitating fraud. Discussions highlighted the need for coordinated intelligence sharing and operational collaboration among law enforcement and international organizations. The event was attended by over 1,300 participants from various sectors, including government, law enforcement, and technology companies, who engaged in assessing emerging fraud trends. INTERPOL's Executive Director noted the urgency of addressing this global security crisis, as fraud continues to evolve and expand its reach.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track European Commission in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What are the main fraud types discussed?
How many participants attended the summit?
What is the estimated global loss from fraud?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…