 Chinadailyasia
Iran's Hormuz Strait Reopening Proposal Remains Amid Stalled US Talks
Article Content

- •Iran's seven-day plan to reopen the Strait of Hormuz is still on the table.
- •Negotiations with the US have stalled due to unmet conditions from Iran.
- •Iran warns of severe military responses to any miscalculations by the US or Israel.
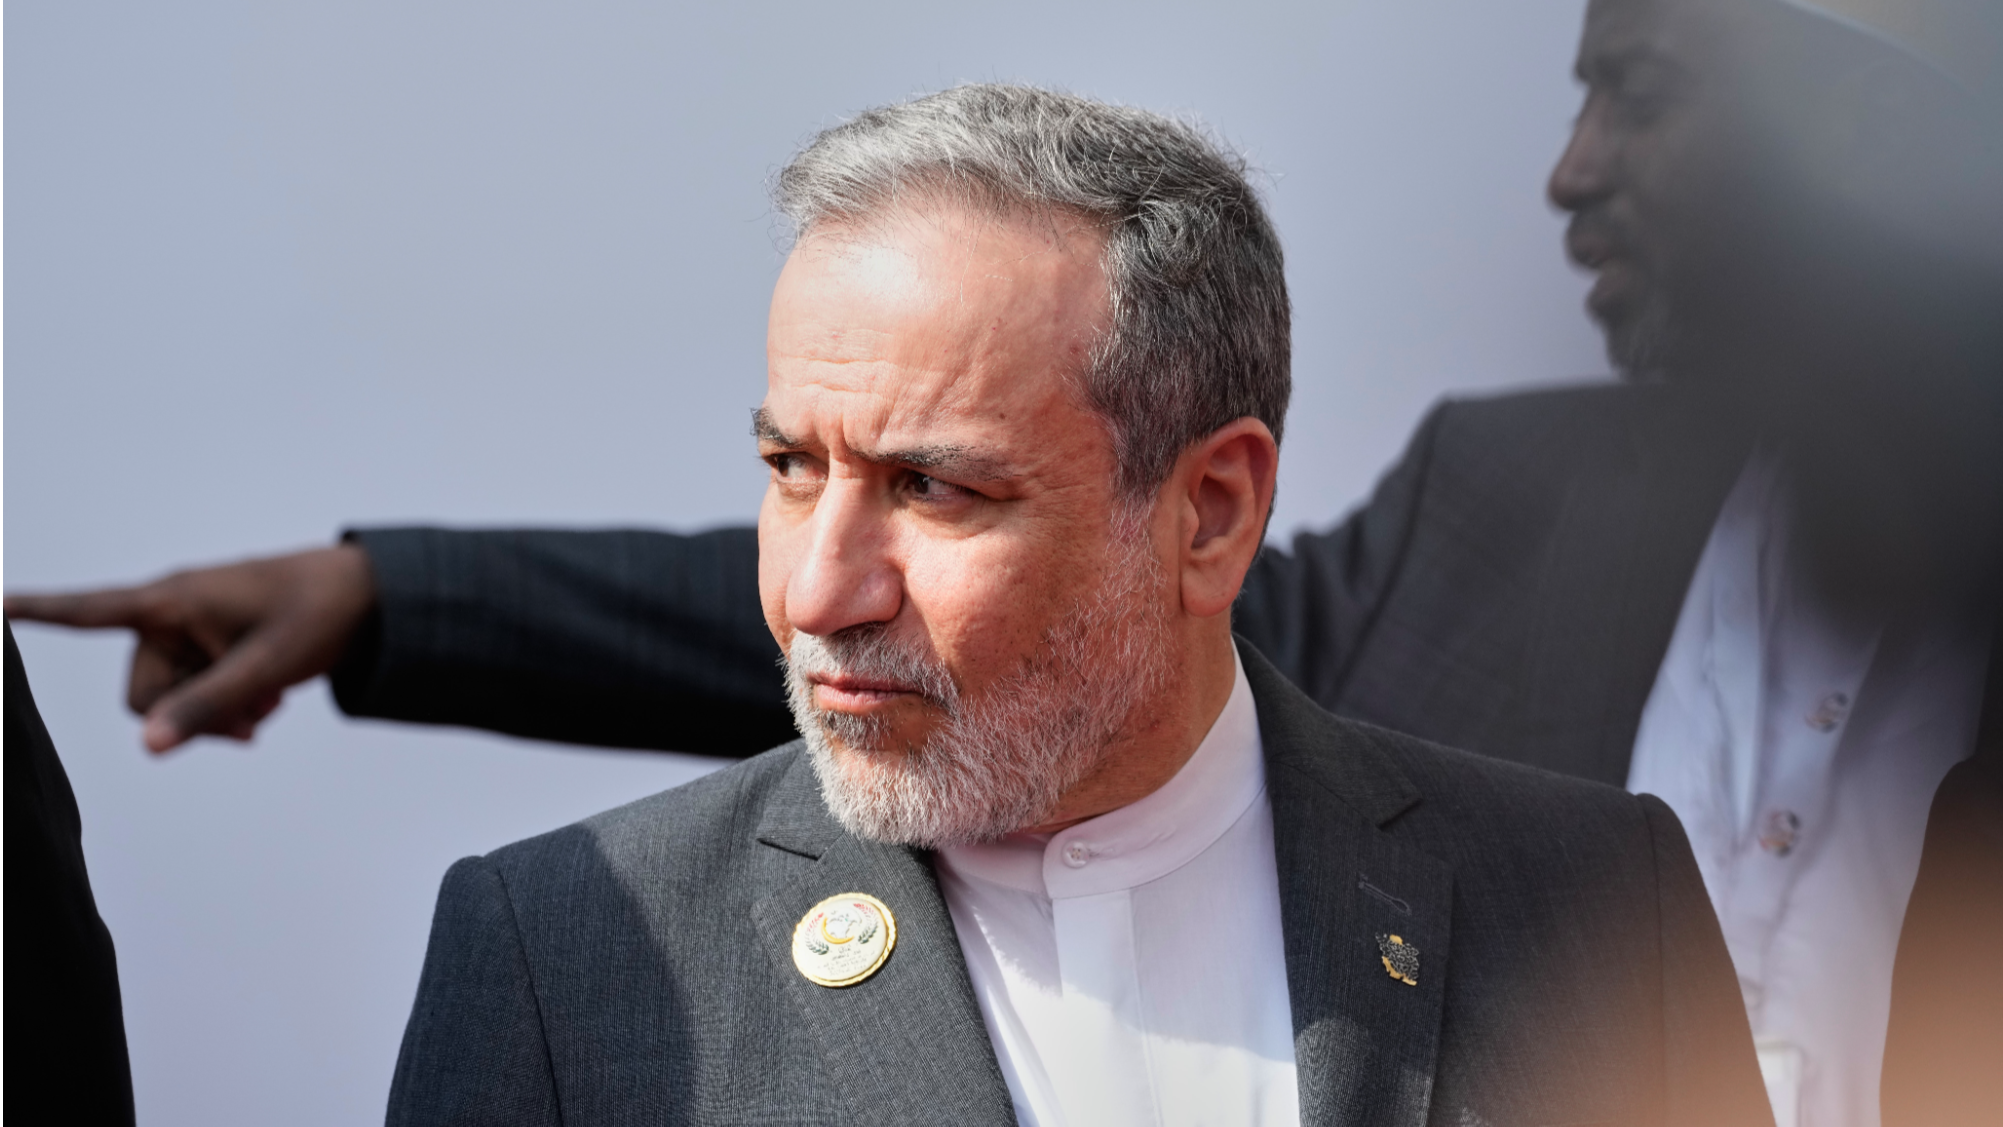
Iran's Foreign Minister Abbas Araghchi confirmed that the proposal to reopen the Strait of Hormuz within seven days is still valid. This proposal, presented in mid-September after a ceasefire collapsed, includes conditions such as lifting the US blockade and sanctions on Iranian oil exports. The US has responded, but negotiations have stalled due to disagreements over Iran's conditions. Araghchi emphasized that if the US meets Iran's demands, the strait could reopen within six days, with negotiations resuming the next day. The Strait of Hormuz is crucial for global oil trade, previously handling a fifth of the world's oil and LNG. Iran has warned that any miscalculations by the US or Israel could lead to a severe military response. The situation remains tense as both sides continue to evaluate their positions.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What conditions does Iran require for reopening the strait?
What is the significance of the Strait of Hormuz?
What could happen if negotiations fail?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…