 Escudodigital
ISACA Conference Highlights AI Governance and Cybersecurity Challenges
Article Content

- •ISACA Conference 2026 addressed AI governance and cybersecurity effectiveness.
- •Monica Verma warned organizations are unprepared for AI-related challenges.
- •Sessions highlighted the importance of a people-centric defense against AI-driven attacks.
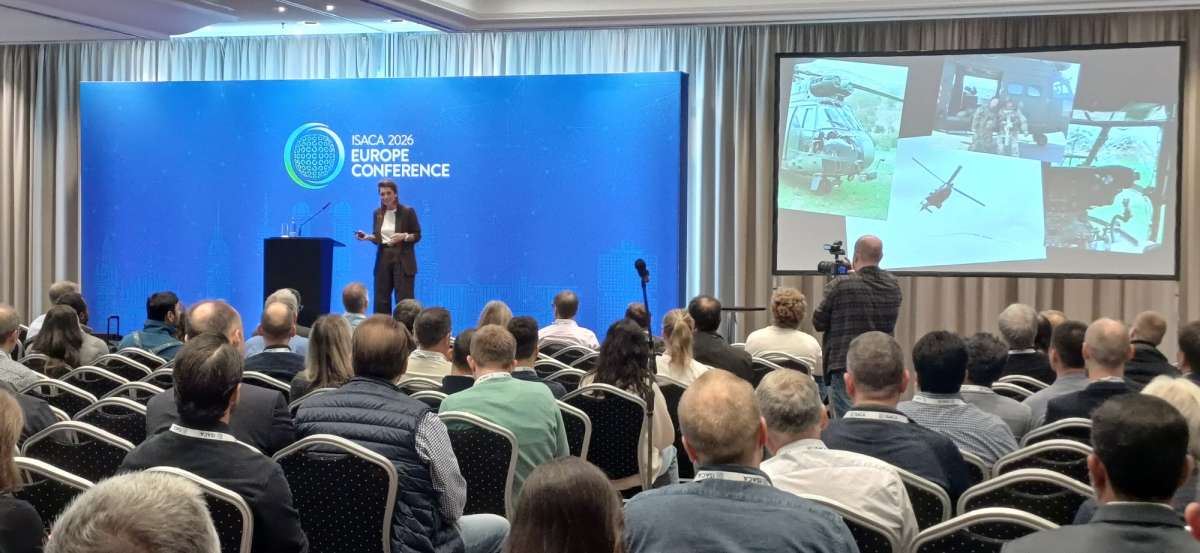
The ISACA European Conference 2026, held from October 7-9 in Munich, focused on the rapid evolution of AI and its implications for cybersecurity. Key discussions included the need for organizations to enhance AI governance and assess cybersecurity effectiveness. Monica Verma emphasized the unpreparedness of most organizations for AI challenges, advocating for a governance framework that includes data management, leadership, and culture. Ramona Ratiu and Zeynep Turesin Soylu highlighted the human factor in defending against AI-driven attacks, showcasing examples of fraud using deepfakes. The conference featured over 50 speakers and discussions on quantum risks and European regulations related to cybersecurity. The event underscored the urgency for organizations to adapt their security measures in response to AI advancements.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What are the key topics discussed at the conference?
Who were the notable speakers?
What is the significance of AI governance?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…