 Kyivindependent
Kromberg & Schubert Plant in Lutsk Halts Operations After Russian Drone Attack
Article Content

- •The Kromberg & Schubert plant in Lutsk was attacked by Russian drones on October 16.
- •The facility manufactures wiring systems for major automotive brands like BMW and Audi.
- •Ukrainian air defenses reportedly intercepted many of the attacking drones.
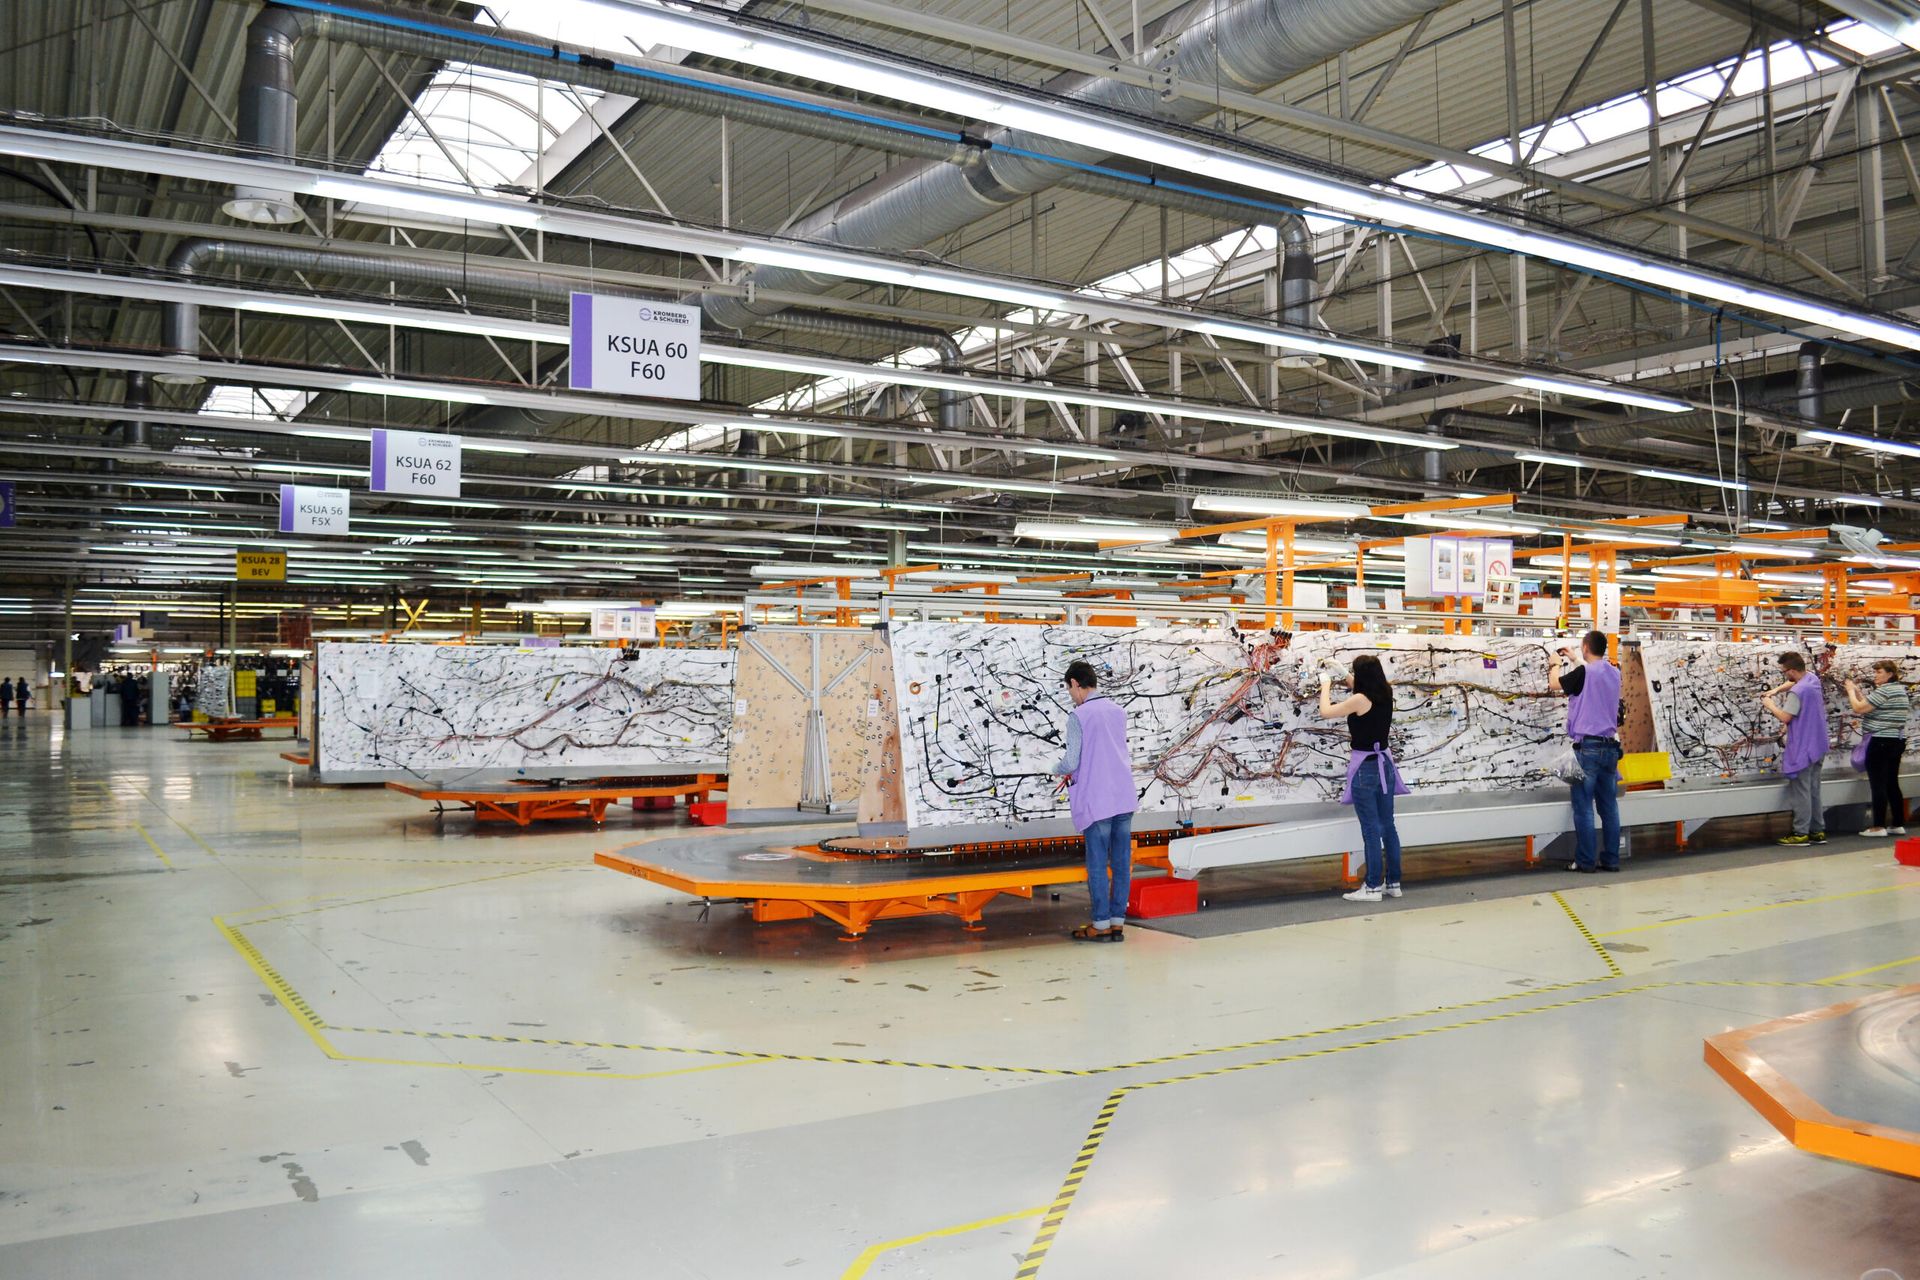
On October 16, 2026, the Kromberg & Schubert electrical wiring plant in Lutsk, Ukraine, suspended operations following a Russian drone attack. The facility, which manufactures wiring systems for major automotive brands, was targeted by jet-powered drones from the Geran family. The attack was confirmed by local military officials, who noted that the plant is a foreign investment site. Employees have been instructed to stay in touch with management for updates on the situation. The attack is part of a broader pattern of strikes on critical infrastructure in Volyn Oblast. Eyewitness accounts and military reports indicate that Ukrainian air defenses successfully intercepted a significant number of incoming drones. The situation remains fluid as the company assesses damage and coordinates safety measures for its workforce.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Kromberg And Schubert in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is the current status of the plant?
How many drones were intercepted?
What brands are affected by the plant's closure?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…