 United24Media
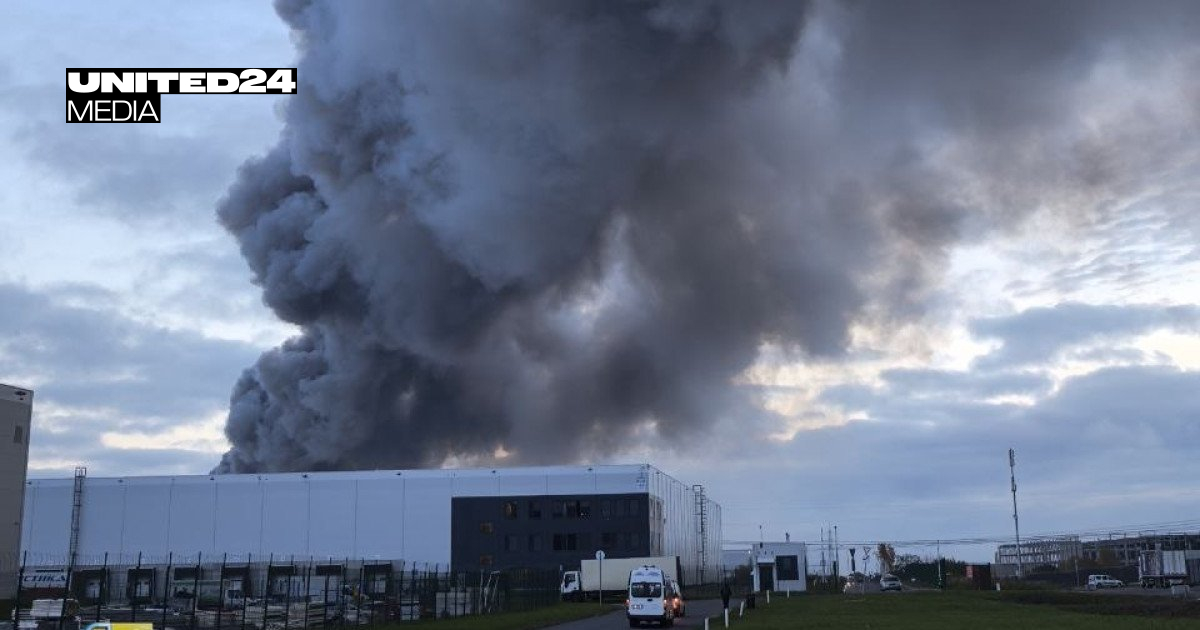
Mass Drone Attack Targets Ozon Warehouse in St. Petersburg
Article Content

- •A massive drone attack on October 18 targeted an Ozon warehouse in St. Petersburg.
- •The attack caused significant disruptions, including flight cancellations and power outages for over 20,000 residents.
- •Local authorities reported the downing of 144 drones during the incident.
On October 18, 2026, a massive drone attack struck St. Petersburg, impacting an Ozon warehouse and causing widespread disruptions. The warehouse, located in the Kolpinsky District and covering 79,000 square meters, caught fire, although the extent of damage remains unclear. The attack also led to the cancellation of 15 flights and the delay of 25 others at Pulkovo Airport. Over 20,000 residents in the Leningrad region lost power due to the disconnection of two transformer substations. Local authorities reported that 144 UAVs were shot down during the incident, while the Russian Defense Ministry claimed to have destroyed 1,015 UAVs over Russian territory. This incident is part of a broader wave of drone strikes targeting logistics and energy infrastructure across the region.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Ozon in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What areas were affected by the power outages?
How many drones were involved in the attack?
What is the current status of the Ozon warehouse?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…