 Theguardian
Melania Trump Brokers Ceasefire Amid Ongoing Ukraine Conflict
Article Content

- •Melania Trump hosted a ceasefire celebration for Russian and Ukrainian officials.
- •The ceasefire allowed for the evacuation of hundreds from the besieged town of Oleshky.
- •Ongoing violence in Ukraine continues despite the temporary truce.
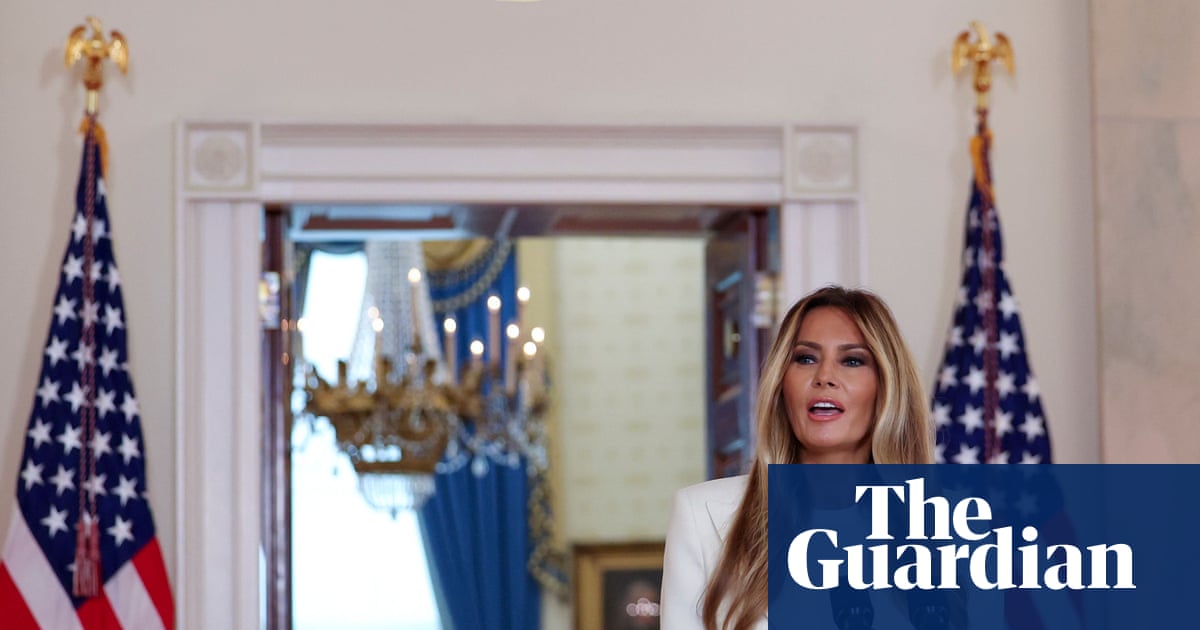
On November 5, 2026, First Lady Melania Trump hosted Russian and Ukrainian officials at the White House to celebrate a ceasefire in Oleshky, a town in Ukraine facing severe humanitarian issues. The ceasefire allowed the evacuation of hundreds of residents amidst ongoing conflict, with both sides crediting Trump for her role in brokering the agreement. During the event, officials from both nations expressed gratitude towards Trump, who discussed humanitarian efforts and demining plans. Despite the positive developments in Oleshky, the broader conflict continues, with recent attacks in Kyiv and other cities. The meeting marks a significant diplomatic moment, as it was one of the highest-level gatherings of Russian and Ukrainian officials in months. However, the ongoing violence and political tensions remain a concern, with the situation in Ukraine still critical.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What was the purpose of the White House meeting?
How many people were evacuated during the ceasefire?
What is the current status of the conflict in Ukraine?
Continue Reading
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…