 Dexpose
Multiple Ransomware Attacks Target Various Organizations
Article Content

- •Multiple organizations have been targeted by ransomware attacks in September 2026.
- •Victims include watchops.com and geekybunch.com, with reported revenues of $1.3 million and $5 million.
- •Details about the attacks remain vague, with no confirmed data breaches or ransom demands disclosed.
In September 2026, multiple organizations, including watchops.com and geekybunch.com, were reported as victims of ransomware attacks by the group known as 'unsafe'. The incidents were listed on dark web leak sites, but details regarding the nature of the attacks, such as data encryption or theft, remain vague. The affected companies reported revenues of approximately $1.3 million and $5 million, respectively. Additionally, other victims like Downrite Engineering, Hattiesburg Eye Clinic, and Technical Asia were also named in the reports. The attack methods and specific vulnerabilities exploited were not disclosed, leaving the scope and impact of these incidents largely unknown. The reports emphasize the need for caution, as many claims remain unverified. Overall, the current status indicates ongoing threats without confirmed data breaches.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (195)
Following this threat?
Track AuditTeam, Arab Maritime Petroleum Transport Company and CVE-2022-40684 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CyberXero Campaign Targets Ukrainian Records Using AI Tools CyberXero, a Russian-speaking initial access broker, has launched a dual-pronged campaign targeting WordPress sites and Ukrainian critical infrastructure, leveraging AI tools like Claude Code. The operation has led to the exfiltration of over 628,000 records from Ukrainian entities, with confirmed compromises in…
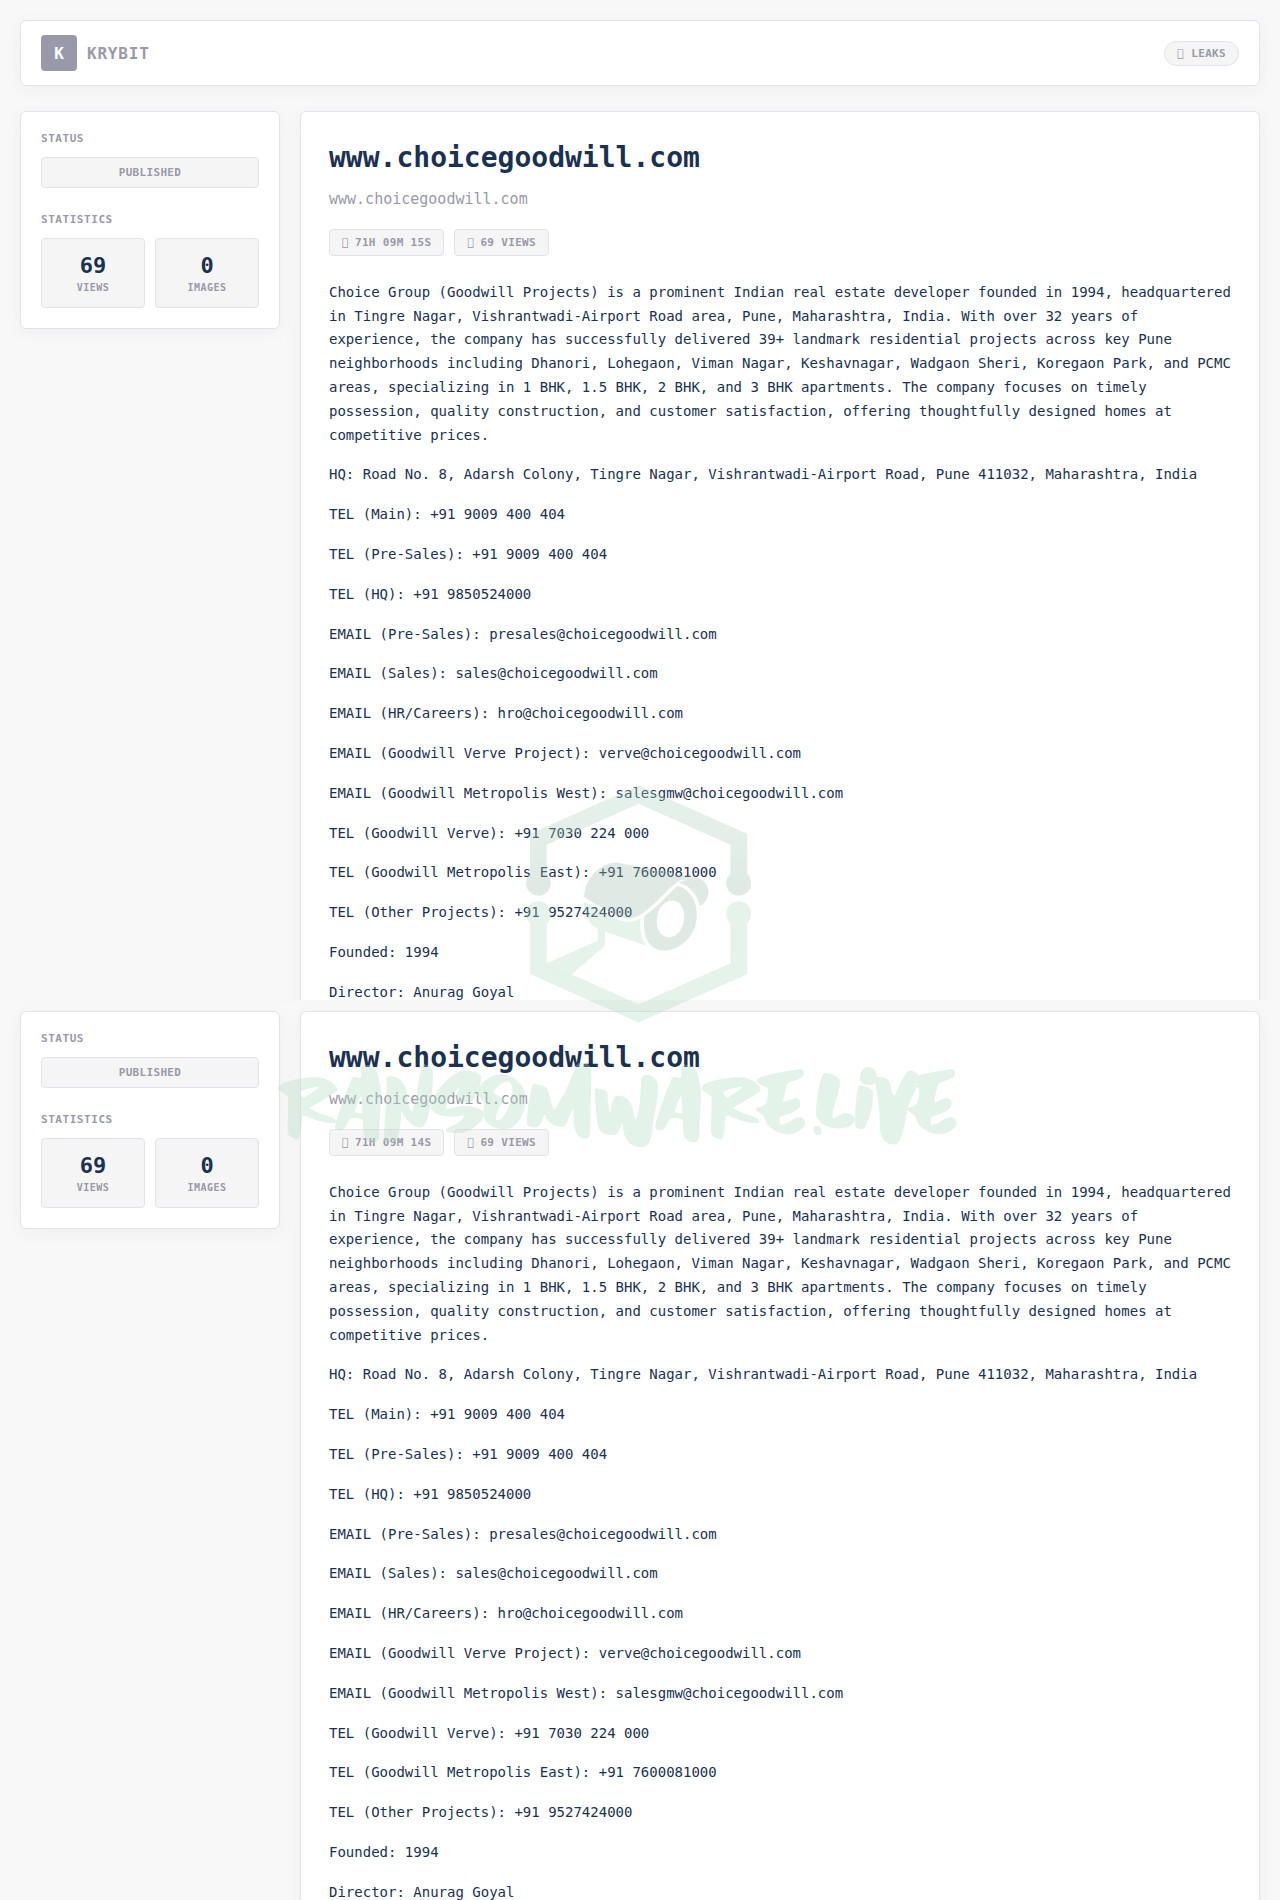 Krybit and Qilin Target Organizations with FortiBleed Exploits Cybercriminal groups Krybit and Qilin have recently published details of their attacks on organizations using FortiOS SSL-VPN, exploiting the FortiBleed vulnerability (CVE-2022-40684). Krybit's latest victim is www.zhservices.com, while Qilin has targeted Revi Group. Both incidents involve the exposure of FortiOS…