 Defensedaily
NRO Launches New Cyber Protection Office with $250M Budget
Article Content

- •NRO's new Cyber Protection Office has a budget of $250 million and over 600 staff.
- •The CPO aims to integrate cyber operations and security functions to counter threats effectively.
- •Warnings from ONCD highlight the increasing risk of AI-driven cyber attacks.
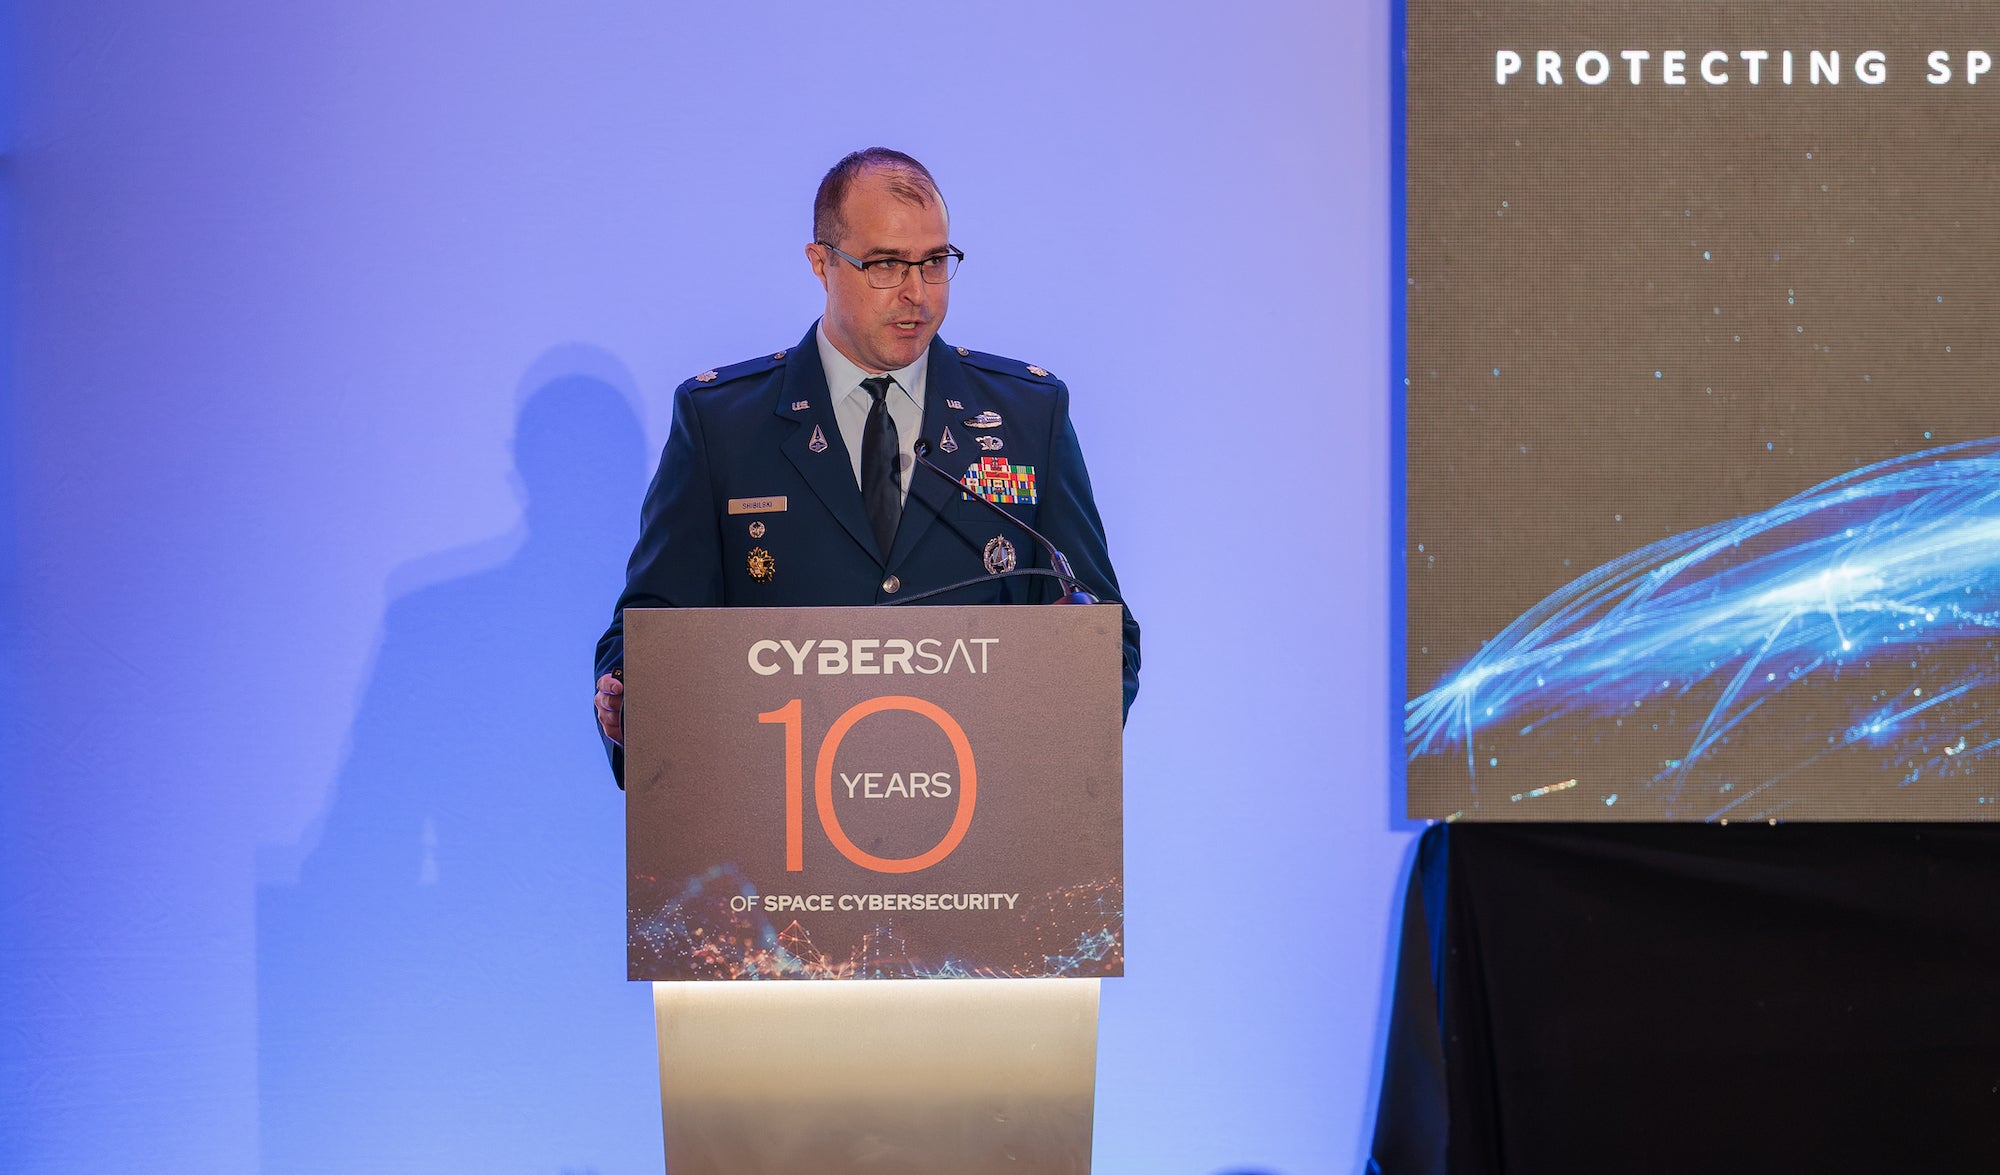
The National Reconnaissance Office (NRO) has established a new Cyber Protection Office (CPO) with a budget of $250 million and a staff exceeding 600 personnel. Lt. Col. Luke Shibilski announced the office's formation at CyberSat, emphasizing the need for integrated cyber operations and security functions. The CPO aims to address threats that exploit organizational gaps and provide continuous cyber defense, incident response, and risk management services. This initiative is part of a broader effort to enhance cyber visibility and support combatant commands globally. The office will also monitor Department of Defense networks, including legacy systems. The urgency of these developments is underscored by warnings from the Office of the National Cyber Director regarding the accelerating threat of AI in cyber attacks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What services does the Cyber Protection Office provide?
What is the significance of the CPO's formation?
What are the concerns regarding AI in cyber attacks?
Continue Reading
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…
 Chinese Actor Compromises US Government Networks via PHP2Shell Exploit A suspected Chinese nation-state actor exploited vulnerabilities in Palo Alto Networks firewalls using a chained PHP2Shell exploit and a Linux kernel privilege escalation flaw. The attack, which began on October 23, targeted 25 servers across the US, Japan, Taiwan, and South Korea, with a focus on US…