 Independent
Nurse Struck Off for Stealing £770k from Vulnerable 99-Year-Old
Article Content

- •Rebecca Burwood exploited a vulnerable 99-year-old, taking £770,000 from her.
- •The nurse manipulated the elderly woman into transferring her house and making large withdrawals.
- •Burwood was struck off by the Nursing and Midwifery Council for serious misconduct.
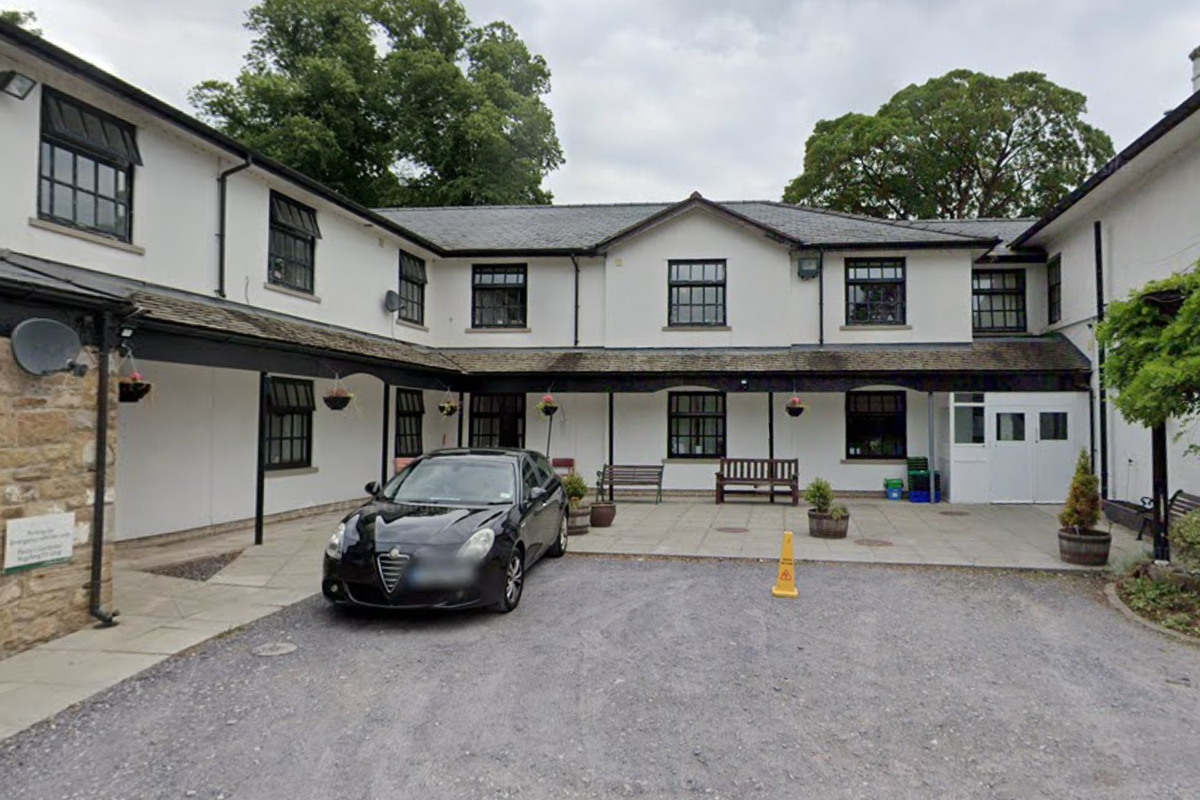
Rebecca Burwood, a nurse at Bryn Yr Haul Care in Mold, Wales, exploited a 99-year-old woman, taking £770,000 over six years. The elderly resident, who had no family, was manipulated into transferring ownership of her house and withdrawing large sums from her bank account. Burwood used the funds for personal expenses, including vehicles and cosmetic surgery. The Nursing and Midwifery Council found her actions constituted serious misconduct, leading to her removal from the nursing register. The victim's bank froze her account due to suspicious activity, prompting an investigation by North Wales Police, which ultimately took no further action as the woman did not wish to file a complaint. Burwood claimed the withdrawals were gifts, but evidence indicated emotional coercion.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Bryn Yr Haul Care in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What was the total amount stolen?
What actions were taken against Burwood?
Was the elderly woman able to file a complaint?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…