 Irishsun
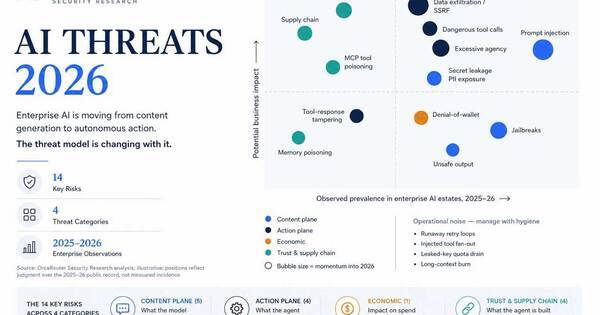
OrcaRouter AI Threat Report 2026 Highlights Rising Prompt Injection Risks
Article Content

- •Prompt injection attacks have surged 340% year-over-year, posing a critical risk to LLM applications.
- •13% of organizations have experienced breaches via AI models, with most lacking basic access controls.
- •OrcaRouter has released security controls for free to help mitigate these emerging threats.
OrcaRouter Security Research released its AI Threat Report 2026, identifying prompt injection as the leading risk to large language model (LLM) applications, with a 340% increase in such attacks year-over-year. The report reveals that 13% of organizations have been breached through AI models, primarily due to inadequate access controls. Notably, the EchoLeak attack (CVE-2025-32711) exemplified the dangers of zero-click exploits, where sensitive data was exfiltrated without user interaction. The report also details several significant incidents from 2026, including data leaks from Chat & Ask AI and Sears Services, and highlights vulnerabilities like CVE-2026-21520 and CVE-2026-39987. OrcaRouter has made its agent Firewall and input/output Guardrails available for free to enhance security against these threats. The report emphasizes that AI systems have become a significant attack surface, with telemetry indicating that successful attacks average completion in just 42 seconds.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Microsoft and CVE-2025-32711 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Emerging Threats from AI-Generated Content Exfiltration A new tool called `exfil-scan` has been developed to detect data exfiltration signals in outputs from large language models (LLMs) and AI-generated content. This tool addresses vulnerabilities highlighted by the EchoLeak attack family, particularly CVE-2025-32711, which demonstrated how hidden payloads could be…
 Emerging Threats from AI Prompt Injection Attacks Recent reports highlight two significant AI-related vulnerabilities: prompt injection and a new attack method called Reprompt. Prompt injection allows attackers to embed malicious instructions within documents or prompts, manipulating AI systems to act against user intent. The Reprompt attack, discovered in Microsoft…