Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
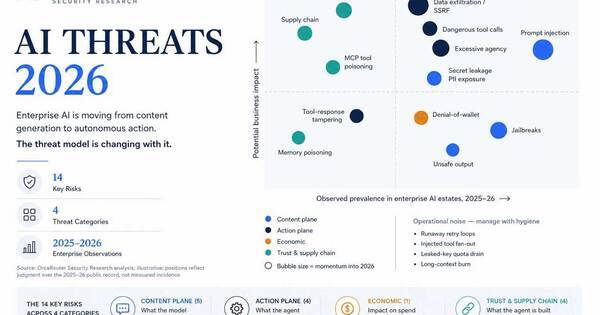
OrcaRouter Security Research released its AI Threat Report 2026, identifying prompt injection as the leading risk to large language model (LLM) applications, with a 340% increase in such attacks year-over-year. The report reveals that 13% of organizations have been breached through AI models, primar...
Microsoft and Salesforce have patched serious prompt injection vulnerabilities in their AI platforms, Copilot Studio and Agentforce, respectively. Capsule Security identified these flaws, allowing attackers to exfiltrate sensitive data via crafted inputs in SharePoint and CRM forms. The Microsoft vu...
A newly disclosed vulnerability in Microsoft 365 Copilot Enterprise, named SearchLeak (CVE-2026-42824), allows attackers to exfiltrate sensitive data with a single click on a crafted link. Discovered by Varonis Threat Labs, the attack exploits a chain of three vulnerabilities: parameter-to-prompt in...
Recent research highlights significant vulnerabilities in agentic AI systems, which can misclassify adversarial inputs as trusted instructions across six architectural layers. These vulnerabilities stem from trust boundary failures, allowing unauthorized actions through tools and memory. The Layered...