 Thelec
Palo Alto Networks Firewalls Exploited Amid AI Security Concerns
Article Content

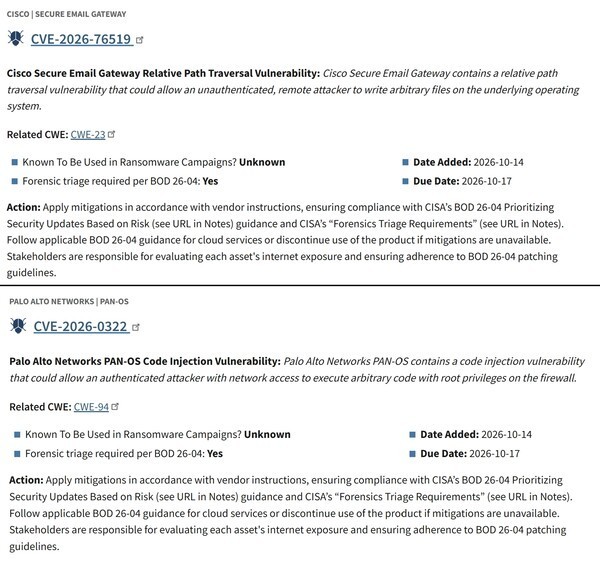
- •Palo Alto Networks and Cisco products have critical vulnerabilities actively exploited.
- •CVE-2026-0322 allows attackers root access to affected firewalls.
- •68% of security leaders lack real-time visibility into their OT networks.
Palo Alto Networks and Cisco products have been identified as vulnerable to active cyberattacks, with critical vulnerabilities added to CISA's Known Exploited Vulnerabilities catalog. The vulnerabilities, including CVE-2026-0322, could allow attackers to gain root privileges on affected systems. Palo Alto Networks confirmed limited exploitation targeting its PAN-OS management interface, which is crucial for firewall administration. The vulnerabilities were disclosed on October 14, 2026, and a patch was released the same day. Security leaders are increasingly worried about AI-driven cyber threats, as highlighted in a recent report by Palo Alto Networks. The report indicated that 68% of critical infrastructure security leaders lack real-time visibility into their operational technology networks, raising concerns about potential impacts from such vulnerabilities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Cisco and CVE-2026-0322 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Which products are affected?
What is the nature of the vulnerabilities?
What actions should organizations take?
Continue Reading
 CISA Adds Critical Vulnerabilities in PAN-OS, Cisco, and Ahsay to KEV Catalog The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added four vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in Palo Alto Networks PAN-OS, Cisco Secure Email Gateway, and AhsayCBS. The vulnerabilities are CVE-2026-0322 (high-severity code injection)…
 Palo Alto Networks PAN-OS RCE Vulnerability CVE-2026-0322 Palo Alto Networks disclosed a remote code execution (RCE) vulnerability, CVE-2026-0322, affecting the management interface of PAN-OS software. This flaw allows authenticated attackers with network access to execute arbitrary code with root privileges on affected firewalls. The vulnerability has a CVSS score of 8.6…