 Azfamily
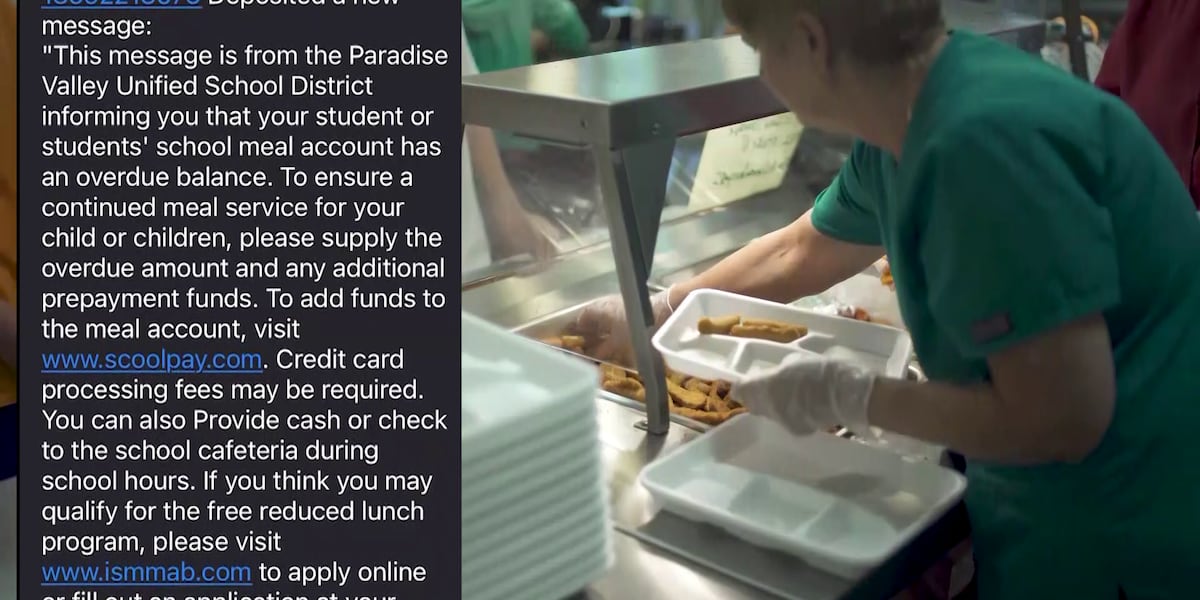
Paradise Valley School District Alerts Parents to Text Message Phishing Scam
Article Content

- •Paradise Valley Unified School District warns of a text message phishing scam targeting parents.
- •41% of educational institutions report being targeted by AI-generated phishing attempts.
- •Parents should verify unexpected communications and use strong passwords to enhance security.
The Paradise Valley Unified School District has issued a warning to parents about a phishing scam involving text messages claiming that their children's school meal accounts have overdue balances. The scam was reported by a parent, and district spokesperson Sarah Hackett confirmed that the message did not originate from the school. Research from Keeper Security indicates that 41% of educational institutions have faced AI-generated phishing attempts, with many parents and students reusing passwords across accounts. Hackett noted that the scam did not compromise the district's internet services. The phishing message contained a misspelling of the word 'school,' which was a key indicator of its illegitimacy. Parents are advised to verify unexpected communications and to use strong passwords to protect their accounts.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Paradise Valley Unified School District in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Korean-speaking Hackers Target PHP Vulnerabilities in Global Campaign A cybersecurity report from Cyfirma reveals that attackers, possibly linked to North Korea's Lazarus group, are preparing to exploit critical vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619). These vulnerabilities allow unauthenticated remote code execution, posing a significant threat to government…