 Itsecurityguru
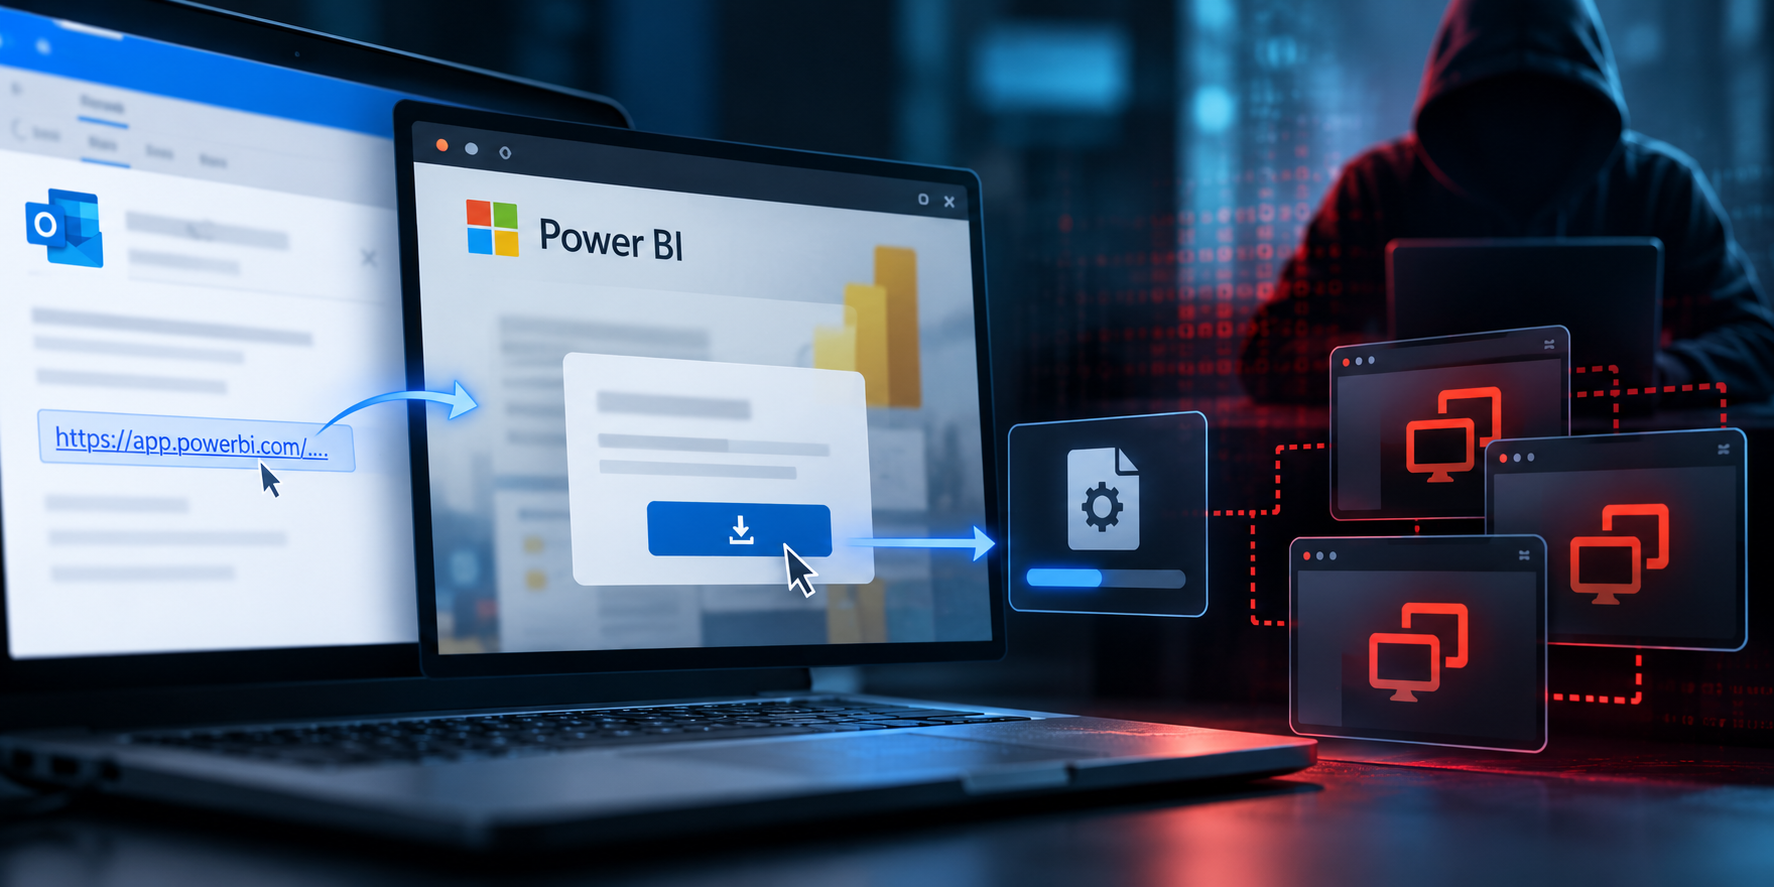
Phishing Campaign Exploits Power BI to Deploy Rogue RMMs
Article Content

- •Attackers exploit Microsoft Power BI to bypass email security in phishing campaigns.
- •Victims are directed to malicious sites that fingerprint their systems before downloading malware.
- •Multiple rogue ScreenConnect clients are deployed to maintain persistent access.
A phishing campaign has been identified that abuses Microsoft Power BI to deliver rogue ScreenConnect remote monitoring and management (RMM) clients. The campaign, first observed on September 10, 2026, uses legitimate Power BI dashboards as phishing lures, allowing attackers to bypass email security measures. Victims receive Outlook phishing emails with links to a fake document hosted on a trusted Power BI domain. Clicking the 'Download Reference' button leads to an attacker-controlled site that performs extensive fingerprinting of the victim's system. The campaign has impacted multiple endpoints, with a retroactive threat hunt revealing 22 additional affected systems. Attackers deploy multiple RMM clients to maintain persistent access, employing techniques to evade detection. Huntress has shut down the attack, but organizations are advised to enhance their phishing protections and monitor for unexpected ScreenConnect installations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What systems are affected by this campaign?
How can organizations protect themselves?
What should I do if I suspect an infection?
Continue Reading
 Critical Citrix NetScaler Vulnerabilities Actively Exploited in Finland The National Cyber Security Centre Finland (NCSC-FI) issued an alert regarding critical vulnerabilities in Citrix NetScaler ADC and Gateway products, specifically CVE-2026-88771 and CVE-2026-88772, which are being actively exploited in Finland. These vulnerabilities allow attackers to execute remote code without…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on…