 Nine.Au
Princess Märtha Louise Denounces Deepfake Pregnancy Rumors
Article Content

- •Princess Märtha Louise faced false pregnancy rumors due to AI-generated deepfake images.
- •Meta removed the accounts spreading the deepfakes for breaching its guidelines.
- •This incident is part of a broader trend of AI misuse targeting royal families.
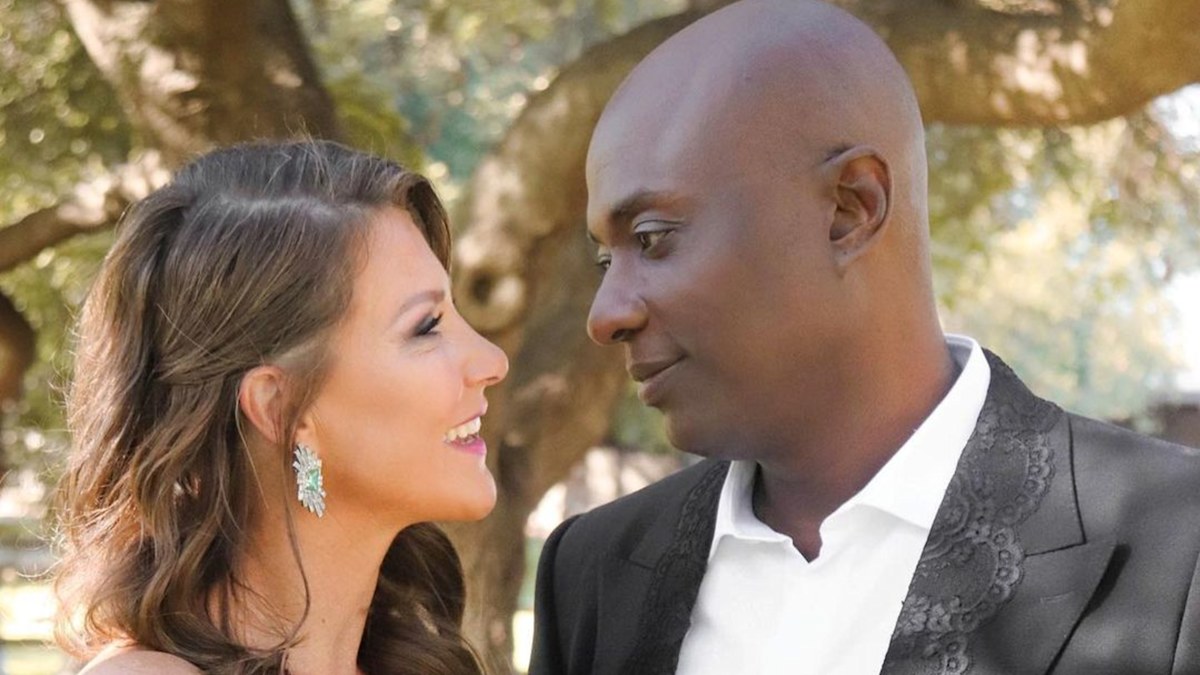
Norway’s Princess Märtha Louise has publicly condemned false pregnancy claims stemming from AI-generated deepfake images of her with a baby bump. The images, which surfaced on two social media accounts in Norwegian and German, were removed by Meta for violating guidelines on coordinated inauthentic behavior. The royal's spokesperson confirmed the images were manipulated and stated that they are taking the matter seriously. This incident follows a similar attack on the Norwegian royal family in June, where AI-generated images of then-Crown Princess Mette-Marit were circulated online. Princess Märtha Louise, who married American shaman Durek Verrett in 2024, has faced ongoing scrutiny and controversy since their union. The couple remains prominent figures in Norway's royal family despite public backlash.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Meta in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What actions are being taken against the deepfake creators?
What is the public reaction to the deepfake images?
Have similar incidents occurred before?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…