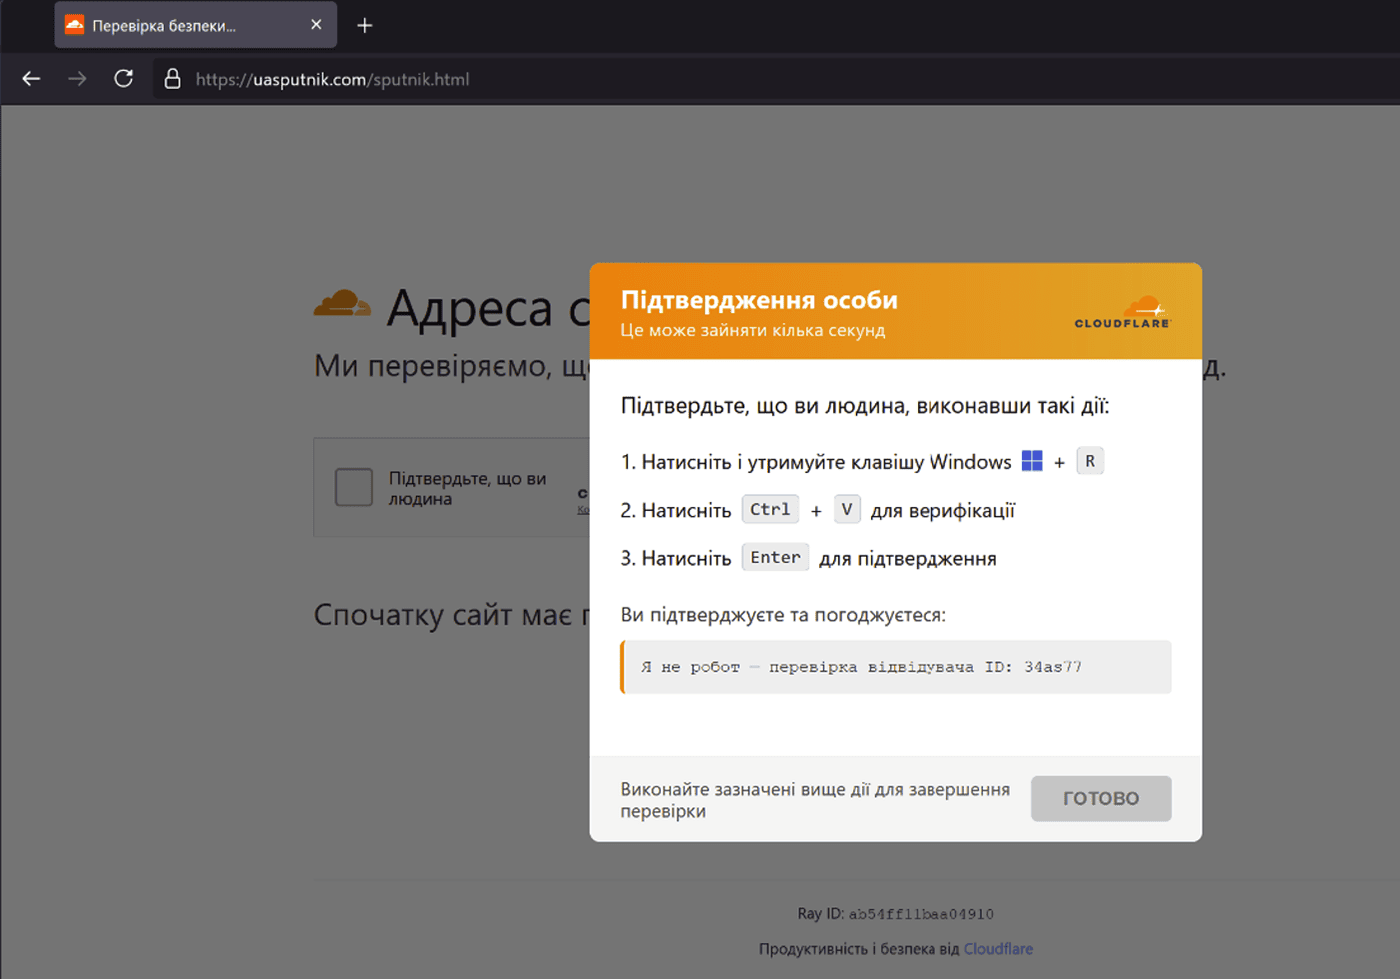
 Securityaffairs
Psychedelic Stealer Campaign Targets Ukrainian Websites with Fake CAPTCHA
Article Content

- •Psychedelic Stealer is distributed via compromised Ukrainian websites using a fake CAPTCHA.
- •The malware targets browser credentials and cryptocurrency data, employing a stealthy installation method.
- •The campaign has impacted users across 32 countries, primarily in Ukraine.
A new malware campaign named Psychedelic Stealer is exploiting compromised Ukrainian business websites to deliver a fake Cloudflare CAPTCHA. This lure, presented through injected iframes, directs users to execute a Windows Installer command that downloads the malware. The campaign has affected visitors from 32 countries, with a significant number of interactions recorded from Ukraine. The malware targets sensitive data, including browser passwords and cryptocurrency wallet information, and establishes persistence through scheduled tasks. The attack method bypasses traditional security measures by avoiding PowerShell and using msiexec instead. The lure management panel revealed extensive telemetry data, but it does not confirm successful malware execution. The campaign leverages trusted websites, making it harder for users to identify the threat. As of now, the attack continues, with ongoing monitoring by Arctic Wolf Labs.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Psychedelic Stealer in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Active Exploitation of Siemens Software Center Vulnerability in ClickFix Campaign Siemens has confirmed that a DLL side-loading vulnerability (CVE-2026-110936) in Siemens Software Center is actively being exploited in malware attacks. The vulnerability allows attackers to execute malicious code by placing a specially crafted DLL in a directory searched by the application. Siemens first disclosed…
 Latrodectus Malware: New Windows Loader Threat Discovered Latrodectus, also known as BlackWidow and IceNova, is a Windows malware loader identified in October 2023. It acts as a backdoor, enabling attackers to download and execute additional malicious payloads. This malware primarily spreads through email campaigns and is linked to the LUNAR SPIDER group, known for…