 qcentroid.xyz
Quantum ML Challenge Highlights DDoS Detection Limitations
Article Content

- •The ETH Quantum Hackathon focused on DDoS detection using quantum machine learning.
- •Classical techniques outperformed quantum methods in clean data scenarios.
- •Quantum methods may excel in complex, ambiguous attack situations.
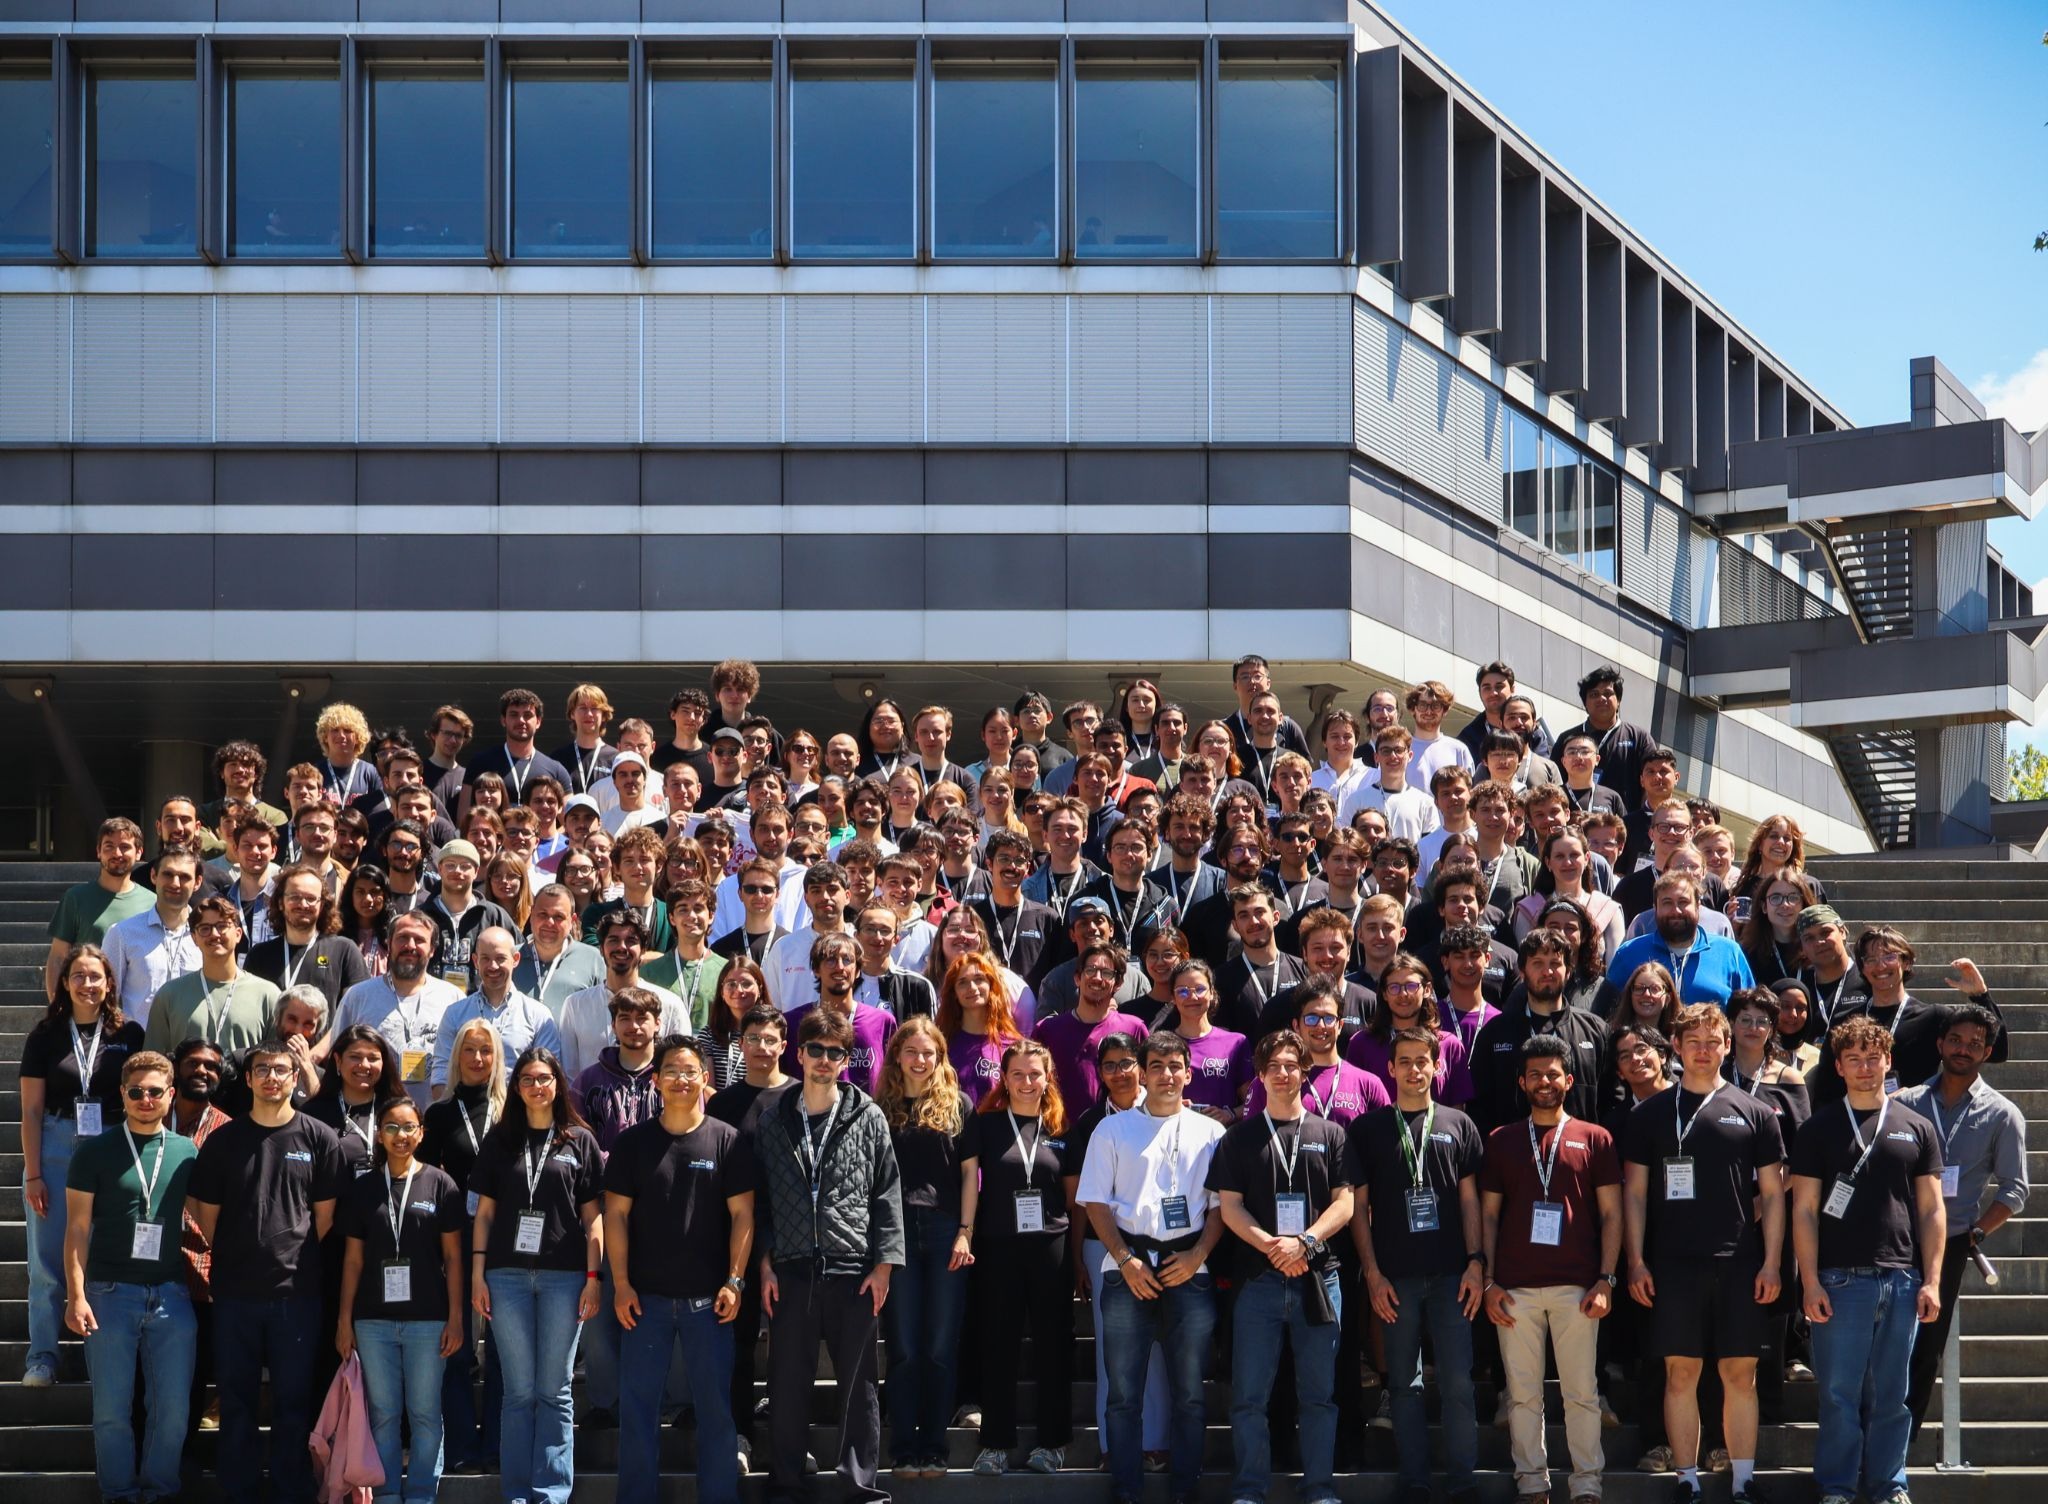
From May 8-10, 2026, the GSMA and QCentroid hosted a challenge at the ETH Quantum Hackathon in Zürich, focusing on using quantum machine learning to detect distributed denial of service (DDoS) attacks. Teams analyzed network telemetry data modeled after a university campus network, simulating two attack patterns: internal machines flooding a target and cloud-hosted bots. Participants were tasked with identifying attack windows and source IP addresses, while being judged on their methodological justification for using quantum techniques. Results indicated that classical methods were more effective with clean data, but quantum methods showed potential in complex scenarios with limited datasets or novel attack types. The findings suggest that while quantum ML has promise, it currently does not surpass classical methods in straightforward applications. The event provided insights into the current limitations and potential future directions for quantum machine learning in cybersecurity.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What were the main tasks for the teams?
How did quantum methods perform?
What insights were gained from the hackathon?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…