 Newsable.Asianetnews
Recruiter Exposes Deepfake Candidate Using Live Face Filter in Interview
Article Content

- •A recruiter caught a candidate using a live face filter during a virtual interview.
- •The incident highlights potential AI misuse in recruitment processes.
- •The recruiter demonstrated the candidate's suspicious behavior in a viral video.
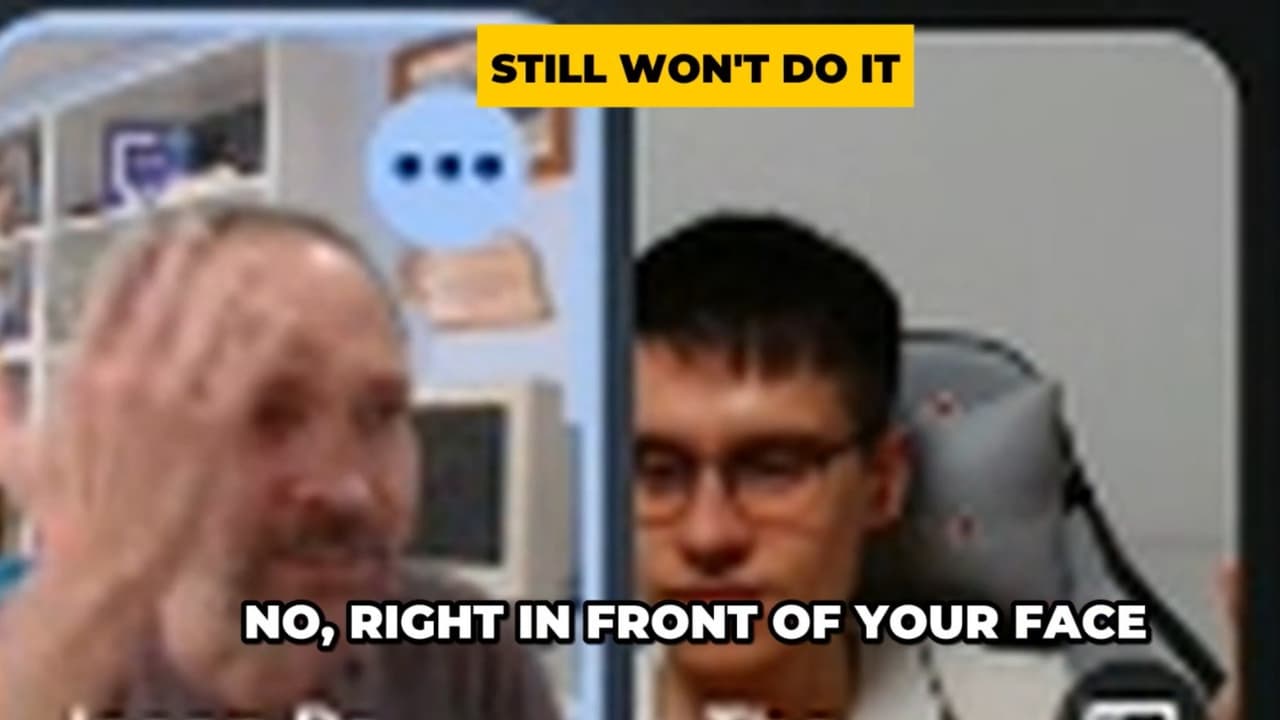
A recruiter, Jason, reported encountering a candidate using a live face filter during a virtual job interview. This incident, which he described as his first experience with a 'deepfake candidate', raised concerns about the misuse of AI in recruitment. The recruiter noticed discrepancies in the candidate's appearance compared to their online profiles, particularly regarding their glasses. A colleague pointed out that the candidate's glasses appeared distorted, indicating a filter was in use. To confirm his suspicions, Jason asked the candidate to place their hand in front of their face, but the candidate avoided doing so. This interaction was captured on video and has since gone viral, igniting discussions about identity verification in remote hiring. The recruiter expressed frustration over the evolving nature of recruitment in the age of AI, emphasizing the need for more in-person interviews.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What should recruiters look for in virtual interviews?
How can AI misuse affect hiring?
What steps can be taken to verify candidate identities?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…