 Bleepingcomputer
RondoDox Botnet Exploits React2Shell Flaw in Next.js Servers
Article Content
Browse articles 
The RondoDox botnet has been exploiting the React2Shell flaw (CVE-2025-55182) to infect vulnerable .js servers with malware and cryptominers. First documented by Fortinet in July 2025, the botnet targets multiple n-day vulnerabilities, including a critical RCE vulnerability in the XWiki Platform identified by VulnCheck in November 2025.
Ask AI about this cluster
Answers cite the sources they use
Updated 229d ago How this analysis works
More articles in this cluster (1)
Following this threat?
Track EtherRAT and CVE-2025-24893 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
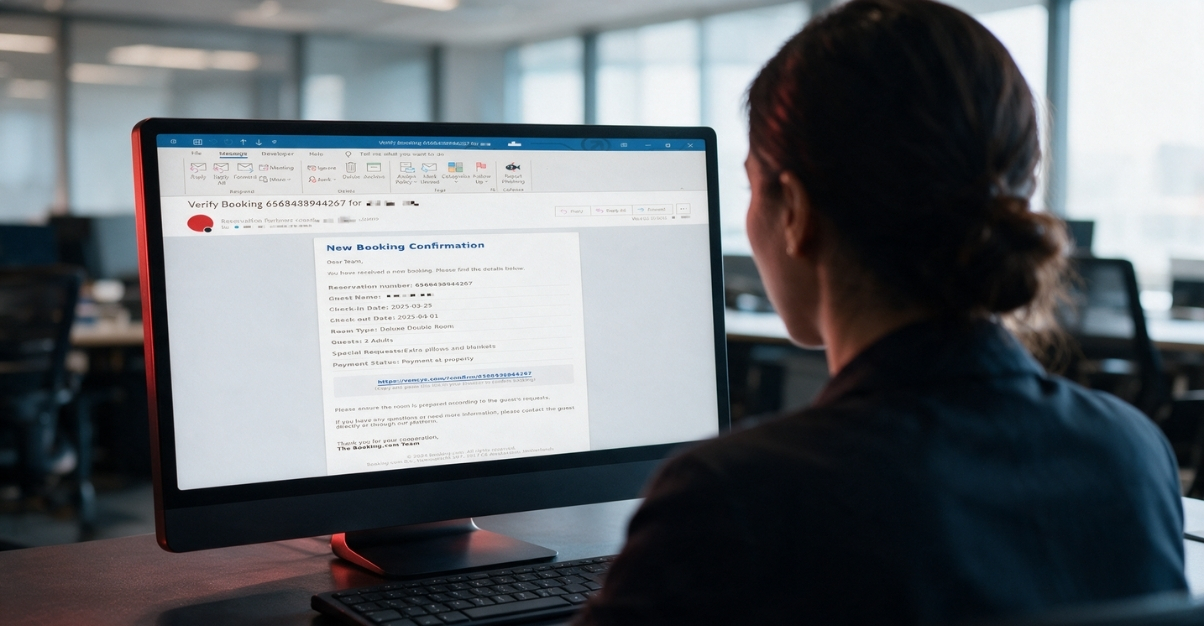 Hackers Exploit Fake Hotel Complaints to Distribute Blockchain Malware Hackers are targeting hotels with fake guest complaints and negative reviews to spread EtherRAT and TONResolver malware. The attacks involve phishing emails that trick hotel staff into downloading malicious LNK files disguised as image files. These malware families utilize public blockchains to locate their…
 PHP Vulnerability Sparks Widespread Cybersecurity Concerns A critical PHP vulnerability has been disclosed, prompting warnings from cybersecurity experts about potential exploits. The PHP Foundation acknowledged a delay in addressing this flaw, which could leave numerous smaller websites vulnerable for weeks. Mitchell Amador, CEO of Immunefi, described the situation as a…