 Independent
Finnish Court Sentences Crew for Undersea Cable Damage
Article Content

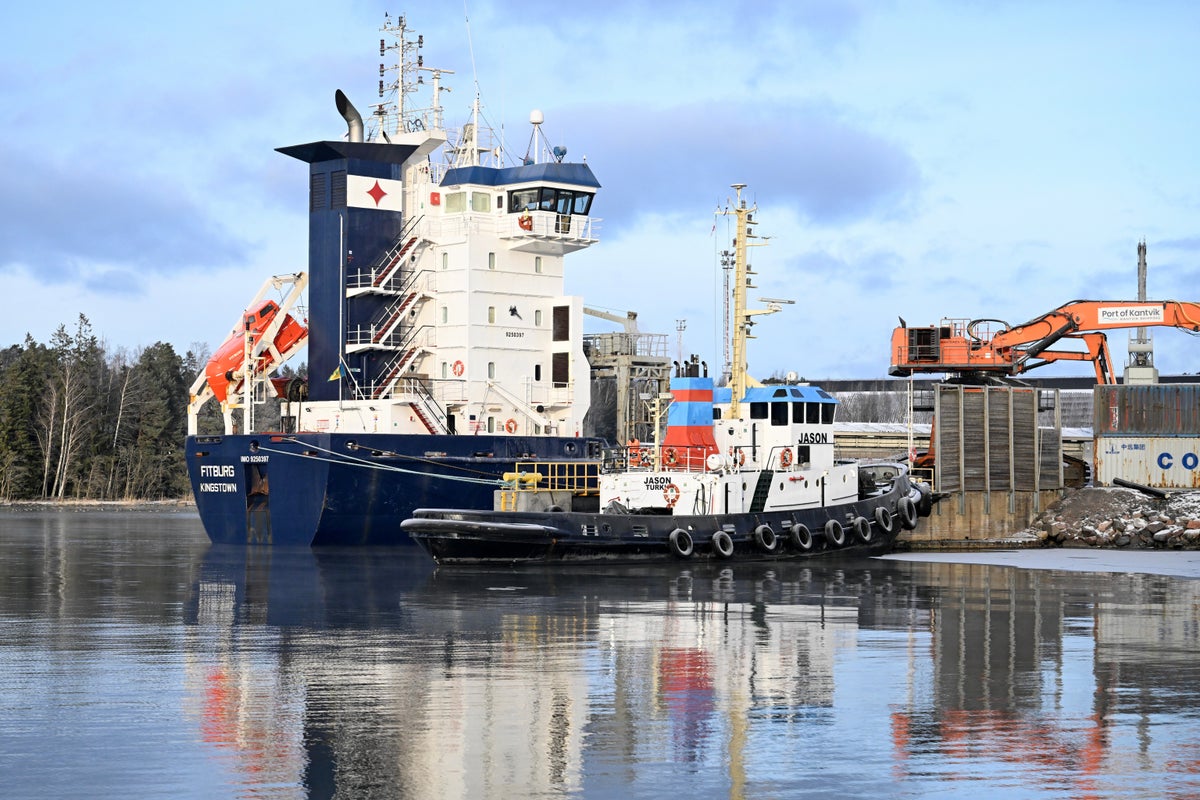
- •The Fitburg damaged two undersea telecommunications cables in the Gulf of Finland.
- •The court ruled the crew must have known the anchor was dragging, leading to their convictions.
- •This incident is part of a broader concern over undersea cable security linked to geopolitical tensions.
A Finnish court has sentenced Russian captain Andrei Maksimenko to three years and six months, and Azerbaijani boatswain Vusal Majidov to two years and ten months for aggravated criminal damage to undersea telecommunications cables. The incident occurred on December 31, 2025, when the cargo ship Fitburg dragged its anchor along the seabed for approximately 130 kilometers, damaging two cables and risking further damage to additional infrastructure. Both men denied wrongdoing, claiming uncertainty about the ship's actions. The court found that they must have known the anchor was down while sailing in Finland's exclusive economic zone. They were also ordered to jointly compensate for repair costs amounting to around €1.9 million. The ruling can be appealed, and the case is part of heightened scrutiny over undersea infrastructure security amid geopolitical tensions involving Russia.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track Elisa in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What were the sentences given?
What damages were caused?
Can the ruling be appealed?
Continue Reading
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…
 Chinese Actor Compromises US Government Networks via PHP2Shell Exploit A suspected Chinese nation-state actor exploited vulnerabilities in Palo Alto Networks firewalls using a chained PHP2Shell exploit and a Linux kernel privilege escalation flaw. The attack, which began on October 23, targeted 25 servers across the US, Japan, Taiwan, and South Korea, with a focus on US…