 Sammyguru
Samsung Releases One UI 9 with Vulnerabilities in October Security Update
Article Content

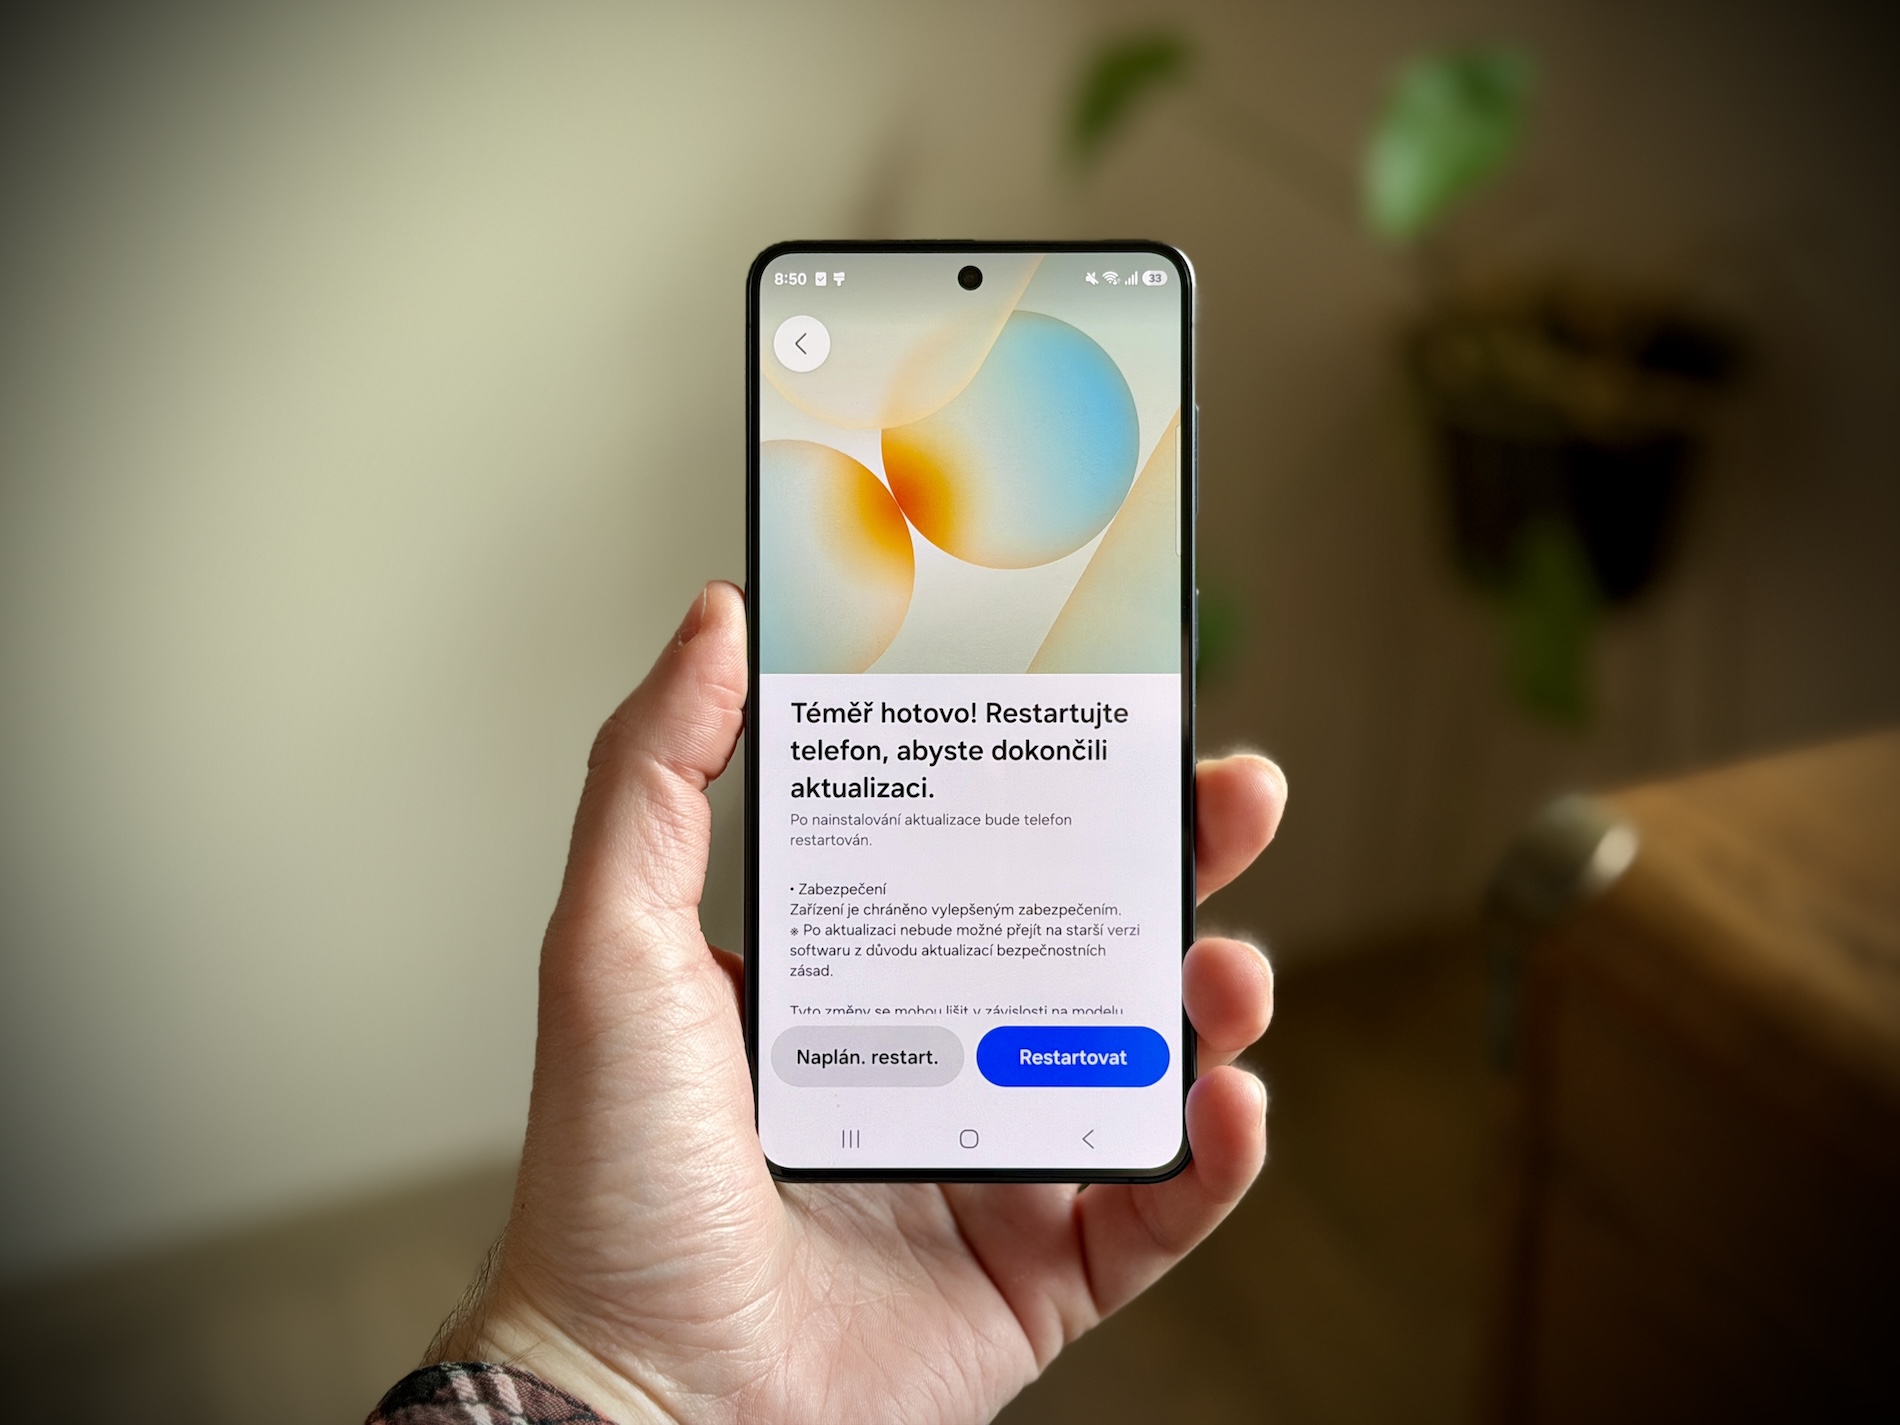
- •Samsung's October update includes One UI 9 for 28 devices.
- •Nine vulnerabilities are rated critically dangerous, including CVE-2026-20519 and CVE-2026-20520.
- •The update addresses serious memory errors and a use-after-free vulnerability in the WSM service.
Samsung has rolled out One UI 9 for 28 devices, including Galaxy A and M series phones, as part of its October 2026 security update. This update addresses 83 vulnerabilities, with nine rated as critically dangerous, including CVE-2026-20519 and CVE-2026-20520, both published on October 5, 2026. The vulnerabilities include serious memory errors and a use-after-free vulnerability in the WSM service, which could allow local attackers to execute code with system privileges. Samsung has also released beta updates for several Galaxy Watch models. Users of the Galaxy S23 series are receiving their last major update unless further updates are provided. The update is crucial for maintaining device security as it addresses high-severity vulnerabilities that could be exploited if not patched.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track CVE-2026-20519 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Which devices received the One UI 9 update?
What vulnerabilities are included in the October update?
How urgent is it to apply the October security update?
Continue Reading
 Samsung October 2026 Update Addresses 83 Vulnerabilities Samsung's October 2026 security update, released on October 6, addresses 83 vulnerabilities across its Galaxy devices. This includes nine Android vulnerabilities, with CVEs such as CVE-2026-20519 and CVE-2026-20520, and 33 high-severity flaws. The update also includes four high-severity patches from Samsung…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…