 Ground.News
Sauron Loader Malware Targets German Organizations via DLL Side-Loading
Article Content

- •Sauron Loader is used in targeted attacks on German organizations.
- •The malware utilizes DLL side-loading and in-memory decryption to evade detection.
- •It operates as a final stage in social engineering attack chains.
Sauron Loader, a new malware loader, has been identified in attacks against German organizations. It operates as a final stage in intrusion chains initiated through social engineering and ClickFix campaigns. The malware is distributed via malicious MSI packages and is designed to gather telemetry from host systems and execute additional malware. Analysts from DCSO linked the loader to underground sales posts targeting Russian-speaking criminals. The malware employs DLL side-loading and in-memory decryption techniques to evade detection, complicating traditional security measures. Current investigations have not quantified the number of affected systems or identified all final payloads. The loader can create scheduled tasks to maintain persistence on infected machines. Security products like Symantec's Carbon Black are reportedly capable of blocking associated malicious indicators.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track ClickFix in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Russia's AI-Driven Cyber Espionage Targets Ukraine and Europe A Russian-linked hacking group, identified as GTG-20006, has utilized Anthropic's Claude AI to automate cyber espionage against over 20 organizations, primarily in Ukraine and Europe. The group targeted Ukrainian government officials, military personnel, and drone manufacturers through sophisticated phishing and…
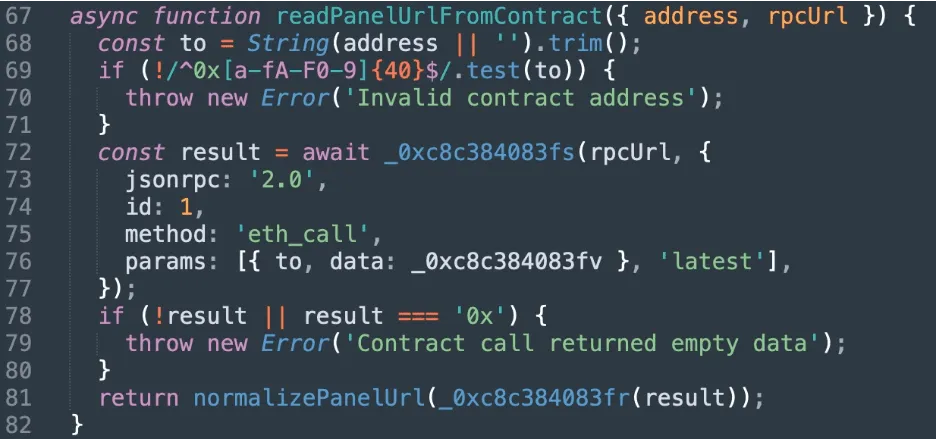 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…