 Vancouversun
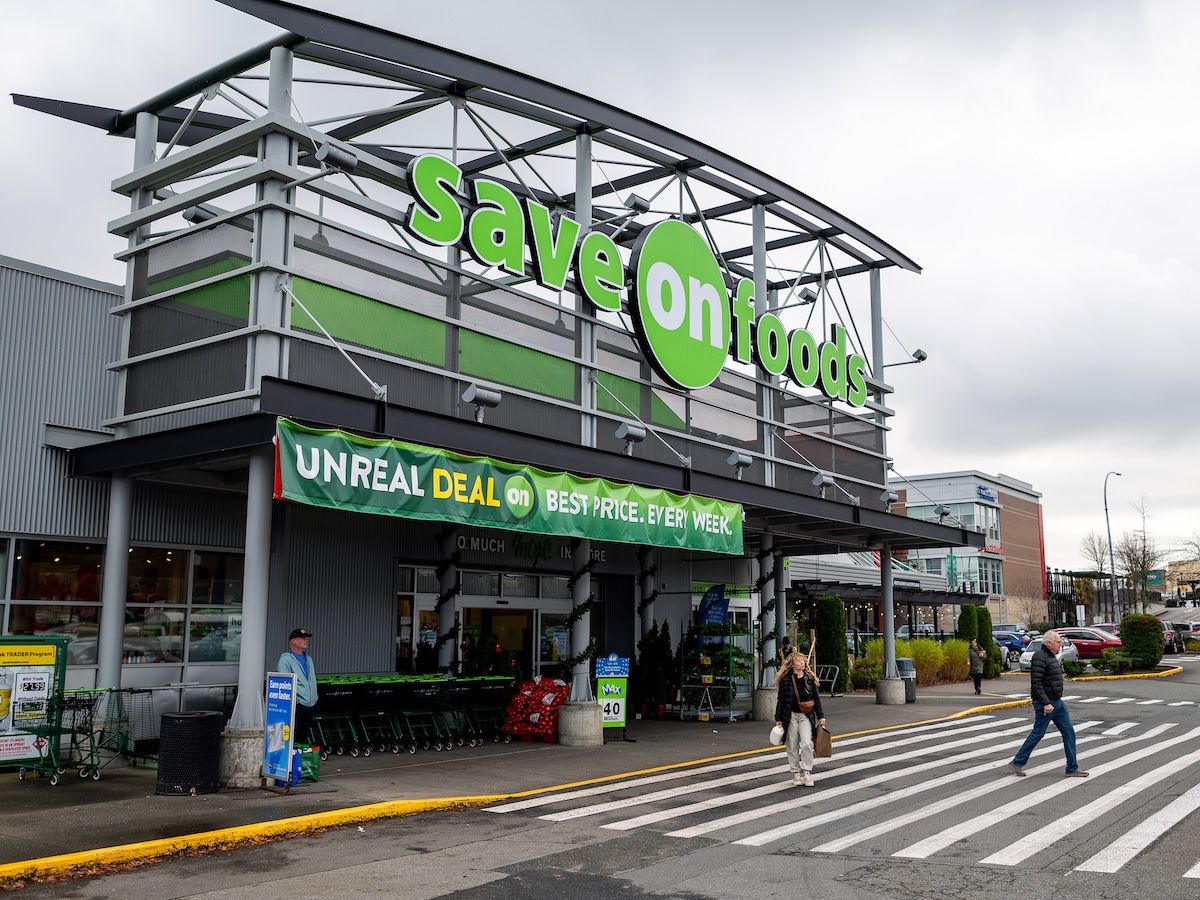
Save-On-Foods Rewards System Breach Exposes Customer Data
Article Content

- •Thousands of customers affected by the breach of Save-On-Foods' rewards system.
- •Personal information accessed includes names, addresses, and dates of birth.
- •No financial data like credit card information was compromised.
Save-On-Foods reported a breach affecting thousands of customers, with unauthorized access to personal information in its rewards system. The company detected the breach on October 13, 2026, and took immediate action to shut down the affected server. Customers were notified on October 14, 2026, that their names, addresses, phone numbers, email addresses, and dates of birth were accessed. The company confirmed that no sensitive financial information, such as credit card data or transaction history, was compromised. An investigation is underway with a third-party cybersecurity expert. Save-On-Foods has advised customers to be vigilant against phishing attempts following the breach. The exact number of affected customers and the full scope of the breach remain undisclosed.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Buy-Low Foods in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What personal information was compromised?
Is financial information at risk?
What should affected customers do?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…