 www.manifold.security
Scams Exploit Placeholder Domains in AI Agent Skills
Article Content

- •Two placeholder domains redirect macOS users to scams.
- •Static checks failed to detect malicious redirects due to JavaScript execution.
- •The issue affects 359,000 GitHub files and 349 AI agent skills.
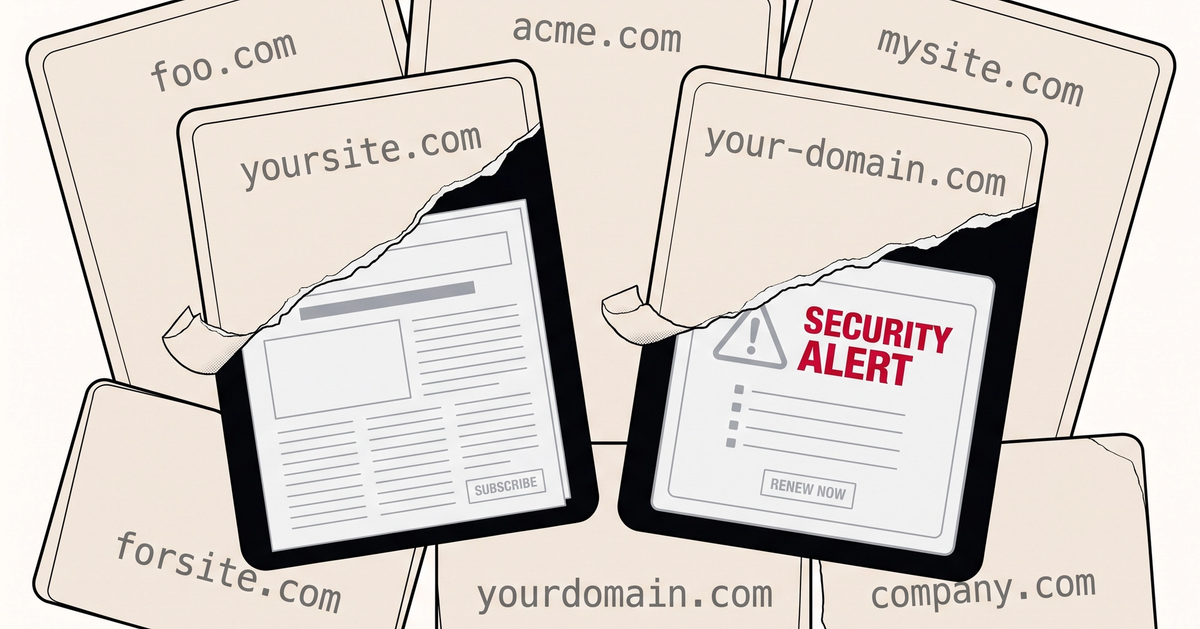
Manifold Security discovered that unreserved placeholder domains, specifically yoursite.com and your-domain.com, are redirecting macOS users to scams. These domains, found in 359,000 GitHub files and cited by 349 AI agent skills, serve cloaked scam redirects without any changes to the original code. Researchers tested these domains across 24 real-browser sessions, where two visits led to scam pages while others ended on parking or ad pages. The scams included a fake 'MacOS Security Center' warning and counterfeit news articles promoting investment schemes. Static checks failed to identify the malicious redirects, which only activated after JavaScript execution in a real browser. This issue highlights the risks associated with using non-reserved domains in software documentation. The findings follow a previous disclosure about another placeholder domain, third-party.com, which was turned into a ClickFix lure targeting Windows users.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track ClickFix and Manifold Security in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Active Exploitation of Siemens Software Center Vulnerability in ClickFix Campaign Siemens has confirmed that a DLL side-loading vulnerability (CVE-2026-110936) in Siemens Software Center is actively being exploited in malware attacks. The vulnerability allows attackers to execute malicious code by placing a specially crafted DLL in a directory searched by the application. Siemens first disclosed…
 ClickFix Technique Surges with AI Lures in Cyber Attacks ClickFix has emerged as a dominant cyber attack technique since 2024, now accounting for over 52% of Push's detections. This method has evolved to include sub-techniques like InstallFix and ConsentFix, with attackers increasingly using AI tools as bait. In Q2 2026, ClickFix detections reached 67%, surpassing other…