 www.siemshipping.com
Siem Industries Orders Two Offshore Subsea Construction Vessels
Article Content

- •Siem Industries ordered two OSCVs for delivery in 2029 and 2030.
- •Each vessel will be equipped with advanced AHC cranes for subsea operations.
- •The design emphasizes energy efficiency and operational flexibility.
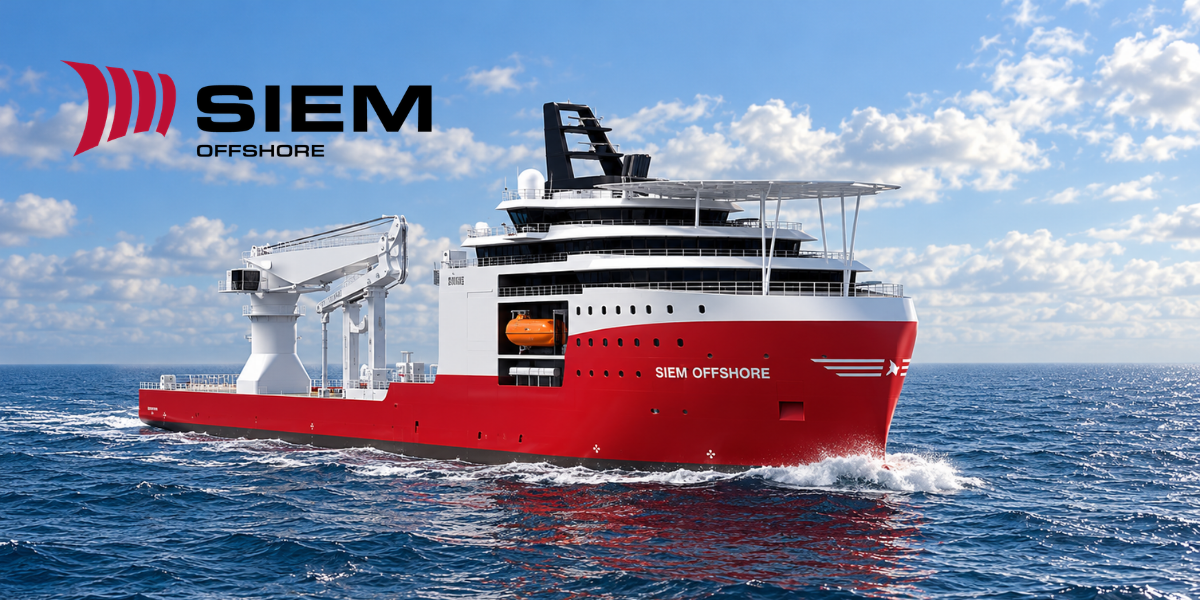
Siem Industries has placed an order for two Offshore Subsea Construction Vessels (OSCVs) at Fujian Mawei Shipbuilding in China, with deliveries expected in 2029 and 2030. Each vessel will feature a 400-tonne active heave compensation (AHC) crane and a 50-tonne AHC crane, enhancing their lifting capabilities for subsea operations. The vessels, designed by Sirius Design & Integration, will measure approximately 145 meters in length and 27 meters in beam, focusing on operational flexibility and energy efficiency. This order signifies Siem's ongoing commitment to the offshore subsea sector, leveraging their extensive experience in specialized offshore vessel operations. The cranes will be manufactured by Huisman, incorporating advanced features such as LiDAR-based collision avoidance and eco-mode functionality.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What are the specifications of the new vessels?
Who is manufacturing the cranes for these vessels?
When are the vessels expected to be delivered?
Continue Reading
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…