 Gbhackers
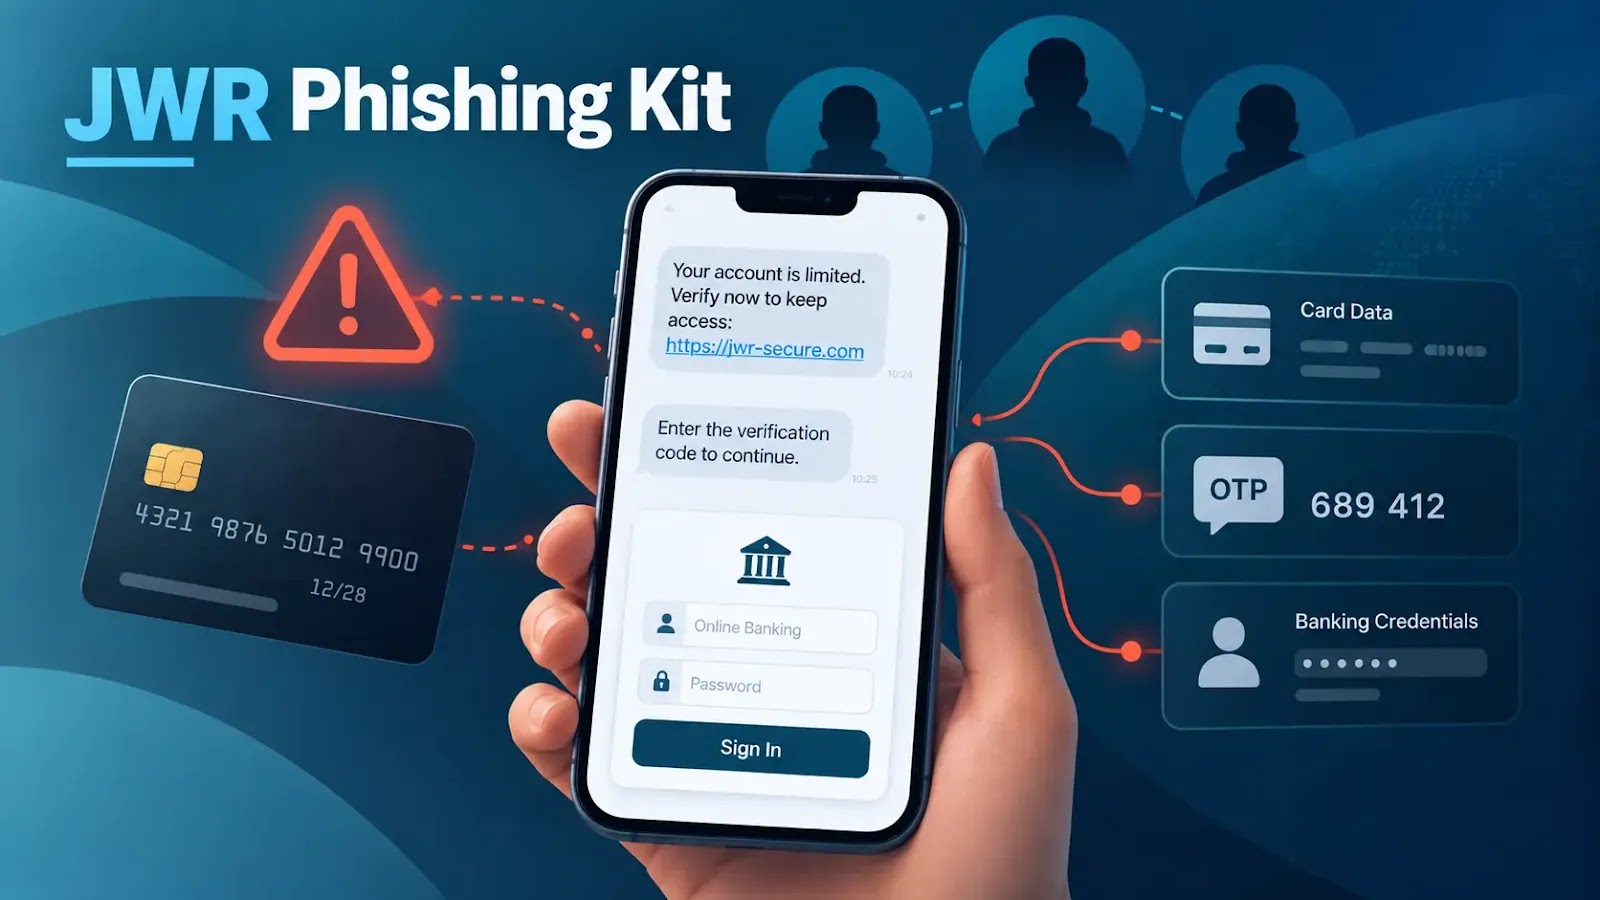
Smishing Triad's JWR Kit Targets Victims via SMS Phishing
Article Content

- •The JWR phishing kit is used in a large-scale smishing campaign targeting sensitive information.
- •Victims are lured through SMS messages impersonating trusted entities, leading to phishing domains.
- •The Smishing Triad operates as a marketplace, with various actors involved in the phishing ecosystem.
A large-scale smishing campaign has been linked to the Smishing Triad, utilizing the JWR phishing kit to steal sensitive information including payment card data, OTPs, and online banking credentials. Victims receive fraudulent SMS messages impersonating trusted entities, prompting them to click on links that lead to disposable phishing domains. The JWR kit operates as a real-time fraud platform, allowing operators to dynamically adjust the phishing flow based on victim responses. Group-IB has attributed this activity to an operator sub-cluster known as Outsider, which participates in a broader phishing-as-a-service ecosystem. The campaign has affected numerous individuals across multiple countries, with the potential for significant financial losses. The JWR kit is noted for its sophisticated architecture, employing Vue 2 single-page applications and encrypted WebSocket communications for data exfiltration. This ongoing threat highlights the need for enhanced public awareness and defensive measures against smishing attacks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Noodle RAT and Shopify in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical GitLab Vulnerabilities Exploited Within Hours of Disclosure On September 10, 2026, GitLab released patches for critical vulnerabilities CVE-2026-85706 and CVE-2026-87719. CVE-2026-85706, a path traversal flaw, allows unauthenticated users to read arbitrary files from GitLab servers, while CVE-2026-87719 enables credential theft via insecure deserialization. Both…