 Koreaherald
South Korea's Major Banks Face Hacking Breach Investigation
Article Content

- •16 financial institutions, including major banks, were affected by the hacking incidents.
- •Approximately 100,000 personal records were exposed during the breaches.
- •Bank CEOs have pledged to improve cybersecurity measures and utilize AI technologies.
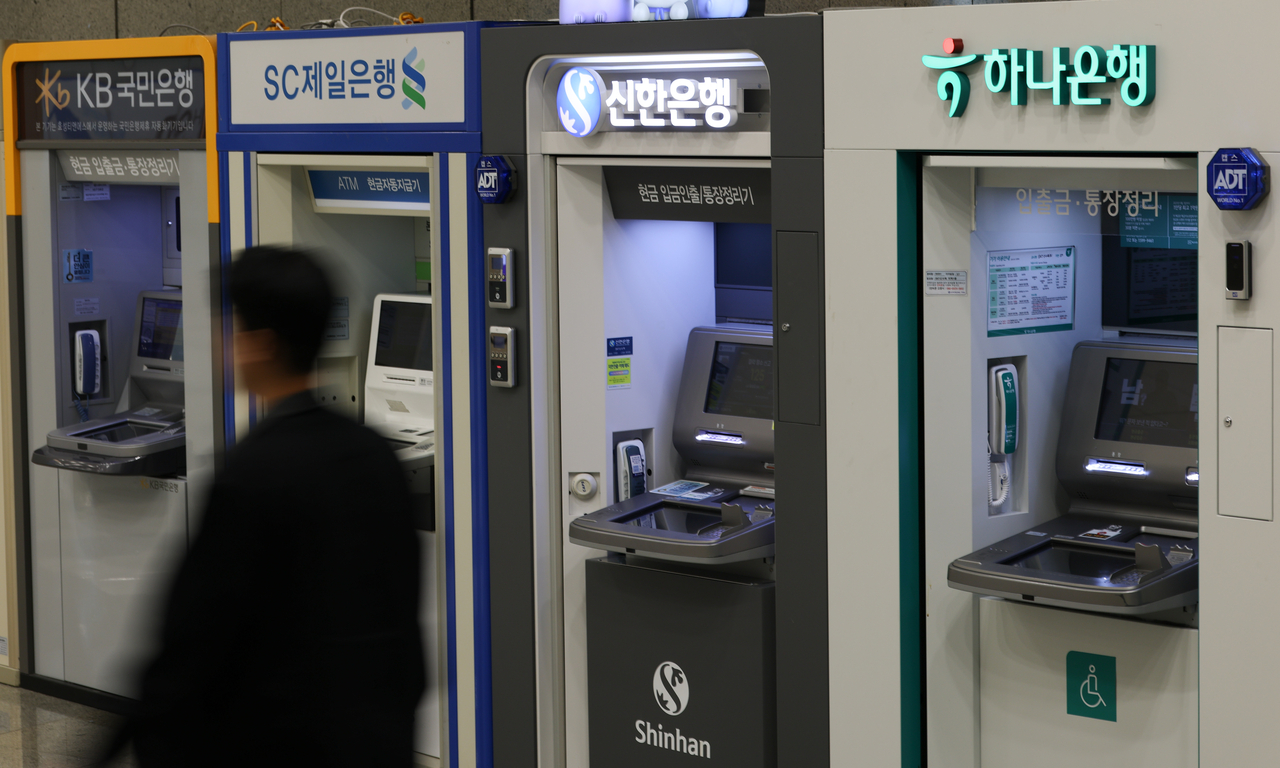
South Korean police plan to refer hacking cases involving major banks to the Serious Crimes Investigation Agency after identifying potential violations of financial security laws. The breaches have affected 16 financial institutions, exposing approximately 100,000 personal records. The targeted systems primarily involved internal networks rather than core banking infrastructure, complicating jurisdictional issues. The Financial Services Commission has indicated that these cases may fall under the Electronic Financial Transactions Act, prompting further investigation. The National Office of Investigation has expanded its team to 43 investigators and is conducting a broader review of cybersecurity across the financial sector. In a related development, the CEOs of the top five banks publicly apologized for the breaches and committed to enhancing security measures, including the use of AI-driven systems.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track BNK Busan Bank in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What financial institutions are affected?
What measures are being taken to enhance security?
What is the current status of the investigation?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…