 Globaltimes.Cn
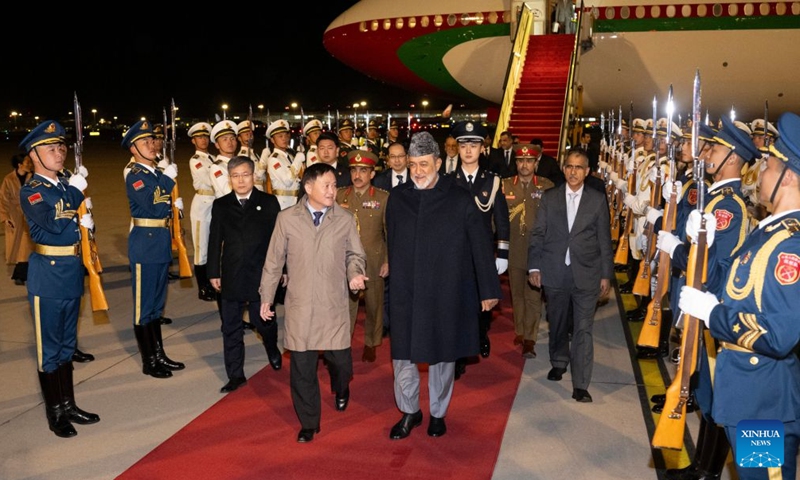
Sultan of Oman Begins Historic State Visit to China
Article Content

- •Sultan Haitham's visit is the first by an Omani head of state to China since 1978.
- •The visit aims to enhance cooperation in trade, investment, and cultural exchanges.
- •Oman seeks stronger ties with China amid rising geopolitical tensions in the Middle East.
Sultan Haitham Bin Tarik Al Said of Oman arrived in Beijing on November 1, 2026, marking the first visit by an Omani head of state to China since diplomatic ties were established in 1978. This visit is significant for enhancing bilateral relations and cooperation across various sectors, including trade, investment, and cultural exchanges. Chinese Foreign Ministry spokesperson Guo Jiakun emphasized the importance of this visit in advancing the strategic partnership between China and Oman. Analysts suggest that Oman seeks to strengthen its ties with China amid evolving geopolitical tensions in the Middle East. The visit is expected to promote cooperation in trade and set a positive example for regional collaboration. The Oman Observer noted that this visit opens new avenues for cooperation in political, economic, and scientific fields, reflecting Oman's strategy to diversify its partnerships. The historical context of Omani-Chinese relations spans over 1,200 years, rooted in maritime trade and cultural exchanges.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Common questions
What is the significance of Sultan Haitham's visit?
What sectors will the cooperation focus on?
Why is Oman seeking stronger ties with China now?
Continue Reading
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…
 Chinese Actor Compromises US Government Networks via PHP2Shell Exploit A suspected Chinese nation-state actor exploited vulnerabilities in Palo Alto Networks firewalls using a chained PHP2Shell exploit and a Linux kernel privilege escalation flaw. The attack, which began on October 23, targeted 25 servers across the US, Japan, Taiwan, and South Korea, with a focus on US…