 Aol
Tampa Man Arrested for Dark Web Child Abuse Material and Dolls
Article Content
Browse articles 
- •Brian Boggess, 61, arrested for possessing over 100 illicit files related to child abuse.
- •SWAT team executed the raid on October 17, 2026, based on a tip about dark web activity.
- •Boggess faces multiple charges, including generating child sexual abuse material.
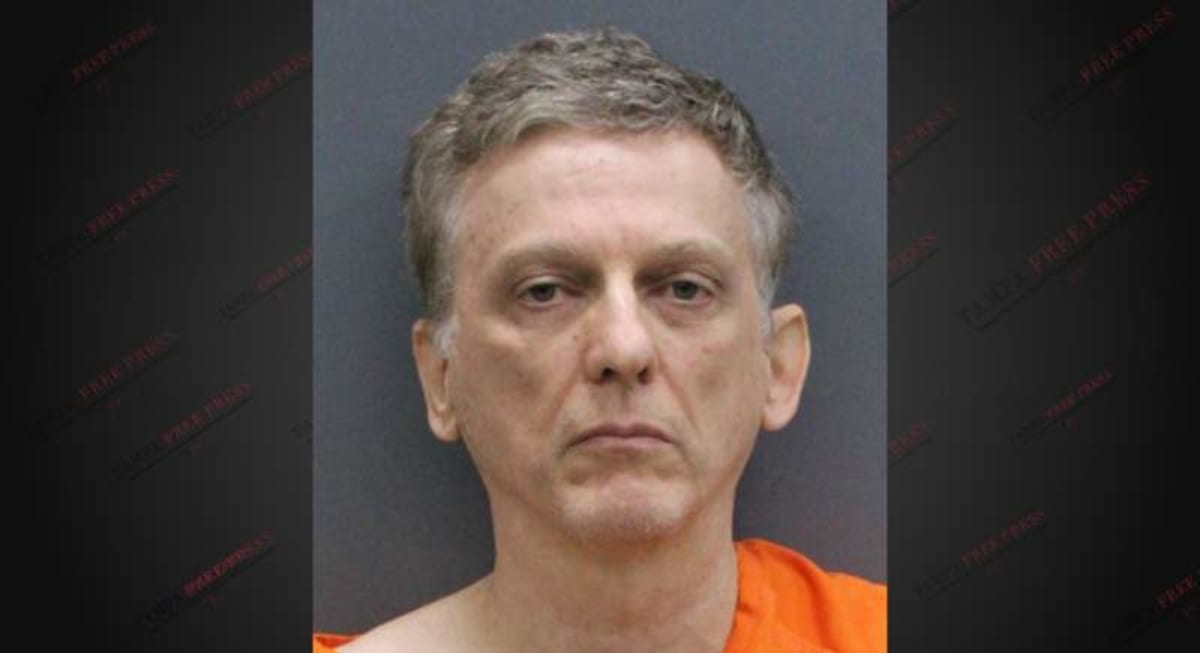
A 61-year-old man from Tampa, Brian Boggess, was arrested following a SWAT raid that uncovered over 100 illicit electronic files related to child sexual abuse and two childlike sex dolls. The Hillsborough County Sheriff’s Office executed the warrant on October 17, 2026, after receiving a tip about child sexual abuse material being downloaded from the dark web. Boggess faces 100 counts of possession of child sexual abuse material, 51 counts of generating such material, and two counts of possession of childlike sex dolls. The investigation is ongoing, and authorities have not disclosed any further details about potential accomplices or additional charges at this time.
Ask AI about this cluster
Answers cite the sources they use
Updated just now How this analysis works
Timeline
2026-10-17
SWAT raid conducted
Hillsborough County Sheriff’s Office executed a warrant at Boggess's residence, leading to his arrest and the discovery of illicit files and dolls.
AolMore articles in this cluster (3)
Common questions
What charges is Brian Boggess facing?
He faces 100 counts of possession of child sexual abuse material, 51 counts of generating such material, and two counts of possession of childlike sex dolls.
What prompted the SWAT raid?
The raid was prompted by a tip-off regarding child sexual abuse material being downloaded from the dark web at Boggess's residence.
Is the investigation ongoing?
Yes, the investigation remains active, and authorities have not disclosed further details about potential accomplices.
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…