 abc7news.com
Teen Loses $58K College Fund in DMV Mercedes-Benz Scam
Article Content

- •California teen lost $58,000 college fund in a car scam involving a DMV title error.
- •The Mercedes-Benz was repossessed by Carvana after Berjis verified the title with the DMV.
- •LAPD is investigating the case, but the seller's identity remains unknown.
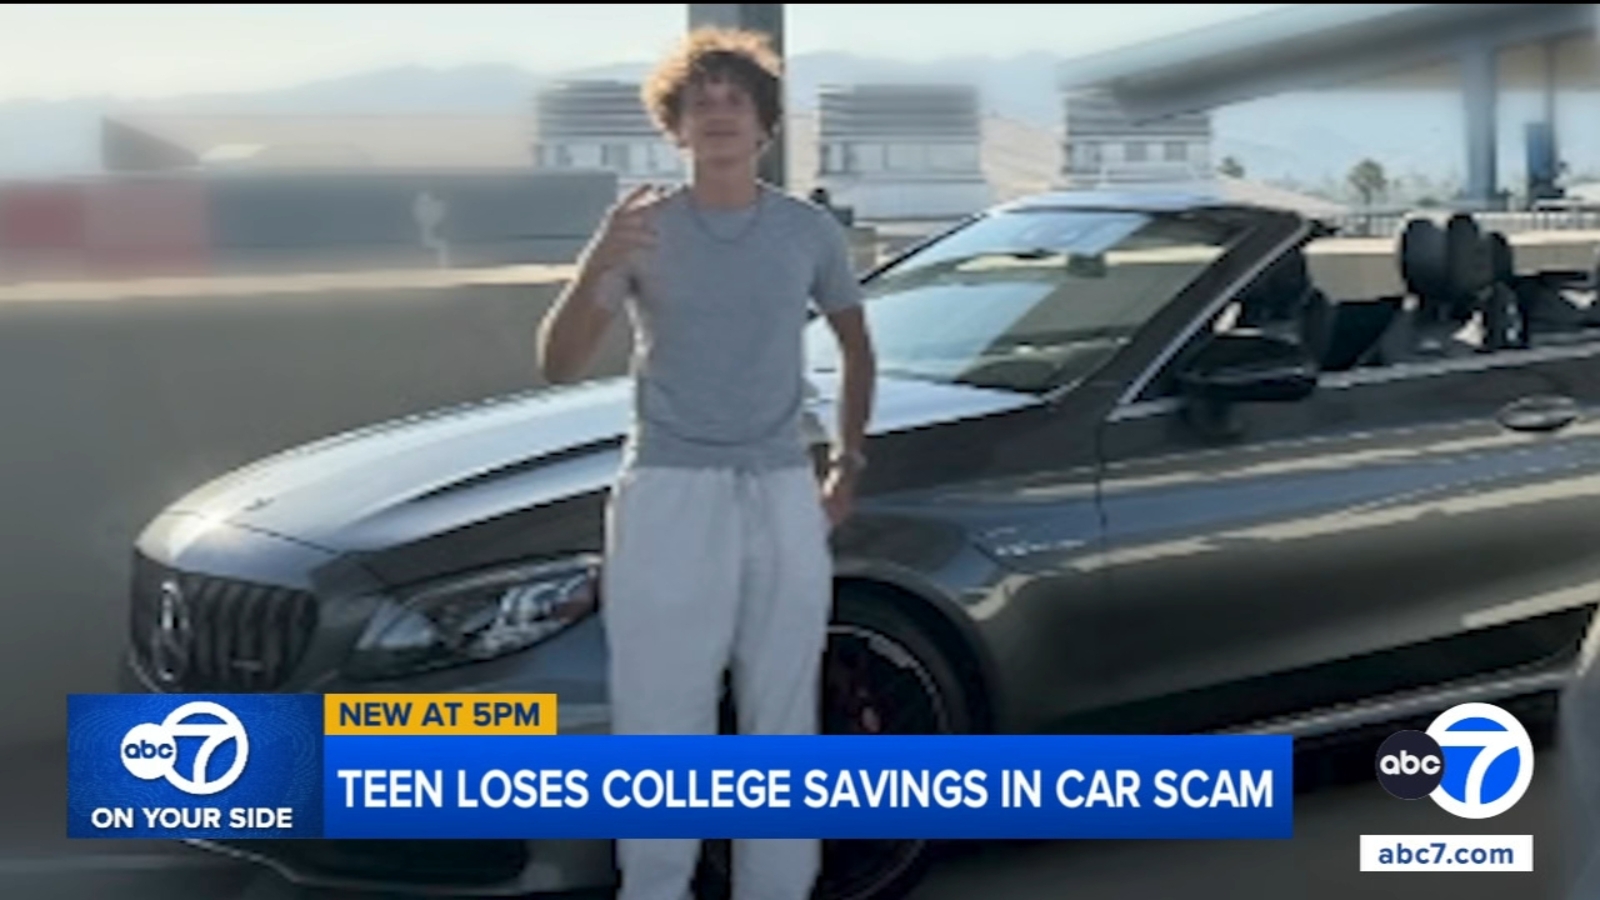
Seventeen-year-old Arrod Berjis from California lost his $58,000 college savings after purchasing a 2019 Mercedes-Benz C63 AMG, which was later repossessed due to a scam involving a DMV title error. Berjis believed the car had a clear title, having verified it with the DMV and obtained a Carfax report showing no liens. After spending three months repairing the vehicle, he found a buyer willing to pay $75,000, but the car was repossessed by Carvana before the sale. The DMV later admitted that paperwork may have been overlooked during the title transfer process. LAPD detectives are investigating the case, but the seller used a fake identity, complicating efforts to locate them. Berjis is now seeking reimbursement from Carvana or the return of his vehicle, fearing that the loss of his savings will delay his college education.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What should I do if I encounter a similar situation?
How can I report a suspected scam?
What are my options if I lose money in a scam?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…