 The420.In
ToddyCat Malware Targets Microsoft Exchange Servers via ProxyLogon Vulnerability
Article Content
Browse articles 
ToddyCat, a cyber espionage group, has been targeting Microsoft Exchange servers since December 2020. The group initially exploited an unidentified vulnerability but significantly ramped up its operations in February 2021 by leveraging the ProxyLogon vulnerability to compromise servers in various high-profile organizations across multiple continents.
Ask AI about this cluster
Answers cite the sources they use
Updated 227d ago How this analysis works
More articles in this cluster (3)
Following this threat?
Track ToddyCat in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
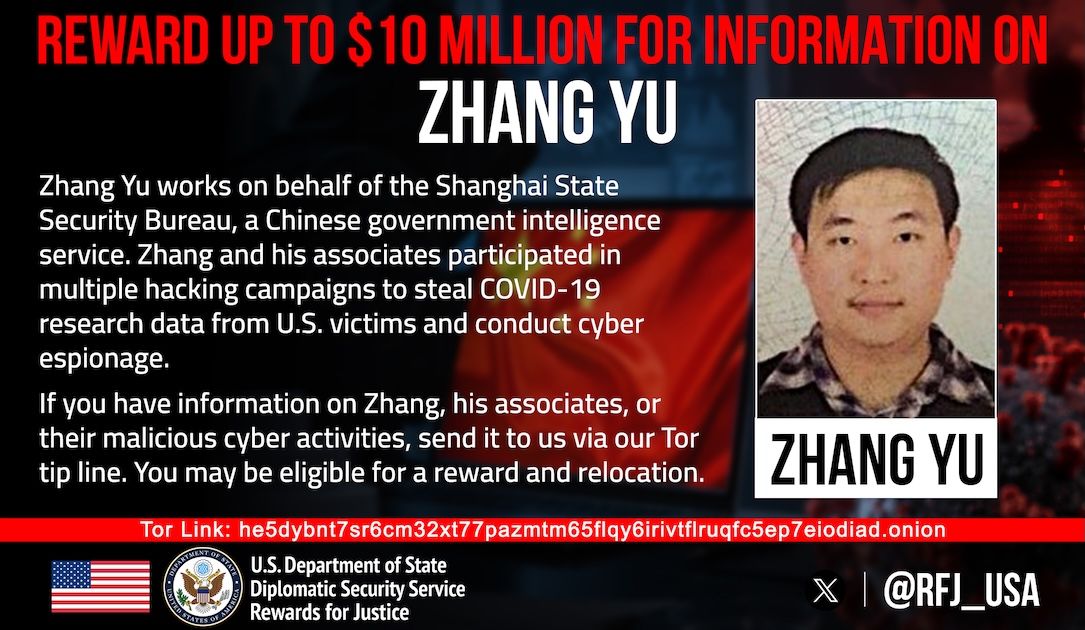 U.S. Offers $10 Million Reward for Zhang Yu, Accused Chinese Hacker The U.S. State Department has announced a reward of up to $10 million for information leading to the identification or location of Zhang Yu, a Chinese national charged with cyberattacks against U.S. COVID-19 research institutions. Zhang is accused of working under the direction of China's Ministry of State Security…
 .NET Vulnerability CVE-2026-111497 Requires Immediate Action On October 25, 2026, Microsoft released out-of-band security updates for.NET addressing CVE-2026-111497, a vulnerability in the Brotli decompression algorithm that allows unauthorized attackers to elevate privileges over a network. The flaw affects.NET versions 8, 9, 10, and 11, particularly in applications that…