 www.foxnews.com
Trump Launches $25M Fraud Whistleblower Program
Article Content

- •Trump's new program offers up to $30,000 for tips on government fraud.
- •The initiative is part of a broader crackdown on taxpayer fraud.
- •Critics question the program's potential conflicts of interest.
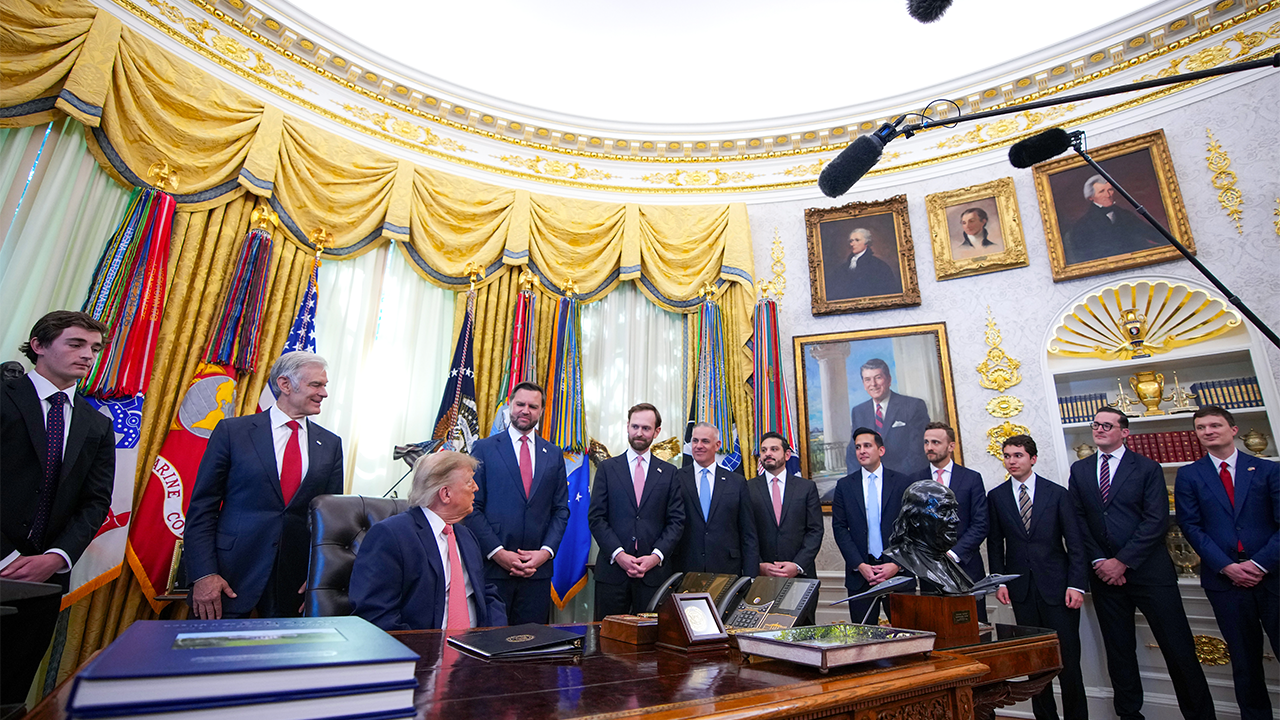
On October 20, 2026, President Donald Trump and Vice President JD Vance announced a $25 million Fraud Whistleblower Incentive Program aimed at encouraging the public to report suspected fraud in federal programs. Individuals providing tips that lead to fraud convictions or significant federal enforcement actions can earn up to $30,000, which is a 1% commission on the fraud amount uncovered. The program will be administered by the Justice Department, and Trump stated he would arbitrate any disputes over claims to rewards. Critics have raised concerns about potential conflicts of interest, given Trump's business ties. The initiative follows previous investigations into alleged fraud in childcare programs, which were highlighted by right-wing influencer Nick Shirley. The White House claims that the program is part of a broader effort to eliminate fraud in government spending.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Common questions
How can I report fraud?
What are the eligibility criteria for rewards?
What is the maximum reward amount?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…