 Kyivindependent
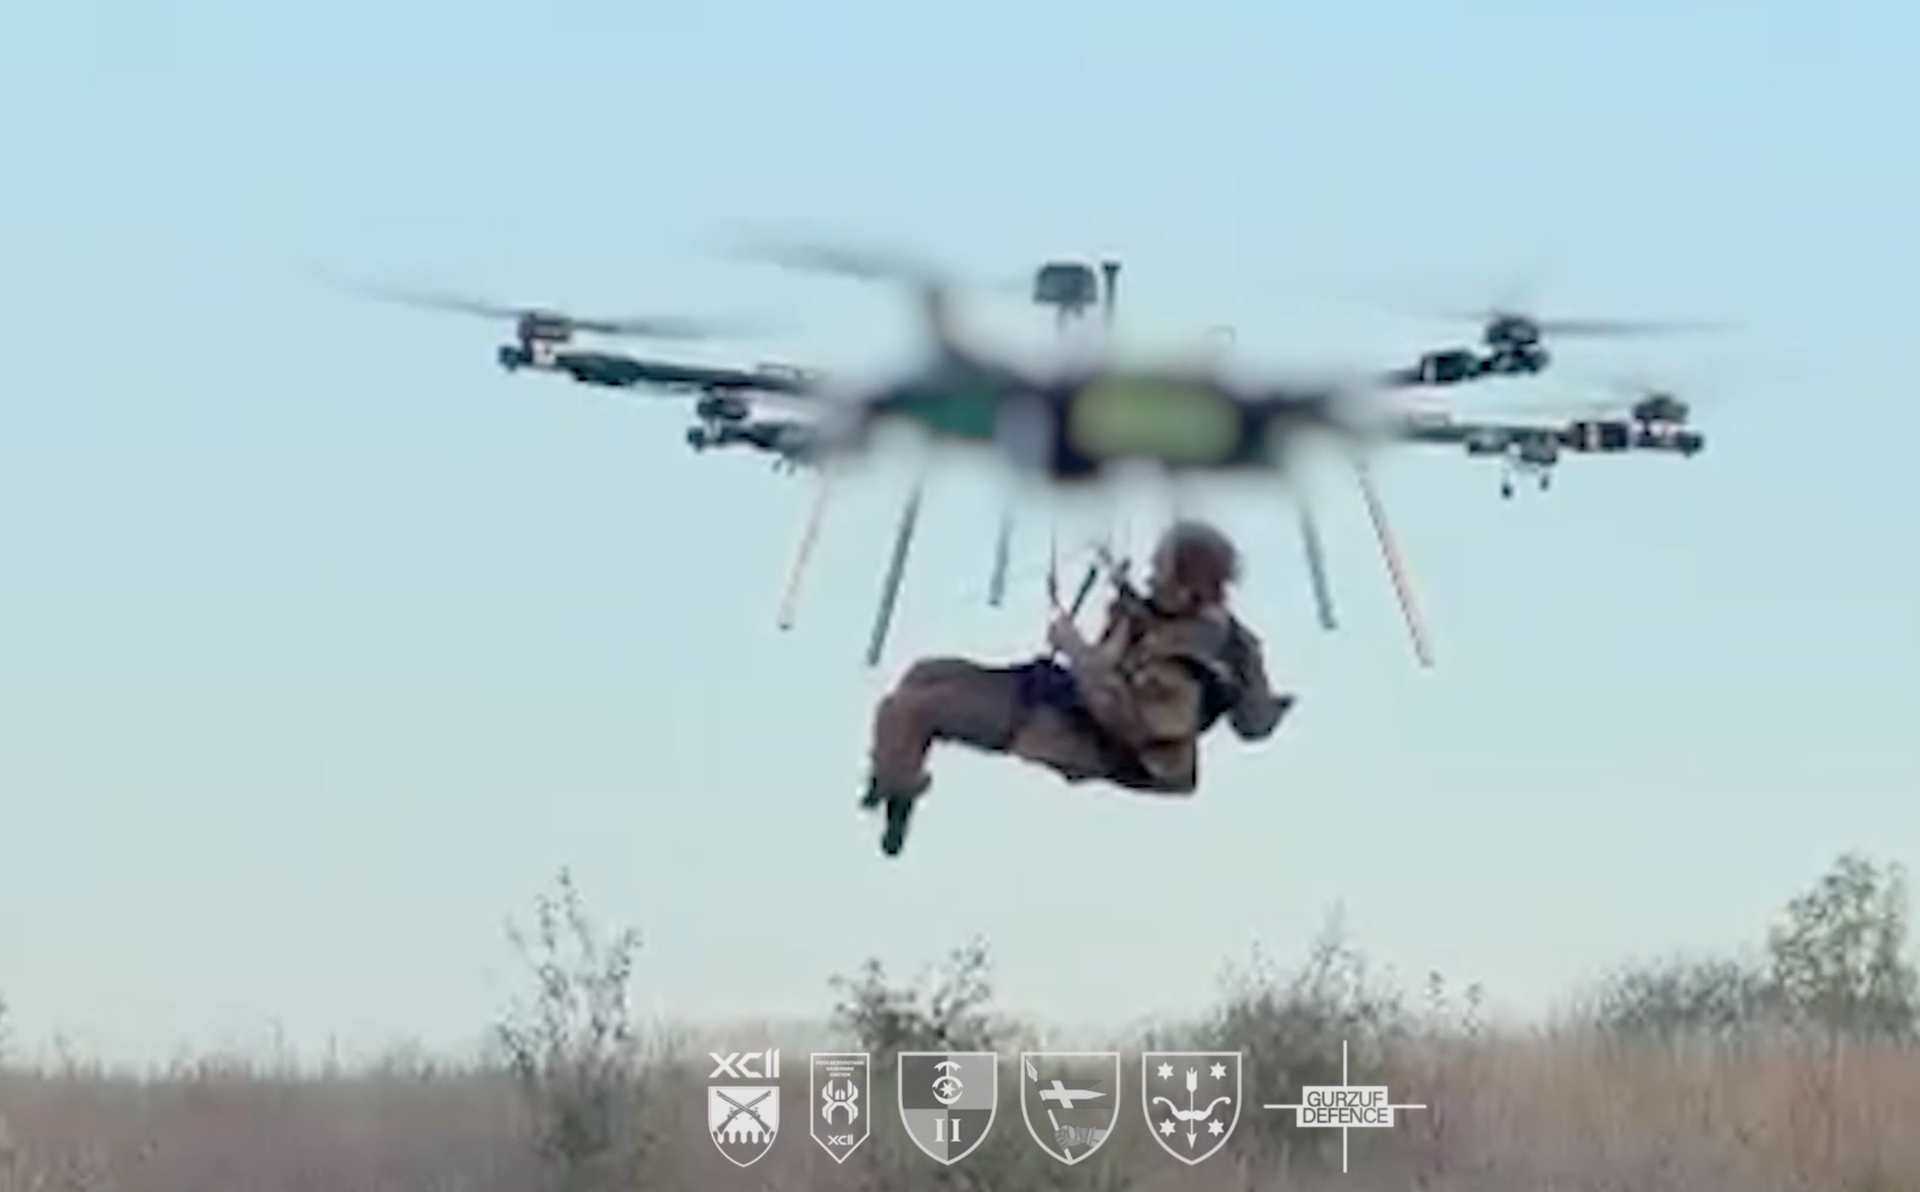
Ukraine Conducts Historic Drone Evacuation of Wounded Soldier
Article Content

- •Ukraine executed the first-ever drone evacuation of a wounded soldier on October 19, 2026.
- •The operation utilized a heavy-lift hexacopter drone, the Ayudag-6, due to unsafe ground conditions.
- •The soldier, after a successful evacuation, is currently receiving treatment and is no longer in danger.
On October 19, 2026, Ukraine's military executed the world's first aerial evacuation of a wounded soldier using a drone, specifically a heavy-lift hexacopter named Ayudag-6, manufactured by Gurzuf Defense. The soldier, identified by the callsign 'Kostya', was severely injured while stationed on the eastern Kharkiv front, where ground evacuation was impossible due to heavy enemy drone activity and mined terrain. The operation involved multiple units, including the 92nd Separate Assault Brigade and the 30th Separate Mechanized Brigade. The drone was equipped with a winch, allowing the soldier to secure himself for the flight, which lasted over an hour and covered 62 kilometers. After the successful evacuation, the soldier is now receiving medical treatment and is no longer in danger. This mission marks a significant advancement in military medical evacuation capabilities, showcasing Ukraine's innovative use of drone technology in warfare.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (9)
Following this threat?
Track Gurzuf Defense in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What drone was used for the evacuation?
Why was ground evacuation impossible?
What is the current status of the evacuated soldier?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…