 unn.ua
Ukraine Increases Support for Energy Workers Amid Ongoing Russian Attacks
Article Content

- •Ukraine has approved a Hr. 30,000 monthly bonus for energy and utility workers.
- •Russian forces are launching 300 to 400 drone attacks daily on Ukrainian infrastructure.
- •The winter season is critical for restoration efforts amid ongoing Russian strikes.
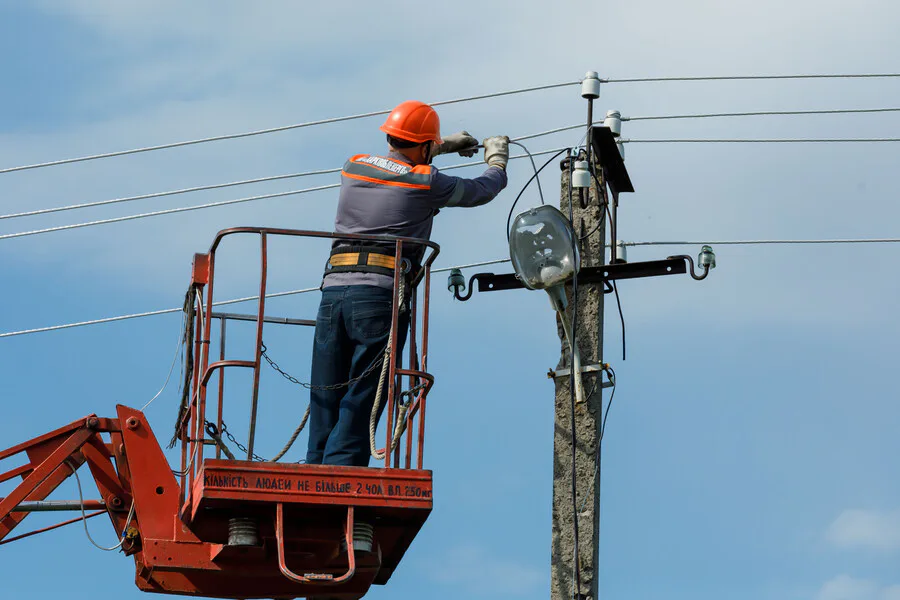
On November 4, 2026, Ukraine's government approved a monthly bonus of Hr. 30,000 ($670) for workers repairing infrastructure damaged by Russian strikes. This decision, announced by Prime Minister Serhii Koretskyi, aims to support energy, utility, and railway workers during the winter heating season. The government previously allocated Hr. 20,000 ($440) for similar efforts last winter. Russian forces have reportedly intensified their attacks, launching 300 to 400 drones daily, with over 2,000 strikes recorded since August. The latest attack on November 3 involved more than 20 strikes on energy facilities within 24 hours. Thousands of energy workers are engaged in restoration efforts under the threat of further attacks, including 'double tap' strikes targeting rescue operations. The situation remains critical as infrastructure continues to be targeted, affecting essential services like electricity and water supply.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track State Emergency Service in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Who qualifies for the new bonuses?
What is the current situation with Russian attacks?
How long will the bonuses be provided?
Continue Reading
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…
 Chinese Actor Compromises US Government Networks via PHP2Shell Exploit A suspected Chinese nation-state actor exploited vulnerabilities in Palo Alto Networks firewalls using a chained PHP2Shell exploit and a Linux kernel privilege escalation flaw. The attack, which began on October 23, targeted 25 servers across the US, Japan, Taiwan, and South Korea, with a focus on US…