 En.Defence-Ua
Ukrainian Forces Strike Russian Warehouse, Prompting Nuclear Speculation
Article Content

- •Ukrainian Special Operations Forces struck a Russian military warehouse on November 2, 2026.
- •The explosion was powerful enough to cause speculation among Russian troops about nuclear involvement.
- •Details on the strike's location and damage remain undisclosed.
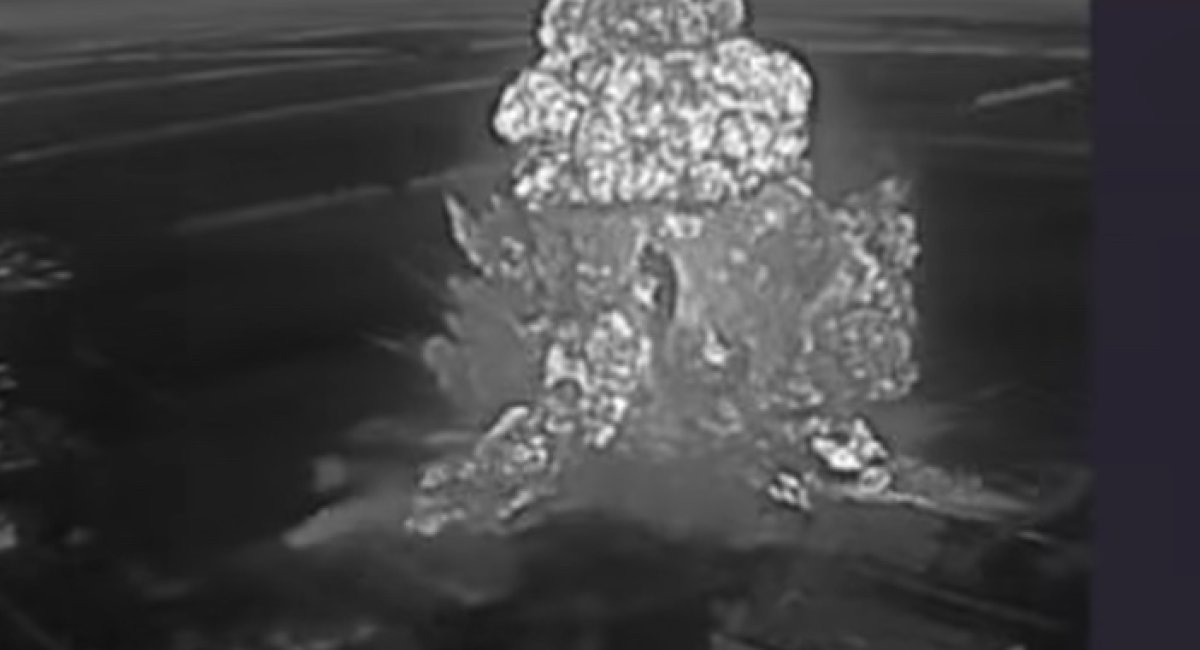
On November 2, 2026, Ukrainian Special Operations Forces targeted a Russian military warehouse, resulting in a massive explosion and subsequent detonations. The strike, carried out by the 73rd Naval Special Operations Center, led Russian troops to speculate about a nuclear weapon being used due to the explosion's intensity. Footage released by the Ukrainian unit shows the explosion and reactions from Russian personnel, with one soldier asking, 'Did they drop a nuke there?!' The exact location and details of the strike, including the type of munitions involved and the extent of damage, remain undisclosed. Earlier reports indicated that Ukrainian forces had successfully engaged numerous Russian targets in the Sumy region, resulting in significant enemy casualties and territorial gains.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What was the target of the Ukrainian strike?
What was the reaction from Russian troops?
What prior operations were reported by Ukraine?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…