 Airandspaceforces
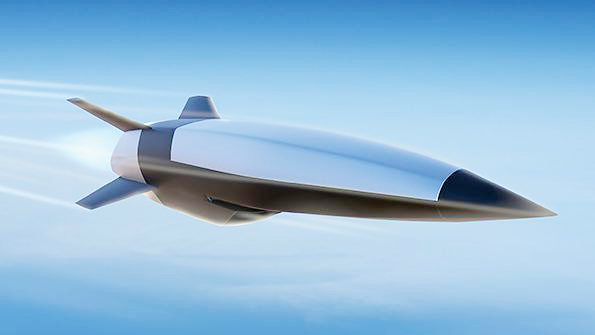
US-Australia Conducts First Flight Test of Hypersonic Attack Cruise Missile
Article Content

- •The HACM flight test marks a significant milestone for U.S.-Australia hypersonic collaboration.
- •The missile is designed to exceed Mach 5 using a scramjet propulsion system.
- •Operational success depends on the ability to protect airbases from Chinese long-range fires.
The U.S. Air Force and Royal Australian Air Force have conducted the first flight test of the Hypersonic Attack Cruise Missile (HACM) over an undisclosed Australian test range. This test is part of the Southern Cross Integrated Flight Research Experiment, aimed at advancing hypersonic capabilities. The HACM, developed by RTX and Northrop Grumman, uses a solid rocket booster and scramjet engine to exceed Mach 5. Despite delays and budget overruns, the Air Force is seeking $1.2 billion for maturation and initial procurement, aiming for fielding in fiscal 2027 and full-rate production by 2029. The operational effectiveness of the HACM hinges on the survivability of allied airbases against Chinese anti-access capabilities. The specific details of the test, including whether the missile achieved powered flight, have not been disclosed.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Northrop Grumman in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is the HACM?
When will HACM be operational?
What challenges does HACM face?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…