 Therecord.Media
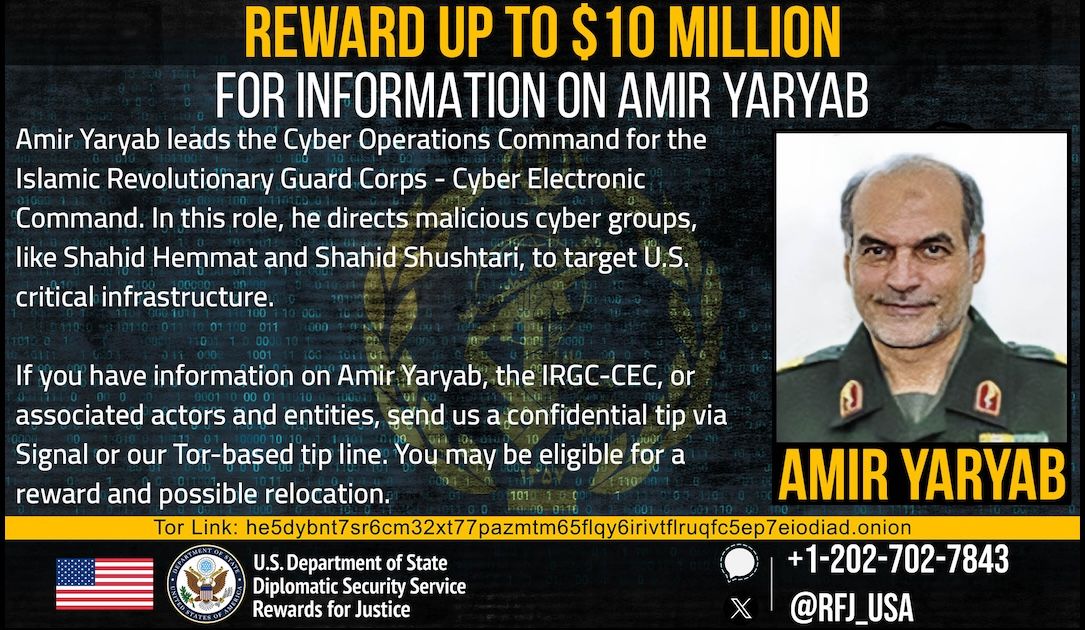
US Offers $10 Million Reward for Iranian Cyber Operations Chief
Article Content

- •A $10 million reward is offered for information on Amir Yaryab, head of IRGC-CEC.
- •Yaryab directs multiple Iranian hacking groups targeting critical infrastructure globally.
- •Recent attacks have compromised over 100 U.S. entities, primarily in the water sector.
The U.S. State Department has announced a $10 million reward for information on Amir Yaryab, a senior official in Iran’s Islamic Revolutionary Guard Corps Cyber-Electronic Command (IRGC-CEC). Yaryab is accused of directing multiple Iranian hacking groups targeting critical infrastructure sectors, including defense, energy, and telecommunications in the U.S., Europe, and the Middle East. His groups, such as CyberAv3ngers, Shahid Hemmat, and Shahid Shoushtari, have utilized malware to compromise civilian infrastructure. Recent attacks have reportedly breached over 100 entities across at least 12 U.S. states, with a focus on the water industry. The U.S. has raised alarms about Iran's resumed cyberattacks since late July 2026, including breaches of email accounts linked to various governmental organizations. The Treasury Department has also sanctioned several Iranian nationals involved in these cyber operations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track X in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Korean-speaking Hackers Target PHP Vulnerabilities in Global Campaign A cybersecurity report from Cyfirma reveals that attackers, possibly linked to North Korea's Lazarus group, are preparing to exploit critical vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619). These vulnerabilities allow unauthenticated remote code execution, posing a significant threat to government…