 Wsvn
U.S. Seizes $2.8M in Fuel Shipments to Sanctioned Cuban Entity
Article Content

- •Federal authorities seized 90 shipments of biodiesel fuel worth $2.8 million destined for Cuba.
- •The shipments were intended for ENETEC, a sanctioned entity linked to the Cuban government.
- •The enforcement action is part of a broader effort to prevent goods from reaching sanctioned entities.
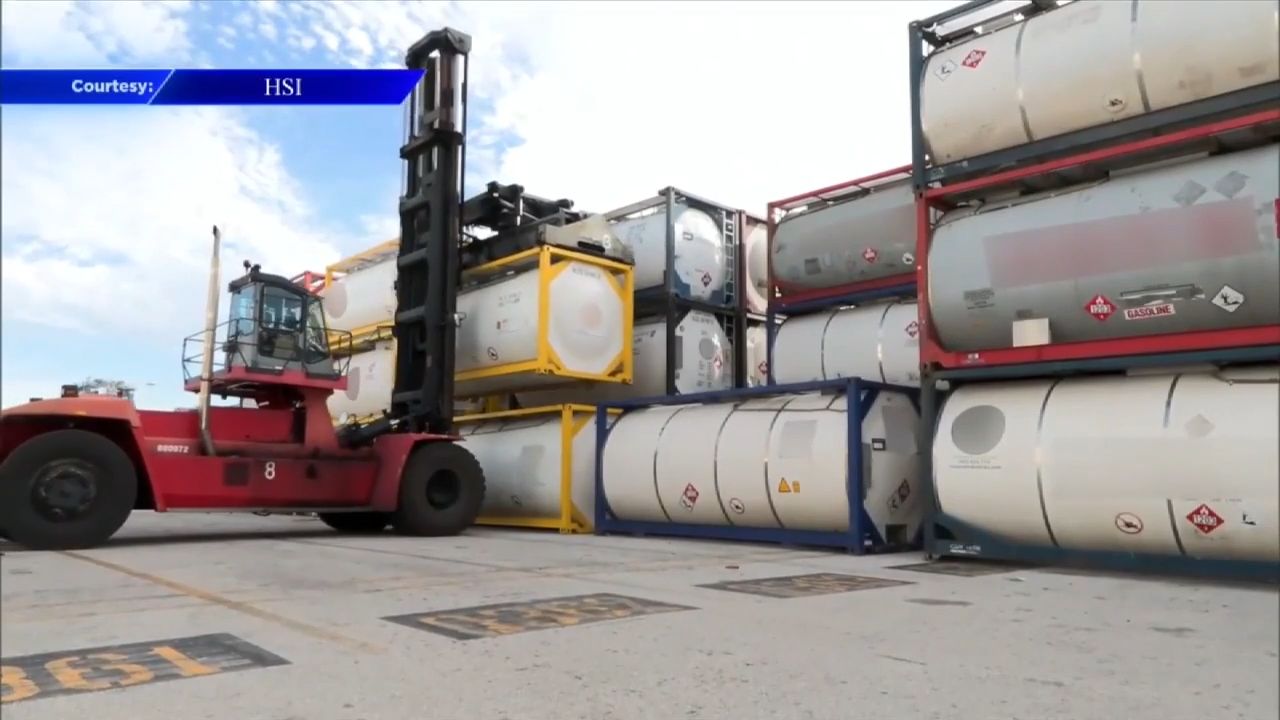
Federal authorities seized approximately $2.8 million worth of biodiesel fuel shipments intended for Cuba, specifically targeting Empresa Nacional de Tanques (ENETEC), a sanctioned Cuban company. The operation involved 90 shipments, with 71 seized at Port Everglades and 19 at the Port of Houston, totaling over 600,000 gallons of fuel. Homeland Security Investigations (HSI) and U.S. Customs and Border Protection (CBP) conducted the enforcement action, citing violations of U.S. export laws and sanctions. The shipments were suspected of benefiting the Cuban government amid ongoing fuel shortages. Authorities emphasized that the seizure does not interfere with legitimate humanitarian assistance to Cuba. The investigation is ongoing, and details about the exporter involved have not been disclosed.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track cuba in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What entity was targeted in the seizure?
How much fuel was seized?
Are there any implications for humanitarian aid?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…